Halloween Special 2026! Get Up to 25% OFF Practice Questions! Limited Time - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

F5 Networks F5CAB5 Exam - Topic 7 Question 10 Discussion

Posted by Kris on May 05, 2026 at 09:19 PM

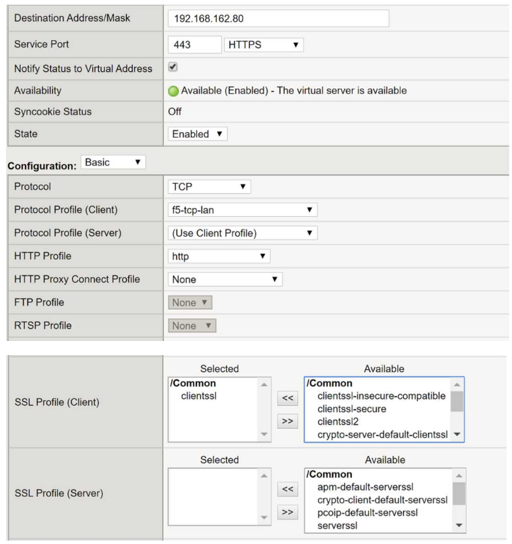
Refer to the exhibit.

A BIG-IP Administrator needs to deploy an application on the BIG-IP system to performSSL offload and re-encrypt the traffic to pool members. During testing, users are unable to connect to the application.

What must the BIG-IP Administrator do to resolve the issue? (Choose one answer)

Suggested Answer: D

To successfully performSSL offload and re-encryptionon a BIG-IP system, the virtual server must be configured withboth a Client SSL profile and a Server SSL profile. The Client SSL profile enables BIG-IP to decrypt inbound HTTPS traffic from clients, while the Server SSL profile is required tore-encrypt traffic before forwarding it to the pool members.

From the exhibit, the virtual server has aClient SSL profile configured, which allows BIG-IP to accept HTTPS connections from clients. However, there isno Server SSL profile attached, meaning BIG-IP attempts to sendunencrypted HTTP trafficto pool members listening on HTTPS (port 443). This protocol mismatch causes the server-side SSL handshake to fail, resulting in users being unable to connect to the application.

This behavior is well documented in BIG-IP SSL troubleshooting guides: when backend servers expect HTTPS, a Server SSL profile is mandatory to establish a secure connection from BIG-IP to the pool members.

The other options are incorrect:

Removing the Client SSL profile (Option A) would break client-side HTTPS.

The server-side TCP profile (Option B) is unrelated to SSL encryption.

Forward Proxy (Option C) is only used for outbound SSL inspection scenarios.

Therefore, configuring anSSL Profile (Server)is the correct and required solution.


Get Premium F5CAB5 Questions as Interactive Web-Based Practice Test or PDF Real Exam Format Detailed Explanations Instant Access Get Your Practice Test
26 comments · newest first
TR
Trinidad 5 days ago
I feel like A could be a quick fix.
CO
Colette 10 days ago
It ensures proper SSL handling for the server.
EN
Enola 15 days ago
Why D?
CO
Colette 20 days ago
I think option D is the best choice.
LE
Lenora 25 days ago
This question is tricky.
DA
Daron 1 month ago
Option A seems risky. Removing the SSL Profile could cause more problems.
FE
Felicitas 1 month ago
I lean towards option B. The Protocol Profile might fix session issues.
KR
Kristian 1 month ago
True, but I feel like the SSL Profile (Server) is more fundamental.
SH
Sharmaine 2 months ago
But what about option C? Enabling Forward Proxy could help too.
LA
Layla 2 months ago
I agree, without it, users can't connect. It's essential for secure traffic.
LA
Laura 2 months ago
I think option D is the best choice. An SSL Profile (Server) is crucial for re-encryption.
FE
Felton 2 months ago
Option A seems risky. Removing the SSL Profile could cause more problems.
GI
Giuseppe 2 months ago
I lean towards option B. The Protocol Profile might fix session issues.
DA
Dannette 2 months ago
True, but I feel like the SSL Profile (Server) is more fundamental.
GE
Gennie 3 months ago
But what about option C? Enabling Forward Proxy could help too.
IR
Ira 3 months ago
I agree, without it, users can't connect. It's essential for secure traffic.
ED
Edmond 3 months ago
I think option D is the best choice. An SSL Profile (Server) is crucial for re-encryption.
LE
Lenny 3 months ago
I'm surprised they didn't check the SSL settings first!
KA
Katina 3 months ago
Wait, why would they use splitsession-default-tcp? Sounds odd.
JU
Jutta 3 months ago
Removing the SSL Profile? That sounds risky.
DA
Dan 4 months ago
I think enabling Forward Proxy is the way to go!
DA
Daniel 4 months ago
They need to configure an SSL Profile (Server) for sure.
CA
Carissa 4 months ago
I’m a bit confused about the Protocol Profile option; I don’t recall it being a common solution for SSL issues.
BA
Barbra 6 months ago
This question seems similar to one we practiced where we had to configure profiles correctly. I wonder if the SSL Profile (Server) is the key here.
BA
Barabara 6 months ago
I'm not entirely sure, but I feel like enabling Forward Proxy in the SSL Profile might be related to how traffic is managed.
RI
Rickie 6 months ago
I think I remember something about needing an SSL Profile for the server to handle the re-encryption properly.
0/2000 characters

Save Cancel