
 MENU

Study the snort rule given below:
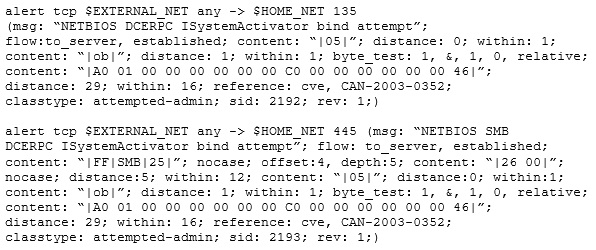
From the options below, choose the exploit against which this rule applies.
Suggested Answer: C
Get Premium 312-50 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
13 comments · newest first
ME
Meaghan
12 months ago
Really? I’m surprised it’s not MS Blaster.
LE
Leatha
12 months ago
Nah, it's not MyDoom, that's a different issue.
WA
Wade
12 months ago
I thought it was SQL Slammer at first.
HY
Hyman
1 year ago
Totally agree, it's definitely WebDav!
WI
Wilford
1 year ago
This rule targets WebDav exploits.
JO
Jose
1 year ago
MyDoom seems like a possibility too, but I don't have a strong feeling about it. I wish I had reviewed more snort rules!
KE
Kenia
1 year ago
I practiced a similar question last week, and I think it was about MS Blaster. Could this rule apply to that?
DE
Delila
1 year ago
I remember something about SQL Slammer being a fast worm, but I can't recall if it matches this rule.
KA
Katie
1 year ago
I think this snort rule might relate to WebDav, but I'm not entirely sure. It feels familiar from our practice sessions.
GR
Graciela
1 year ago
Okay, I think I've got this. The manager wants to see the number of closed Cases in real time, so a Push Topic Event would be the way to go. That allows the dashboard to receive updates as soon as Cases are closed.
FR
Francesco
1 year ago
Hmm, this is a tricky one. I think the key is to avoid the blame game and really dig into the technical details to understand what went wrong. Gotta love those SRE practices!
LA
Latosha
1 year ago
I think the answer is B. Using an Open Application activity seems like the most straightforward way to start an app in Citrix.
SH
Shenika
1 year ago
Hmm, I'm a bit confused. The question mentions the organization tolerates 4% noncompliance, but the sample had 8 out of 90 desks with sensitive info. I'll need to do the math to see if that's within the tolerance.