Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Welcome to Pass4Success

- Free Preparation Discussions

Cisco 300-215 Exam - Topic 8 Question 53 Discussion

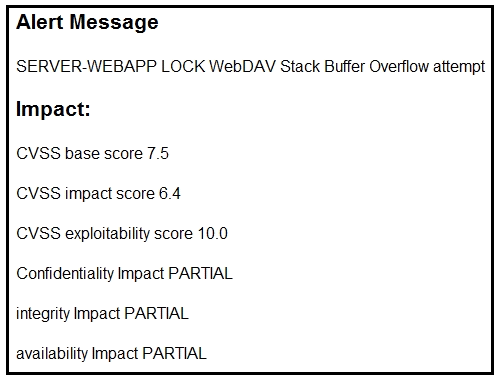
Refer to the exhibit.After a cyber attack, an engineer is analyzing an alert that was missed on the intrusion detection system. The attack exploited a vulnerability in a business critical, web-based application and violated its availability. Which two migration techniques should the engineer recommend? (Choose two.)
C) address space randomization and E) data execution prevention
A) encapsulation
B) NOP sled technique
D) heap-based security

Cisco 300-215 Exam - Topic 8 Question 53 Discussion

Actual exam question for Cisco's 300-215 exam
Question #: 53
Topic #: 8
[All 300-215 Questions]

Refer to the exhibit.

After a cyber attack, an engineer is analyzing an alert that was missed on the intrusion detection system. The attack exploited a vulnerability in a business critical, web-based application and violated its availability. Which two migration techniques should the engineer recommend? (Choose two.)

Show Suggested Answer Hide Answer
Suggested Answer: C, E

Contribute your Thoughts:

0/2000 characters
Delbert
10 months ago
Encapsulation could help, but not sure it's enough on its own.
upvoted 0 times
...
Merrilee
10 months ago
Surprised they didn't mention heap-based security!
upvoted 0 times
...
Oretha
10 months ago
NOP sled technique? Really? That seems outdated.
upvoted 0 times
...
Ashley
11 months ago
Totally agree, data execution prevention is also crucial.
upvoted 0 times
...
Hollis
11 months ago
I think address space randomization is a must!
upvoted 0 times
...
Avery
11 months ago
I'm a bit confused about heap-based security; I know it relates to memory management, but I can't recall its effectiveness in this context.
upvoted 0 times
...
Charisse
11 months ago
I practiced a question similar to this, and I feel like data execution prevention was mentioned as a key technique for securing applications.
upvoted 0 times
...
Sharika
11 months ago
I think address space randomization could be a good option since it makes it harder for attackers to predict where to find vulnerabilities.
upvoted 0 times
...
Carlota
11 months ago
I remember studying about encapsulation and how it can help protect application data, but I'm not sure if it's the best choice here.
upvoted 0 times
...
Amalia
11 months ago
I'm not too familiar with CRI-O, but since the question mentions it's related to OpenShift, I'll guess that option B is the correct answer.
upvoted 0 times
...
Simona
11 months ago
Okay, I've got this. The information protection solution is designed to safeguard sensitive data from unauthorized access. That means option D is the correct answer - it protects sensitive data from being exposed to unauthorized users.
upvoted 0 times
...
Hester
11 months ago
I'm a bit confused by this graph. I'm not sure how to interpret the "Within-Cluster Sum of Squares" metric and determine the optimal k value.
upvoted 0 times
...

Save Cancel