
 MENU

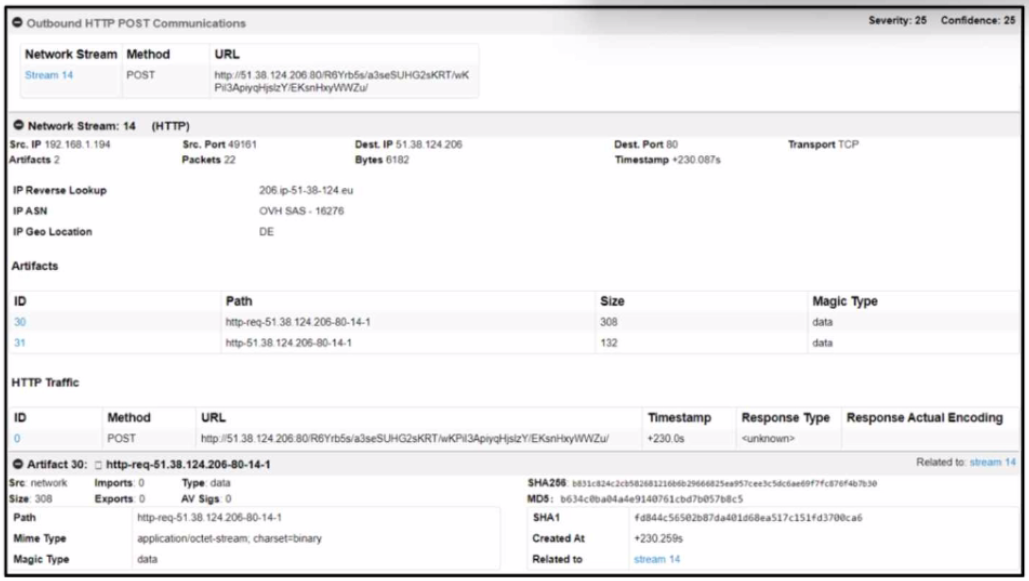
Refer to the exhibit.
Comprehensive and Detailed
From the exhibit, Cisco Secure Malware Analytics (formerly Threat Grid) has captured outbound HTTP POST communication to the IP address 51.38.124.206 on port 80. This destination is highlighted in the analysis under ''Outbound HTTP POST Communications,'' indicating exfiltration behavior or command-and-control (C2) signaling.
Key indicators:
The report shows that binary data was POSTed to this IP.
The source system generated 22 packets and sent 6,192 bytes.
The system has flagged the behavior with a severity of 25 and confidence of 25---suggesting that this is an IoC worth acting on.
Therefore, the artifacts suggest that the destination IP 51.38.124.206 is involved in malicious activity, and the correct answer is: