
 MENU

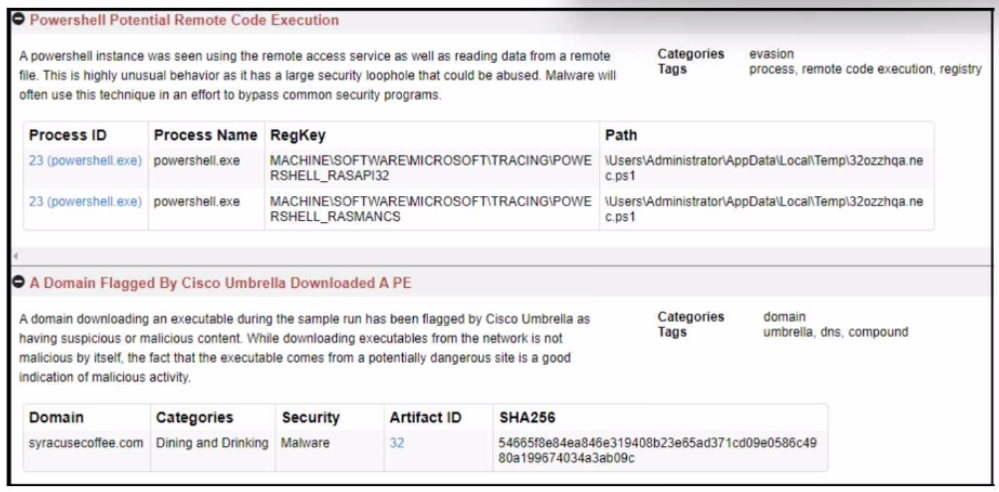
Refer to the exhibit.
Suggested Answer: A
Get Premium 300-215 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
The correct next step in analyzing the malicious nature of the email is to evaluate the artifacts in Cisco Secure Malware Analytics (formerly Threat Grid). This tool provides a comprehensive sandbox environment where behavioral indicators like file execution, registry access, and domain connections are logged and scored.
The exhibit shows:
Remote PowerShell execution
Executable download from a flagged domain
SHA256 hash linked to malware
All these artifacts, as labeled in the Secure Malware Analytics output, are key indicators of compromise, and analyzing them further can confirm whether the email was part of a malicious campaign.
Thus, the best action is: A . Evaluate the artifacts in Cisco Secure Malware Analytics.
27 comments · newest first
CA
Carolann
5 months ago
D is my choice. Activity paths help trace malware origins.
OD
Odette
6 months ago
C seems interesting. Registry activity can reveal hidden issues.
KA
Kate
6 months ago
I prefer B. File activity shows real-time threats.
RE
Renay
6 months ago
I think option A is the best. Malware insights are crucial.
JA
Jacklyn
6 months ago
Wait, are we really using Cisco for this? Didn't expect that!
MY
Myra
6 months ago
D) Seems a bit complex, not sure it's necessary.
OL
Oliva
6 months ago
C) is crucial for understanding registry changes!
ST
Stephania
7 months ago
I think B) is more relevant for file activity insights.
EL
Elliott
7 months ago
A) looks like a solid choice for malware analysis.
BO
Bong
7 months ago
Haha, I bet the exam writers had a field day coming up with these options. Time to put on my thinking cap!
BL
Blossom
7 months ago
D) Analyze the activity paths in Cisco Secure Malware Analytics. This is the way to go, folks. It's the only option that aligns with the information presented.
GA
Garry
7 months ago
B) Evaluate the file activity in Cisco Umbrella. I'm not feeling confident about this one. The image looks more focused on Cisco Secure Malware Analytics.
LE
Leanora
8 months ago
C) Analyze the registry activity section in Cisco Umbrella. Hmm, I'm not convinced this is the right answer. The image doesn't seem to focus on Cisco Umbrella.
MA
Mable
8 months ago
A) Evaluate the artifacts in Cisco Secure Malware Analytics. Seems like a reasonable choice, but I'm not sure it's the best option.
RE
Reuben
8 months ago
D) Analyze the activity paths in Cisco Secure Malware Analytics. This is the correct answer based on the image.
AL
Alline
8 months ago
I definitely remember discussing activity paths in Cisco Secure Malware Analytics, but I need to double-check how to interpret those paths effectively.
MA
Margarita
9 months ago
I feel a bit uncertain about the registry activity section in Cisco Umbrella; I hope I can remember the steps to analyze it properly.
DA
Daniela
9 months ago
I think analyzing file activity in Cisco Umbrella was covered in a similar practice question, but I can't recall the key metrics we should look for.
HE
Helaine
9 months ago
I remember we practiced evaluating artifacts in Cisco Secure Malware Analytics, but I'm not sure what specific details to focus on.
LU
Luz
9 months ago
Hmm, I'm not sure I fully understand what they're asking for in the registry activity section. I'll need to review my notes on Umbrella to make sure I'm interpreting that correctly. But I think I can handle the rest of the question.
LO
Louann
9 months ago
I feel pretty confident about this one. I've worked with Cisco Secure Malware Analytics and Umbrella before, so I think I can tackle all the different parts of the question. I'll just need to make sure I'm addressing each part thoroughly.
EL
Elmira
10 months ago
Okay, I've got a plan. I'll start by analyzing the activity paths in Cisco Secure Malware Analytics, since that seems like the core of the question. Then I'll move on to evaluating the other sections to get a full picture.
BE
Bernardine
10 months ago
I'm a bit confused by the different sections here. Should I be focusing on the file activity in Umbrella or the registry activity? I'll need to read through the question carefully to make sure I understand what they're asking.
MO
Mohammad
10 months ago
Hmm, this looks like a tricky one. I think I'll start by evaluating the artifacts in Cisco Secure Malware Analytics, since that seems like the most straightforward part.
AL
Alesia
3 months ago
True, but I feel like file activity in Umbrella is crucial too.
LO
Louvenia
4 months ago
But what about analyzing activity paths? That could reveal more insights.
TH
Thora
4 months ago
I agree, evaluating artifacts sounds solid.