
Free Preparation Discussions
 MENU

Cisco 200-901 Exam - Topic 1 Question 117 Discussion
Topic #: 1
Refer to the exhibit.
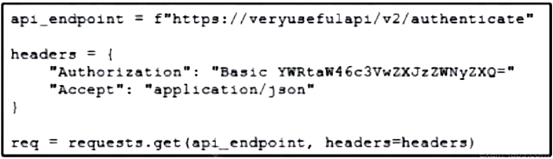
A developer is part of a team that is working on an open-source project in which source code is hosted in a public GitHub repository. While the application was built, security concerns were addressed by encrypting the credentials on the server. After a few months, the developer realized that a hacker managed to gain access to the account. The exhibit contains part of the source code for the login process. Why was the attacker able to access the developer's account?
The exhibit shows that the credentials are base64 encoded and included in the source code. Base64 encoding is not a secure method of protecting credentials as it can be easily decoded. Therefore, an attacker who gains access to the source code can decode the credentials and gain unauthorized access to the account. Proper security practices should involve storing credentials securely, such as using environment variables or secure vaults, and not hardcoding them in the source code.
OWASP - Storing Passwords Securely
Cisco DevNet Associate Certification Guide
Keneth
2 days agoJohnetta
7 days agoCoral
12 days agoDeangelo
17 days agoDean
23 days agoMisty
28 days agoLavonne
1 month agoElroy
1 month agoSol
1 month agoKallie
2 months agoShawnta
2 months ago