Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Free Preparation Discussions
 MENU

CIPS L5M3 Exam - Topic 1 Question 5 Discussion
Actual exam question for
CIPS's
L5M3 exam
Question #: 5
Topic #: 1
[All L5M3 Questions]
Topic #: 1
Which of the following will you put into box 1?
Suggested Answer:
B
The correct answers are as follows:
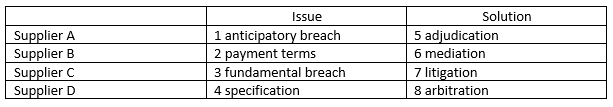
This is arbitration as it involves a panel.
Miles
10 months agoLinette
10 months agoLaquita
10 months agoBulah
11 months agoKris
11 months agoMonroe
11 months agoAdolph
11 months agoMarla
11 months agoCarin
11 months agoAshton
11 months agoGary
11 months agoTalia
11 months agoJolanda
1 year agoTabetha
1 year agoGracia
1 year agoRaina
1 year agoRonny
1 year agoCarlee
1 year agoAshanti
1 year agoRia
1 year agoCassie
1 year agoYuriko
1 year agoCasey
1 year agoLavonna
1 year agoOra
1 year agoLashawn
1 year agoEvangelina
1 year agoDeandrea
1 year agoKattie
1 year agoDorathy
1 year agoTalia
1 year agoZena
1 year agoEdda
1 year agoNichelle
1 year agoDiane
1 year agoCathern
1 year agoDenny
1 year agoHubert
1 year ago