
 MENU

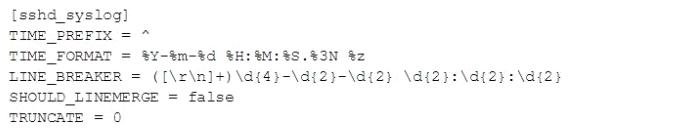
In this source definition the MAX_TIMESTAMP_LOOKHEAD is missing. Which value would fit best?
Event example:
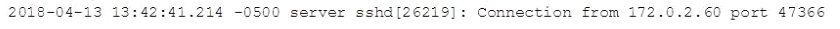
Suggested Answer: D
Get Premium SPLK-1003 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
12 comments · newest first
AN
An
11 months ago
MAX_TIMESTAMP_LOOKAHEAD usually ranges from 5 to 20.
HO
Honey
11 months ago
Wait, is 30 even realistic?
SA
Salley
12 months ago
C seems way too high, right?
JO
Jordan
12 months ago
Definitely agree with B!
TW
Twanna
12 months ago
I think B (10) is a safe bet.
CH
Chi
1 year ago
I feel like 10 could be a good fit, but I also remember something about needing to consider the event frequency.
TU
Tuyet
1 year ago
I’m a bit confused about the values. Is 30 too high? I feel like I need to double-check the documentation.
CA
Catarina
1 year ago
I think I practiced a question similar to this, and I chose 20 because it seemed like a safe upper limit.
AL
Alex
1 year ago
I remember reading that MAX_TIMESTAMP_LOOKAHEAD usually defaults to 10, but I'm not entirely sure if that's the best choice here.
CH
Chery
1 year ago
Okay, let me think this through step-by-step. I need to determine the best way to model the many-to-many relationship.
VE
Verda
1 year ago
I remember discussing subnet configurations; maybe changing the system IPs is key here? But I'm not completely sure.
ME
Mel
1 year ago
I'm a bit confused by the wording of the question. Does "Multiple choices" mean I can select more than one answer?