
Free Preparation Discussions
 MENU

Splunk SPLK-1003 Exam Questions
- Topic 1: Splunk Admin Basics: This section evaluates the foundational knowledge required of a Splunk Administrator, focusing on identifying core components such as indexers, search heads, and forwarders within a Splunk deployment.
- Topic 2: License Management: Designed for Splunk Administrators, this domain addresses types of Splunk licenses, how to manage them effectively, and the implications of license violations on operational continuity.
- Topic 3: Splunk Configuration Files: This part assesses a Splunk Administrator’s ability to navigate the configuration file directory, understand precedence and layering, and use diagnostic tools like btool to verify configuration settings.
- Topic 4: Splunk Indexes: Relevant to Splunk Administrators, this section covers the structure and types of index buckets, data retention policies, integrity checks, and the role of the fishbucket in tracking file inputs.
- Topic 5: Splunk User Management: Aimed at Splunk Administrators, this area focuses on user account creation, role-based access controls, and custom role development to maintain a secure and organised user environment.
- Topic 6: Splunk Authentication Management: This domain is intended for Security Operations Engineers and involves integrating LDAP directories, implementing multi-factor authentication, and exploring other authentication mechanisms within Splunk.
- Topic 7: Getting Data In: This domain addresses the responsibilities of Splunk Administrators in configuring data inputs, differentiating forwarder types, and using the command-line interface for setting up Universal Forwarders.
- Topic 8: Distributed Search: Security Operations Engineers are assessed on their understanding of distributed search architecture, including search head and peer roles, and how to configure and manage search groups.
- Topic 9: Getting Data In – Staging: This section is relevant to Splunk Administrators and focuses on the three stages of data indexing—input, parsing, and indexing—and outlines data ingestion options and configurations.
- Topic 10: Configuring Forwarders: Splunk Administrators are assessed on the deployment and configuration of forwarders, along with recognition of additional forwarder functionalities essential for scalable data ingestion.
- Topic 11: Forwarder Management: This section, intended for Splunk Administrators, tests the candidate's understanding of deployment servers, forwarder apps, client group management, and monitoring forwarder activities across distributed environments.
- Topic 12: Monitor Inputs: Targeted at Splunk Administrators, this domain involves creating and customising monitor inputs for files and directories, including the deployment of remote monitors.
- Topic 13: Network and Scripted Inputs: Security Operations Engineers are assessed on setting up and customising TCP and UDP network inputs, as well as implementing basic scripted inputs for dynamic data ingestion.
- Topic 14: Agentless Inputs: Designed for Security Operations Engineers, this section covers creating agentless inputs using WMI and HTTP Event Collector (HEC), particularly for integrating data from Windows and RESTful sources.
- Topic 15: Fine Tuning Inputs: Splunk Administrators are evaluated on their ability to customise input processing, including sourcetype identification, character encoding, and other configurations for accurate data onboarding.
- Topic 16: Parsing Phase and Data: Security Operations Engineers are tested on their understanding of event parsing, timestamp recognition, and the use of data preview tools to verify data correctness prior to indexing.
- Topic 17: Manipulating Raw Data: Aimed at Splunk Administrators, this section covers using configuration files to mask, re-route, or suppress data at index time using props.conf, transforms.conf, and SEDCMD.
Free Splunk SPLK-1003 Exam Actual Questions
Note: Premium Questions for SPLK-1003 were last updated On Oct. 28, 2026 (see below)
Which Splunk forwarder type allows parsing of data before forwarding to an indexer?
The universal forwarder has which capabilities when sending data? (select all that apply)
A user is assigned two roles with the following search filters. What is the user's applied search filter?
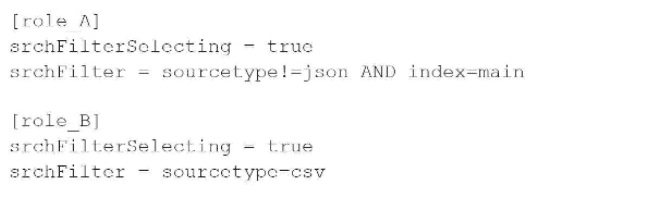
When a user is assignedmultiple rolesin Splunk and each has a defined srchFilter, Splunk combines these filters using alogical ANDoperation. This ensures that the user can only search within the intersection of constraints imposed by each role.
From Splunk Docs:
'If a user has multiple roles assigned and multiple roles specify srchFilter, Splunk softwareANDs the filters together.'
--- Source: Splunk Documentation -- authorize.conf
Let's break it down:
role_A specifies: sourcetype!=json AND index=main
role_B specifies: sourcetype=csv
To evaluate the effective search filter for the user, Splunk willANDthe two conditions:
(sourcetype=csv) AND (sourcetype!=json AND index=main)
This means the user's search is limited to events where:
sourcetype=csv (from role_B)
sourcetype!=json AND index=main (from role_A)
Combining them together logically:
srchFilter = ((sourcetype=csv) AND (sourcetype!=json AND index=main))
This is exactly what is shown inOption A.
authorize.conf - Splunk Admin Manual
Which valid bucket types are searchable? (select all that apply)
Hot/warm/cold/thawed bucket types are searchable. Frozen isn't searchable because its either deleted at that state or archived.
What configuration file are remote Windows Management Instrumentation inputs defined in?
In Splunk Enterprise, when collecting data from remote Windows machines using Windows Management Instrumentation (WMI), the configurations are defined in the wmi.conf file. This file specifies the parameters for connecting to WMI providers and defines the data inputs.
The wmi.conf file is located in the $SPLUNK_HOME\etc\system\local\ directory. It contains stanzas that define global settings and input-specific configurations for WMI data collection. This setup allows Splunk to collect various types of data from remote Windows systems, such as event logs and performance metrics, without requiring a forwarder on the remote machine.
Monitor data through Windows Management Instrumentation (WMI) - Splunk Documentation
wmi.conf - Splunk Documentation
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
William Mitchell
1 month agoKaren Phillips
2 months agoKenneth Carter
2 months agoCharles Phillips
3 months agoDorothy Flores
3 months agoJason Howard
4 months agoJason King
4 months agoNancy Rodriguez
5 months agoJames Nelson
5 months agoDorothy Nguyen
6 months agoChristopher Sanchez
6 months agoSarah Jones
6 months agoMargaret Miller
6 months agoAnthony Parker
6 months agoHeather Torres
6 months agoSusan Edwards
6 months agoKayleigh
7 months agoCarrol
7 months agoLilli
7 months agoLeota
8 months agoRashida
8 months agoTess
8 months agoAlex
8 months agoTalia
9 months agoJackie
9 months agoEleonora
9 months agoNickolas
9 months agoErick
10 months agoTyisha
10 months agoDorothy
10 months agoKrystal
10 months agoErin
11 months agoPamella
11 months agoDorothy
11 months agoThea
11 months agoHoney
12 months agoBilly
12 months agoThurman
1 year agoFanny
1 year agoLezlie
1 year agoCorrinne
1 year agoMargarita
1 year agoEveline
1 year agoReita
1 year agoNieves
1 year agoDaron
1 year agoMarcelle
1 year agoCiara
1 year agoLavonna
2 years agoMarylin
2 years agoVivan
2 years agoAleta
2 years agoRefugia
2 years agoMaurine
2 years agoKasandra
2 years agoCharlesetta
2 years agoClorinda
2 years agoViola
2 years agoRueben
2 years agoFiliberto
2 years agoVince
2 years agoJose
2 years agoVirgie
2 years agoFreida
2 years agoBarney
2 years agoMindy
2 years agoIsadora
2 years agoCordelia
2 years agoRosendo
2 years agoJamal
2 years agoDonette
2 years agoLaurel
2 years agoWillodean
2 years agoIsadora
2 years agoLyndia
2 years agoQuentin
2 years agoAngella
2 years agoTroy
2 years agoFairy
2 years agoMozell
2 years agoCarry
2 years agoKandis
2 years agoHalina
2 years agoMeghann
2 years agoWei
2 years agoOliva
2 years agoEmilio
2 years ago