
 MENU

After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an app named App1 that is installed on two Azure virtual machines named VM1 and VM2. Connections to Appl are managed by using an Azure Load Balancer.
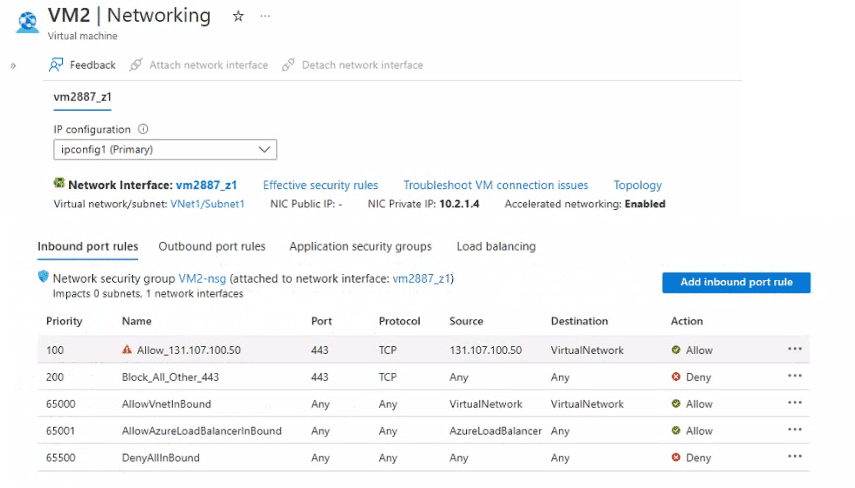
The effective network security configurations for VM2 are shown in the following exhibit.
You discover that connections 10 App1 from 131.107.100.50 over TCP port 443 fail.
You verity that the Load Balancer rules are configured correctly.
You need to ensure that connections to App1 can be established successfully from 131.107.100.50 over TCP port 443.
Solution: You create an inbound security rule that allows any traffic from the Azureload Balancer source and has a priority of 150.
Does this meet the goal?
Exhibit
Traffic from the load balancer's health-probe/data path is already permitted by the default AllowAzureLoadBalancerInBound rule at priority 65001, so adding another AzureLoadBalancer-source allow rule at priority 150 does nothing new. The exhibit shows Allow_131.107.100.50 (priority 100, allow, destination VirtualNetwork) sitting ahead of Block_All_Other_443 (priority 200, deny) --- NSG rules are evaluated in ascending priority order and processing stops at the first match, so rule 100 should already permit this specific source on port 443. The real defect here is that Block_All_Other_443 (200) still exists and is evaluated for any request that doesn't cleanly match rule 100 (for example if the destination scope of rule 100 doesn't line up with the actual traffic pattern); adding an unrelated AzureLoadBalancer rule at 150 does not touch this conflict and therefore does not fix client connectivity. The effective fix is to adjust the priority/scope of the existing Allow_131.107.100.50 rule, not to add a Load Balancer-source rule.
Official Reference
Network security group rule processing and default rules --- https://learn.microsoft.com/en-us/azure/virtual-network/network-security-groups-overview
Currently there are no comments in this discussion, be the first to comment!