
 MENU

NO: 99
A BIND server should be upgraded to use TSIG. Which configuration parameters should be added if the server should use the algorithm hmac-md5 and the key skrKc4DoTzi/takIlPi7JZA==?
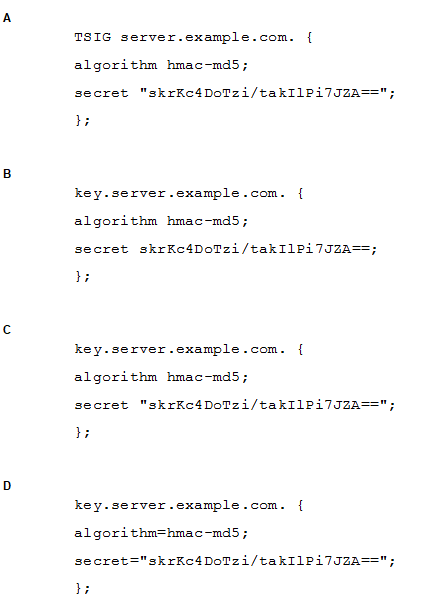
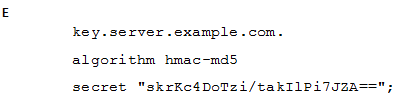
Suggested Answer: C
Get Premium 202-450 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
11 comments · newest first
VA
Vanda
11 months ago
Just make sure the key is base64 encoded!
JE
Jerry
12 months ago
I think Option C is the right one for this.
SI
Simona
12 months ago
Wait, is hmac-md5 still considered secure?
OM
Omer
12 months ago
Totally agree, hmac-md5 is a solid choice!
GL
Glory
1 year ago
You need to add the key and algorithm in the config.
CH
Cheryl
1 year ago
I believe the hmac-md5 algorithm is pretty standard for TSIG, but I’m confused about how to format the key in the config file.
CU
Curt
1 year ago
I remember practicing a similar question where we had to set up TSIG keys, but I can't recall if the key needs to be base64 encoded or not.
LU
Luke
1 year ago
I think we need to specify the algorithm and the key in the configuration file, but I'm not entirely sure about the exact syntax.
SL
Slyvia
1 year ago
I think we might need to include a line for the key and another for the algorithm, but I’m not confident if there are any additional parameters required.
LE
Leandro
1 year ago
This seems like a straightforward question. I think the check sheet would be the best tool to collect this data, since it allows you to tally the number of times certain events occur.
TR
Trina
1 year ago
Okay, let me think this through step-by-step. The question is asking about the correct placement of the 'as-override' command to prevent BGP loops. I'll need to carefully analyze the options.