Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Free Preparation Discussions
 MENU

Linux Foundation CKS Exam - Topic 1 Question 31 Discussion
Actual exam question for
Linux Foundation's
CKS exam
Question #: 31
Topic #: 1
[All CKS Questions]
Topic #: 1
Context
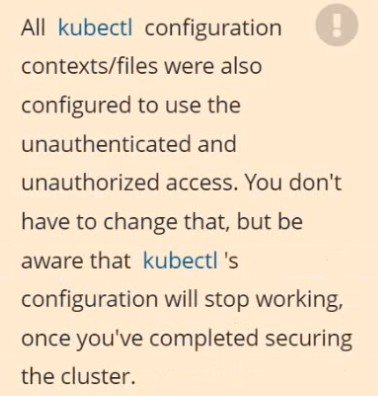
The kubeadm-created cluster's Kubernetes API server was, for testing purposes, temporarily configured to allow unauthenticated and unauthorized access granting the anonymous user duster-admin access.
Task
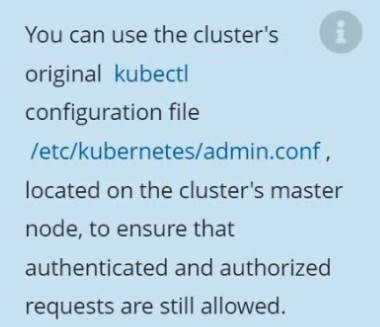
Reconfigure the cluster's Kubernetes API server to ensure that only authenticated and authorized REST requests are allowed.
Use authorization mode Node,RBAC and admission controller NodeRestriction.
Cleaning up, remove the ClusterRoleBinding for user system:anonymous.
Suggested Answer:
A
Daryl
10 months agoLaurel
11 months agoEffie
11 months agoYuette
11 months agoMariann
11 months agoKaron
11 months agoAbraham
11 months agoRoyce
11 months agoDerick
12 months agoHerminia
12 months agoChau
12 months ago