
Free Preparation Discussions
 MENU

Juniper JN0-683 Exam Questions
- Topic 1: Data Center Deployment and Management: This section assesses the expertise of data center networking professionals like architects and engineers, focusing on key deployment concepts. Topics include Zero-touch provisioning (ZTP), which automates device setup in data centers without manual input.
- Topic 2: Layer 3 Fabrics: This section measures the knowledge of professionals managing IP-based networks in data centers. It covers IP fabric architecture and routing, ensuring candidates understand how the network is structured for scalability and how traffic is routed efficiently.
- Topic 3: VXLAN: This part requires knowledge of VXLAN, particularly how the control plane manages communication between devices, while the data plane handles traffic flow. Demonstrate knowledge of how to configure, Monitor, or Troubleshoot VXLAN.
- Topic 4: EVPN-VXLAN Signaling: This section assesses an understanding of Ethernet VPN (EVPN) concepts, including route types, multicast handling, and Multiprotocol BGP (MBGP). It also covers EVPN architectures like CRB and ERB, MAC learning, and symmetric routing.
- Topic 5: Data Center Interconnect: For Data Center Engineers, this part focuses on interconnecting data centers, covering Layer 2 and Layer 3 stretching, stitching fabrics together, and using EVPN-signaled VXLAN for seamless communication between data centers.
- Topic 6: Data Center Multitenancy and Security: This section tests knowledge of single-tenant and multitenant data center setups. Candidates such as Data Center Professionals are evaluated on ensuring tenant traffic isolation at both Layer 2 and Layer 3 levels in shared infrastructure environments.
Free Juniper JN0-683 Exam Actual Questions
Note: Premium Questions for JN0-683 were last updated On Oct. 16, 2026 (see below)
You want to convert an MX Series router from a VXLAN Layer 2 gateway to a VXLAN Layer 3 gateway for VNI 100. You have already configured an IRB interface. In this scenario, which command would you use to accomplish this task?
Scenario Overview:
Converting an MX Series router from a VXLAN Layer 2 gateway to a VXLAN Layer 3 gateway involves transitioning the router's functionality from simply bridging traffic within a VXLAN segment to routing traffic between different segments.
Key Configuration Requirement:
IRB (Integrated Routing and Bridging) Interface: An IRB interface allows for both Layer 2 switching and Layer 3 routing. To enable routing for a specific VNI (VXLAN Network Identifier), the IRB interface must be associated with the routing function in the corresponding bridge domain.
Correct Command:
C . set bridge-domains VLAN-100 routing-interface irb.100: This command correctly binds the IRB interface to the bridge domain, enabling Layer 3 routing functionality within the VXLAN for VNI 100. This effectively transitions the device from operating solely as a Layer 2 gateway to a Layer 3 gateway.
Data Center Reference:
This configuration step is essential when converting a Layer 2 VXLAN gateway to a Layer 3 gateway, enabling the MX Series router to route between VXLAN segments.
Which statement is correct about a collapsed fabric EVPN-VXLAN architecture?
Collapsed Fabric Architecture:
A collapsed fabric refers to a simplified architecture where the spine and leaf roles are combined, often reducing the number of devices and links required.
In this architecture, the spine typically handles core switching, while leaf switches handle both access and distribution roles.
Understanding Border Gateway Functionality:
Border gateway functions include connecting the data center to external networks or other data centers.
In a collapsed fabric, these functions are usually handled at the leaf level, particularly on border leaf devices that manage the ingress and egress of traffic to and from the data center fabric.
Correct Statement:
D . Border gateway functions occur on border leaf devices: This is accurate in collapsed fabric architectures, where the border leaf devices take on the role of managing external connections and handling routes to other data centers or the internet.
Data Center Reference:
The collapsed fabric model is advantageous in smaller deployments or scenarios where simplicity and cost-effectiveness are prioritized. It reduces complexity by consolidating functions into fewer devices, and the border leaf handles the critical task of interfacing with external networks.
In conclusion, border gateway functions are effectively managed at the leaf layer in collapsed fabric architectures, ensuring that the data center can communicate with external networks seamlessly.
Exhibit.
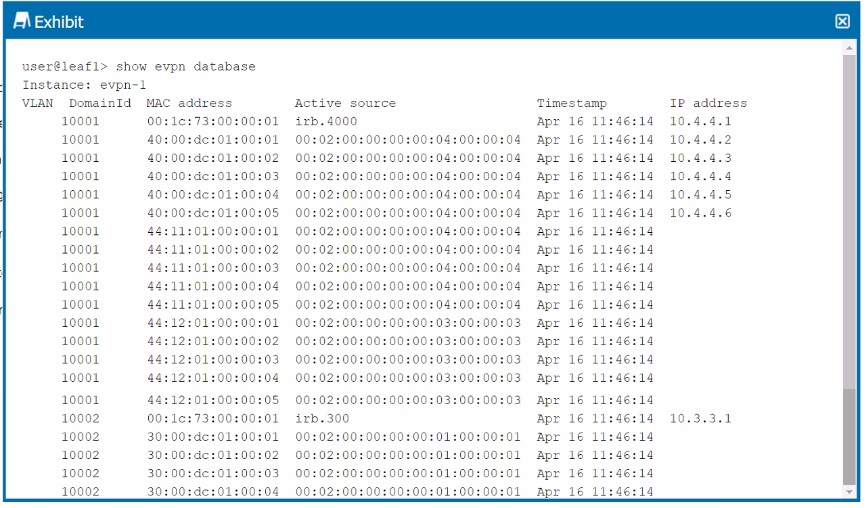
The exhibit shows the truncated output of the show evpn database command.
Given this output, which two statements are correct about the host with MAC address 40:00:dc:01:00:04? (Choose two.)
Understanding the Output:
The show evpn database command output shows the MAC address, VLAN, active source, timestamp, and IP address associated with various hosts in the EVPN instance.
Analysis of the MAC Address:
Option A: The MAC address 40:00:dc:01:00:04 is associated with the IP address 10.4.4.5, as indicated by the output in the IP address column. This confirms that this host has been assigned the IP 10.4.4.5.
Option D: The active source for the MAC address 40:00:dc:01:00:04 is listed as 00:02:00:00:00:04:00:04:00:00:04:00:04, which indicates that the host is connected via an ESI (Ethernet Segment Identifier) LAG (Link Aggregation Group). This setup is typically used in multi-homing scenarios to provide redundancy and load balancing across multiple physical links.
Conclusion:
Option A: Correct---The host with MAC 40:00:dc:01:00:04 is assigned IP 10.4.4.5.
Option D: Correct---The host is originating from an ESI LAG, as indicated by the active source value.
You want to provide a OCI that keeps each data center routing domain isolated, while also supporting translation of VNIs. Which DCI scheme allows these features?
Understanding DCI (Data Center Interconnect) Schemes:
DCI schemes are used to connect multiple data centers, enabling seamless communication and resource sharing between them. The choice of DCI depends on the specific requirements, such as isolation, VNI translation, or routing domain separation.
VXLAN Stitching:
VXLAN stitching involves connecting multiple VXLAN segments, allowing VNIs (VXLAN Network Identifiers) from different segments to communicate with each other while maintaining separate routing domains.
This approach is particularly effective for keeping routing domains isolated while supporting VNI translation, making it ideal for scenarios where you need to connect different data centers or networks without merging their control planes.
Other Options:
A . MPLS DCI label exchange: This option typically focuses on MPLS-based interconnections and does not inherently support VNI translation or isolation in the context of VXLAN.
B . Over the top (OTT) with VNI translation enabled: This could support VNI translation but does not inherently ensure routing domain isolation.
D . Over the top (OTT) with proxy gateways: This typically involves using external gateways for traffic routing and may not directly support VNI translation or isolation in the same way as VXLAN stitching.
Data Center Reference:
VXLAN stitching is a powerful method in multi-data center environments, allowing for flexibility in connecting various VXLAN segments while preserving network isolation and supporting complex interconnect requirements.
Which parameter is used to associate a received route with a local VPN route table?
Understanding VPN Route Table Association:
In MPLS/VPN and EVPN networks, the route-target community is a BGP extended community attribute used to control the import and export of VPN routes. It associates received routes with the appropriate VPN route tables on the PE (Provider Edge) routers.
Function of Route-Target Community:
The route-target community tag ensures that routes are imported into the correct VRF (Virtual Routing and Forwarding) instance, allowing them to be correctly routed within the VPN.
Conclusion:
Option A: Correct---The route-target community is used to associate received routes with a local VPN route table.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Christopher Torres
27 days agoDavid Taylor
2 months agoHyun Wu
19 days agoMichael Scott
2 months agoAnthony Baker
3 months agoFrank Mitchell
3 months agoAmanda Moore
4 months agoJason Mitchell
4 months agoJohn Nguyen
5 months agoMelissa Nelson
5 months agoStephen Scott
6 months agoAdam Nguyen
6 months agoPablo Greco
13 days agoCarol Gonzalez
6 months agoDorothy Nguyen
6 months agoStephanie Cook
5 months agoMichael Anderson
5 months agoAlana
7 months agoThaddeus
7 months agoJoni
7 months agoGlendora
7 months agoLouis
8 months agoJeanice
8 months agoJeannetta
8 months agoRolande
9 months agoTamesha
9 months agoLouisa
9 months agoLeonor
9 months agoSabina
10 months agoKiley
10 months agoGussie
10 months agoKaran
10 months agoTonette
11 months agoAllene
11 months agoSherita
11 months agoLezlie
11 months agoTegan
12 months agoCarylon
12 months agoEllsworth
1 year agoEdgar
1 year agoTracey
1 year agoCharlette
1 year agoGianna
1 year agoKati
1 year agoTonette
1 year agoMillie
1 year agoDong
1 year agoBillye
1 year agoPamella
1 year agoElza
1 year agoJess
1 year agoCecilia
1 year agoAaron
1 year agoMarylin
2 years agoMarva
2 years agoSueann
2 years agoMirta
2 years agoTricia
2 years agoMonte
2 years agoOretha
2 years agoRegenia
2 years agoCassie
2 years agoEdwin
2 years agoStevie
2 years agoJean
2 years agoGerri
2 years agoBrynn
2 years agoAmos
2 years agoJohnson
2 years agoEvan
2 years agoHerminia
2 years agoRessie
2 years agoDella
2 years agoMerlyn
2 years agoFrederica
2 years agoQueenie
2 years agoKeshia
2 years agoViki
2 years agoChu
2 years agoRyan
2 years agoJade
2 years agoDalene
2 years agoWilford
2 years agoPa
2 years agoKimbery
2 years agoAnnabelle
2 years ago