
 MENU

Refer to the exhibit.
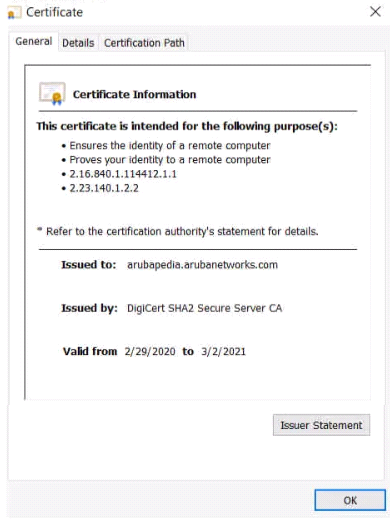
Device A is establishing an HTTPS session with the Arubapedia web sue using Chrome. The Arubapedia web server sends the certificate shown in the exhibit
What does the browser do as part of vacating the web server certificate?
Suggested Answer: C
Get Premium HPE6-A78 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
37 comments · newest first
KE
Keneth
12 months ago
I thought it was the private key for some reason, but now I'm confused.
VI
Vicente
12 months ago
100% agree with Corrina, that's how it works!
AL
Alaine
1 year ago
Wait, are we sure it's not the private key? That seems odd.
LO
Lovetta
1 year ago
I think it's the public key from the DigCert SHA2 CA, right?
CO
Corrina
1 year ago
It's definitely using the public key from the root CA!
MA
Maira
1 year ago
I feel like option A makes sense since it mentions the DigCert SHA2 Secure Server CA, but I’m not confident if that’s the right one to use for checking the signature.
TO
Tonette
1 year ago
I’m a bit confused about the roles of the public and private keys here. I thought the browser always uses the public key to verify signatures, but I can't recall the specifics.
MA
Margarett
1 year ago
I remember practicing a question similar to this, and I believe it was about using the public key for verification. So, I might lean towards option B.
JO
Joni
1 year ago
I think the browser checks the certificate's signature using the public key from the root CA, but I'm not entirely sure if it's the DigCert root or the SHA2 Secure Server CA.
LA
Laila
1 year ago
Okay, I've got a strategy - I'll first consider the definitions of each option, then eliminate the ones that don't match the question.
ME
Melissa
1 year ago
This is a tricky one. The question is really testing our ability to draw the right analogy from the airplane cockpit example. I'll need to make sure I fully understand how the different instruments and indicators in the cockpit relate to the overall performance and success of the flight.
AN
Andra
1 year ago
I feel pretty confident about this one. The Citrix Configuration Service is the key service that Citrix Studio relies on, so a failure there would definitely cause issues when trying to access Citrix Studio.
GL
Glenna
1 year ago
This question is making my head spin. Can we just ask the Arubapedia web server to verify their own certificate for us? That seems like the easiest solution.
QU
Queenie
1 year ago
User1: Ah, I see. It's all about verifying the certificate chain correctly.
BE
Bernadine
1 year ago
User3: No, it actually uses the public key in the DigCert root CA certificate to verify the certificate signature.
LE
Lettie
1 year ago
User2: So, the browser uses the public key in the DigCen SHA2 Secure Server CA certificate to check the certificate's signature, right?
DA
Daniel
1 year ago
User1: I wish it was that easy, but the browser has to verify the certificate using the public key in a specific certificate.
WI
William
1 year ago
Ah, I see what's happening here. The browser checks the signature using the public key in the DigiCert SHA2 Secure Server CA certificate. Easy peasy!
CA
Carol
1 year ago
User 3: Easy peasy, lemon squeezy!
JA
Jacqueline
1 year ago
User 2: That's correct! It's part of validating the web server certificate.
AL
Alva
1 year ago
User 1: The browser uses the public key in the DigCen SHA2 Secure Server CA certificate to check the certificate's signature.
AL
Aleta
1 year ago
Hmm, I think the public key in the DigiCert root CA certificate is the way to go. That's the trusted root, right?
SH
Sharee
1 year ago
Owen: That makes sense, it's all about verifying the authenticity of the certificate.
OW
Owen
1 year ago
User 2: The browser uses the public key in the DigiCert root CA certificate to check the certificate signature.
WI
Willard
1 year ago
User 1: I agree, the DigiCert root CA certificate is the trusted root.
LO
Lorrie
2 years ago
Wait, are we supposed to use the public key or the private key to verify the certificate? I'm so confused!
VI
Vincent
1 year ago
User1: Oh, I see. Thanks for clarifying!
CA
Candida
1 year ago
User3: Because the private key is used by the web server to sign the certificate, while the public key is used by the browser to verify the signature.
CR
Cruz
1 year ago
User2: But why not the private key?
GR
Gracia
1 year ago
User1: It uses the public key in the DigCen SHA2 Secure Server CA certificate to check the certificate's signature.
BR
Brinda
1 year ago
It's okay, I think we use the public key in the certificate to verify it.
JO
Joaquin
1 year ago
C) It uses the private key in the DigiCert SHA2 Secure Server CA to check the certificate's signature.
NO
Nobuko
1 year ago
B) It uses the public key in the DigCert root CA certificate to check the certificate signature
FR
Fredric
1 year ago
A) It uses the public key in the DigCen SHA2 Secure Server CA certificate to check the certificate's signature.
KA
Karan
2 years ago
I'm not sure about that. I think it uses the private key in the Arubapedia web site's certificate to check the signature.
MA
Maurine
2 years ago
I agree with Erasmo. That's how the browser validates the certificate.
ER
Erasmo
2 years ago
I think the browser uses the public key in the DigCen SHA2 Secure Server CA certificate to check the certificate's signature.