
 MENU

Analyze the screenshot below. Which of the following attacks can be mitigated by these configuration settings?
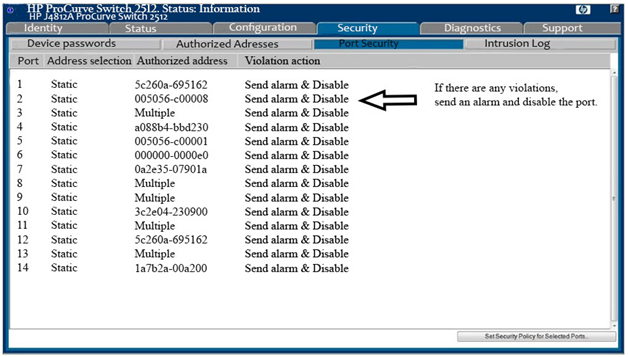
Suggested Answer: D
Get Premium GCED Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
Both BPDU Guard and Root Guard are used to prevent a new switch from becoming the Root Bridge. They are very similar but use different mechanisms.
Rootguard allows devices to use STP, but if they send superior BDPUs (i.e. they attempt to become the Root Bridge), Root Guard disables the port until the offending BPDUs cease. Recovery is automatic.
If Portfast is enabled on a port, BPDU Guard will disable the port if a BPDU is received. The port stays disabled until it is manually re-enabled. Devices behind such ports cannot use STP, as the port would be disabled as soon as they send BPDUs (which is the default behavior of switches).
13 comments · newest first
LE
Leonora
11 months ago
Wait, I didn't know these settings could do that!
EM
Emerson
11 months ago
Agreed, but can it really stop IP masquerading?
KA
Karol
12 months ago
Not so sure about that, what about Replay attacks?
LI
Lilli
12 months ago
I think it also helps with MAC Flood attacks.
MA
Margurite
12 months ago
Definitely mitigates Denial-of-Service attacks.
NO
Novella
1 year ago
I believe the configuration could prevent an IP masquerading attack, but I need to double-check my notes on that one.
MA
Marlon
1 year ago
I'm a bit confused about the Replay attack. I thought those settings were more about network traffic than replay issues.
SH
Sheron
1 year ago
I remember practicing a similar question about MAC Flood attacks, and I feel like those settings could definitely mitigate that type of attack.
JU
Juliana
1 year ago
I think the settings might help with the Denial-of-Service attack, but I'm not entirely sure how they relate to network broadcasts specifically.
GE
German
1 year ago
The catalog is the clear winner here. That's where the administrator will find the most comprehensive and up-to-date information on the cloud provider's service offerings.
TH
Thaddeus
1 year ago
I'm pretty confident that Option B is the correct answer here. Changing the management port on the FMC and pushing that change to the FTD devices is the way to ensure they can all communicate.
GE
Gertude
1 year ago
Okay, I think I've got this. The key is to consider the different ways incidents can be created - either programmatically through the API or manually through the UI. The other options don't seem directly related to the incident configuration process.
AU
Audria
1 year ago
I think Cisco Expressway backs up log files and call states, but I'm not 100% sure if call states are included.