
 MENU

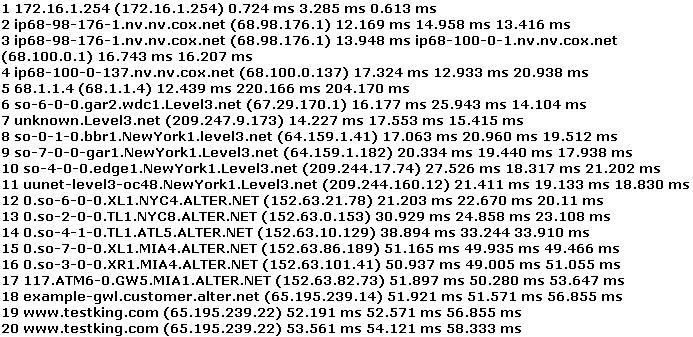
You have performed the traceroute below and notice that hops 19 and 20 both show the same IP address. What can be inferred from this output?
Suggested Answer: B
Get Premium CPEH-001 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
11 comments · newest first
ST
Stefany
12 months ago
I thought stateful inspection firewalls could do this too?
AN
Antonio
12 months ago
Definitely an application proxy, no doubt!
EL
Elbert
12 months ago
Wait, are we sure it’s not just a routing issue?
YO
Yolando
1 year ago
Totally agree, that’s a classic sign!
FL
Flo
1 year ago
Looks like a proxy firewall to me.
RO
Ronnie
1 year ago
I vaguely remember something about honeypots and firewalls in our study sessions, but I’m not sure how they relate to this traceroute output.
CH
Chantay
1 year ago
This feels familiar; I think it might be related to an application proxy firewall, but I’m not completely confident.
WI
Willard
1 year ago
I think we practiced a similar question where repeated IPs suggested a firewall, but I can’t recall the exact type.
CH
Cherelle
1 year ago
I remember discussing how multiple hops with the same IP could indicate a firewall, but I’m not sure if it’s specifically an application proxy or stateful inspection.
YO
Youlanda
1 year ago
Hmm, I'm a bit unsure about this one. I know the Mann-Whitney test is nonparametric, but I can't remember if it's more or less powerful than the t-test. I'll have to think this through carefully.
CA
Carlee
1 year ago
Hmm, I'm a bit unsure about this one. The options all look similar, and I want to make sure I understand the correct command to configure the syslog server. I'll need to double-check the F5 documentation to be certain.