
 MENU

You run nmap port Scan on 10.0.0.5 and attempt to gain banner/server information from services running on ports 21, 110 and 123. Here is the output of your scan results:
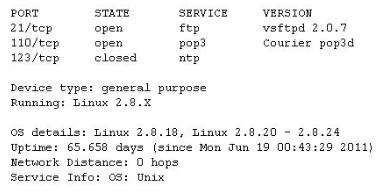
Which of the following nmap command did you run?
Suggested Answer: C
Get Premium CPEH-001 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
11 comments · newest first
MU
Murray
12 months ago
Wait, are you sure about A? Seems too easy.
CA
Carlota
12 months ago
I agree with A, that’s the most comprehensive command.
MA
Maile
1 year ago
No way, it’s definitely not C.
FA
Fallon
1 year ago
I think it might be B, but not sure.
FR
Frederick
1 year ago
Definitely option A, it includes service detection.
DO
Dortha
1 year ago
I don't recall seeing `-F` in our practice questions. It seems like a fast scan, but I'm not sure if it provides the same level of detail as the others.
RE
Reita
1 year ago
I keep mixing up the options, but I think `-O` is for OS detection, not just service info. So, I don't think option C is right.
AD
Adelina
1 year ago
I'm not entirely sure, but I think `-sV` is what we use for version detection. I feel like I saw a question similar to this in practice that used `-A` too.
VA
Vanesa
1 year ago
I remember that the `-A` option is for aggressive scanning, which includes service version detection. So, I think option A is likely correct.
AR
Arlie
1 year ago
This seems like a straightforward question about the ISO 9241 definition of usability. I think the key is to identify which aspect of usability is violated by the lack of a cancellation function on the car rental website.
HU
Hubert
1 year ago
Alright, I've got a strategy. I'll look at the different protocol and user name options in the filter commands and try to determine which one would allow tracing for just the "LAB\tester" user.