
 MENU

-- Exhibit --
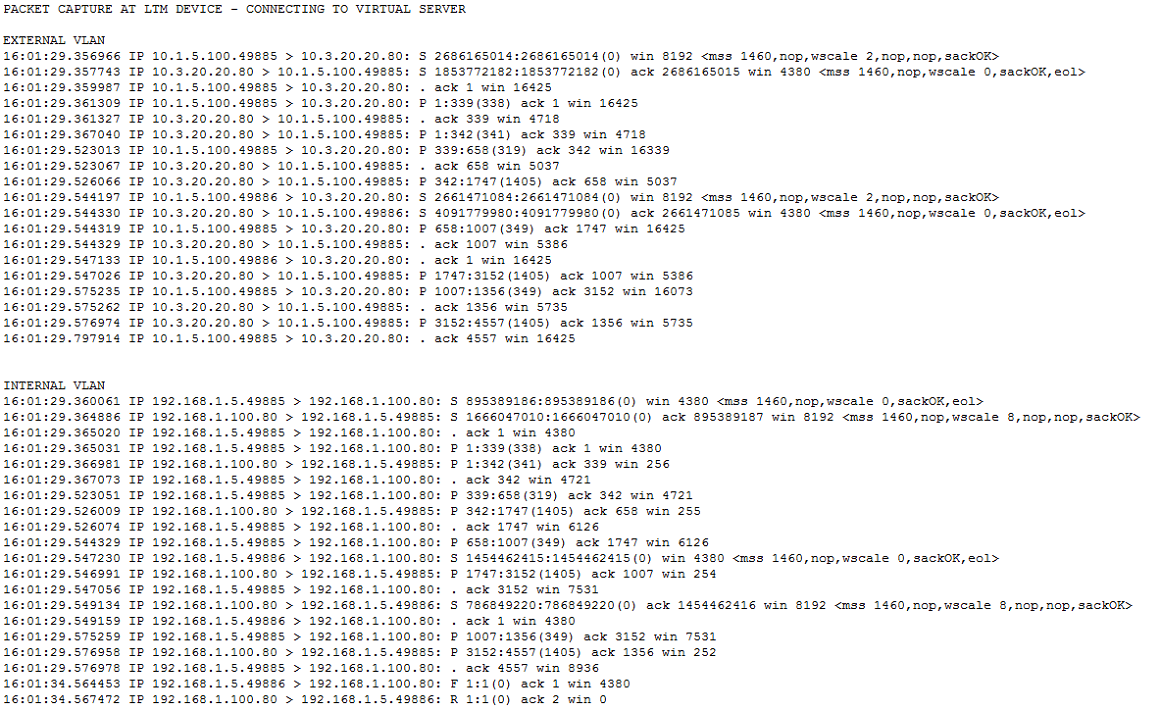
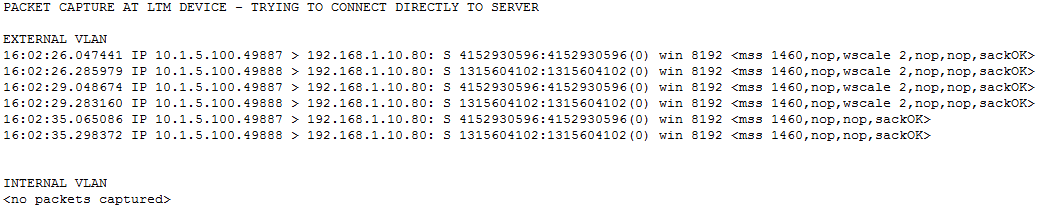
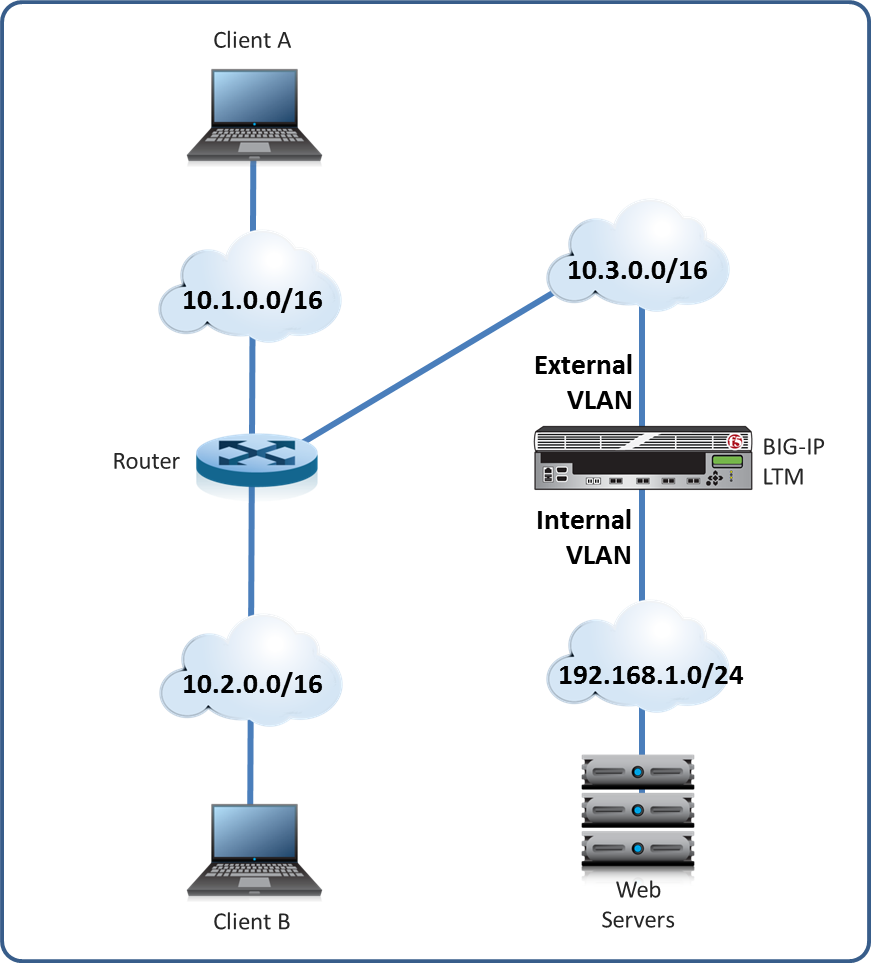
-- Exhibit --
Refer to the exhibits.
Users are able to access the application when connecting to the virtual server but are unsuccessful when connecting directly to the application servers. The LTM Specialist wants to allow direct access to the application servers.
Which configuration change resolves this problem?
Suggested Answer: D
Get Premium 301b Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
12 comments · newest first
YO
Yolando
12 months ago
Definitely need to configure that route to the web server subnet!
CA
Cassi
12 months ago
Wait, can we really access the app servers directly? Sounds odd.
IR
Irving
1 year ago
Disabling address translation? That seems risky!
JE
Jeniffer
1 year ago
I think a SNAT pool might be more effective here.
GA
Gayla
1 year ago
Looks like enabling port 443 is the way to go!
JO
Joesph
1 year ago
I’m leaning towards configuring a route to the web server subnet, but I’m not confident that's the right approach for this scenario.
IS
Isaiah
1 year ago
The IP Forwarding virtual server option sounds familiar, but I can't recall if it directly addresses access issues like this.
OR
Oretha
1 year ago
I think enabling port 443 on the virtual server could be a solution, but I feel like there might be more to it.
SH
Shantay
1 year ago
I remember something about SNAT pools from practice questions, but I'm not entirely sure how they apply here.
LE
Lenna
1 year ago
I've got a good feeling about this one. The question is pretty clear, and I think the answer is geo-locations. That seems like the most logical way to manage the geographic deployment in the Cisco Webex Control Hub.
TO
Tomas
1 year ago
I've got a good feeling about this one. The fact that the sensitive information was posted online suggests that data classification was the first control to fail. The company didn't properly classify and protect that data.
HE
Heike
1 year ago
Okay, I've got this. Based on my understanding, the next step after the initial findings review is to schedule follow-up actions and retesting. That's option B, so that's my answer.