
 MENU

-- Exhibit --
-- Exhibit --
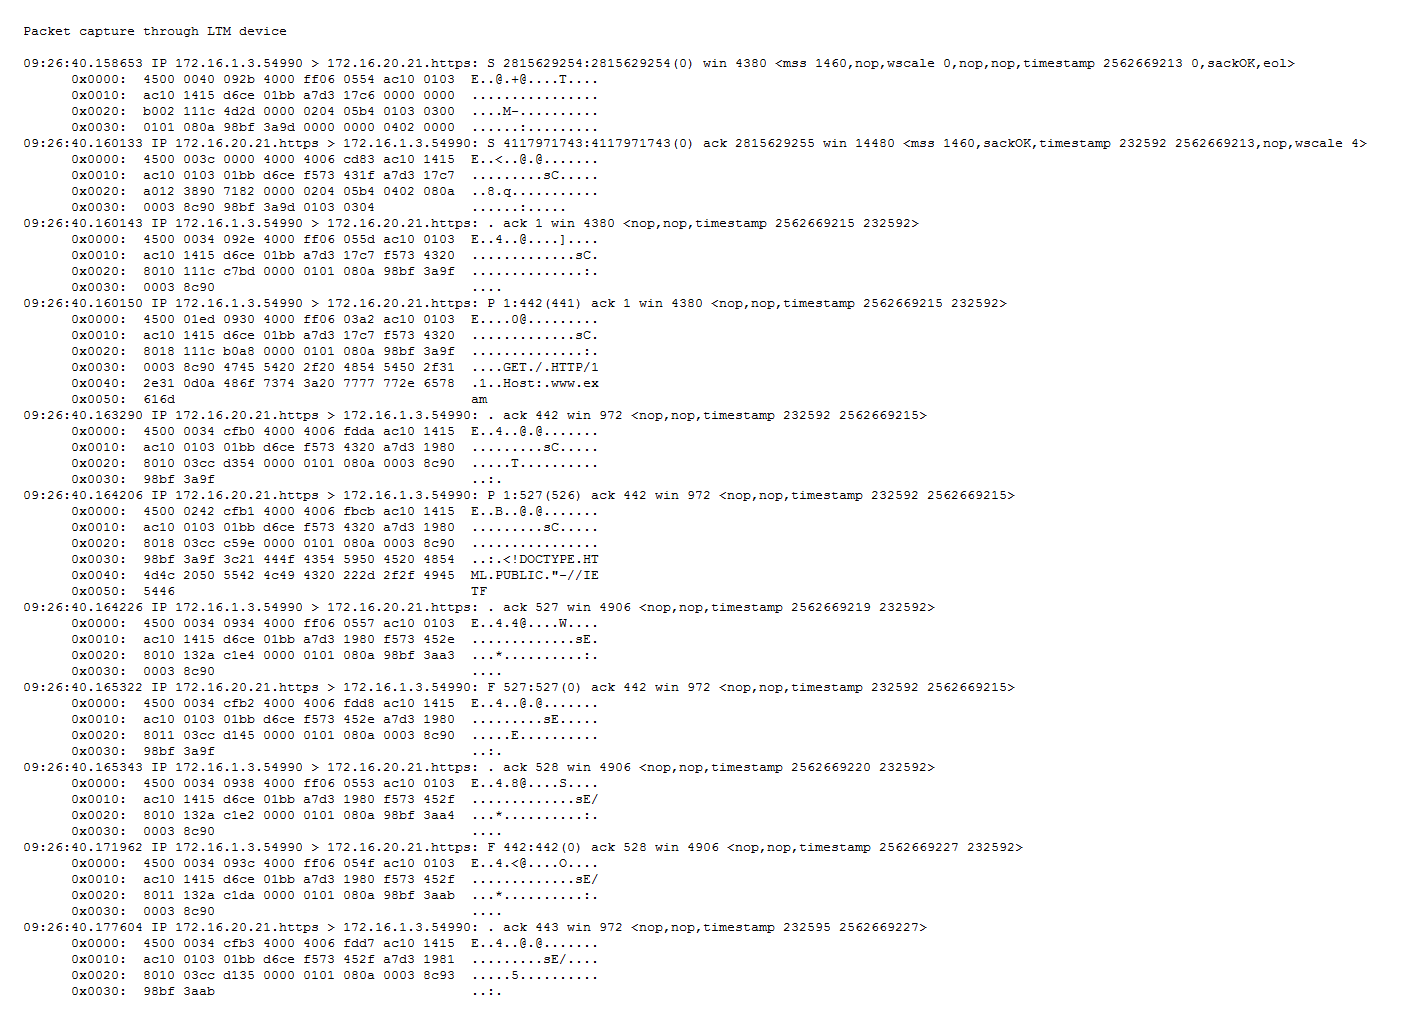
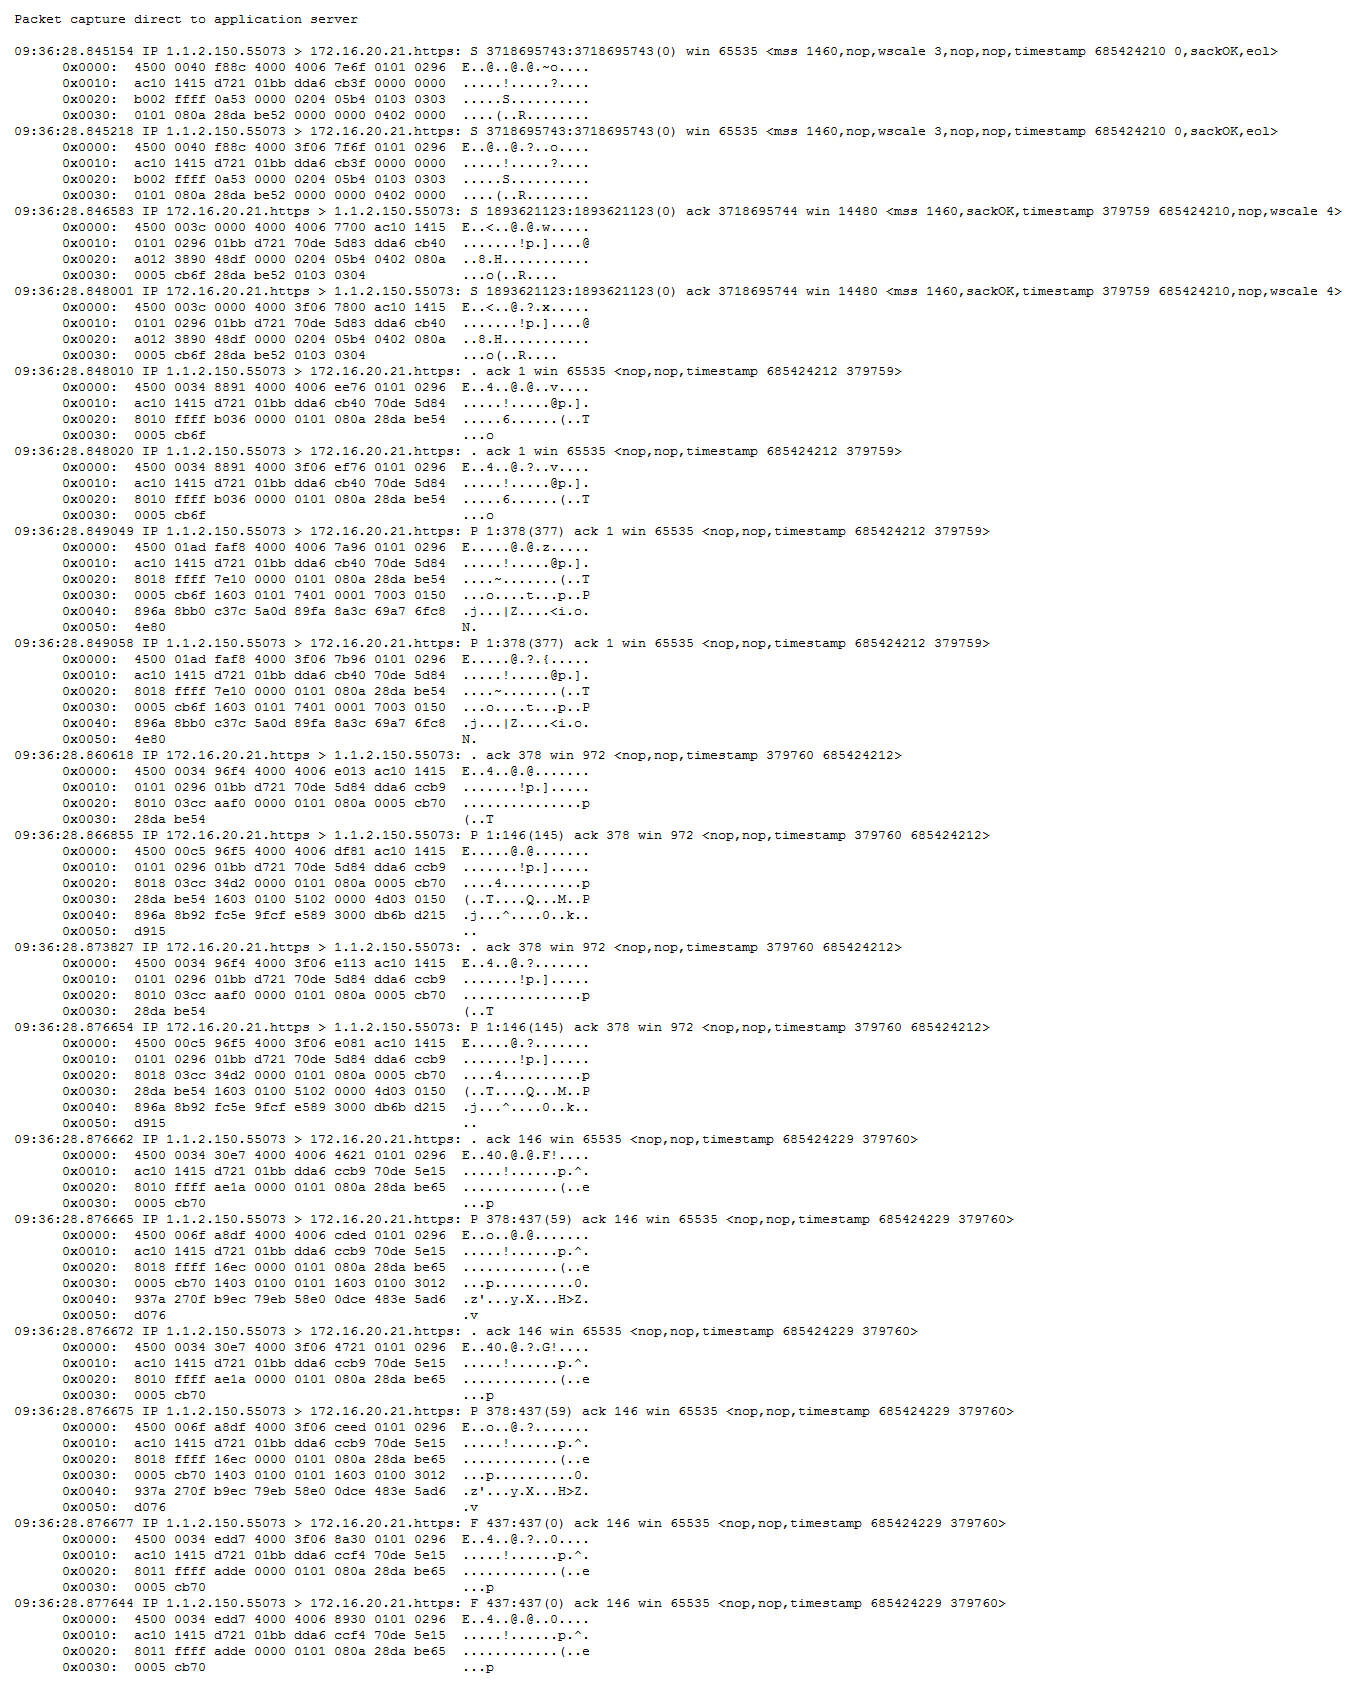
Refer to the exhibits.
An LTM Specialist has configured a virtual server to distribute connections to a pool of application servers and to offload SSL processing. The application fails to work as expected when connecting to the virtual server. It does work when clients connect directly to the application. Two packet captures were taken at the application server.
What is the root cause of the problem?
Suggested Answer: B
Get Premium 301b Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
11 comments · newest first
SO
Son
12 months ago
Wait, are the app servers even listening on port 80?
IN
Inocencia
12 months ago
Nah, it’s probably the LTM sending non-SSL traffic.
ME
Mel
12 months ago
But what if the SSL handshake is failing instead?
DO
Dong
1 year ago
I agree, that’s definitely a common issue!
TI
Tish
1 year ago
The virtual server needs a clientSSL profile assigned.
ST
Stefanie
1 year ago
I think the application servers need to be listening on the correct ports, but I can't recall if that’s the main issue here. It could be related to the SSL setup instead.
VI
Viola
1 year ago
I feel like I’ve seen a question about SSL handshakes failing before. If that’s the case, option D might be the right answer, but I’m not completely confident.
BE
Beckie
1 year ago
I'm not entirely sure, but I think if the LTM is sending non-SSL traffic to an SSL port, that could definitely cause issues. It sounds familiar from practice questions.
CA
Carla
1 year ago
I remember something about SSL profiles being crucial for proper communication. Could it be that the virtual server just doesn't have a clientSSL profile assigned?
KE
Keva
1 year ago
This is a tricky one. There are a lot of moving parts to consider - the customer, the supplier, the project team. I'm going to have to really focus to work through this systematically.
BE
Bettyann
1 year ago
This looks like a tricky MPLS question. I'll need to carefully analyze the information provided and think through the different protection scenarios.