
 MENU

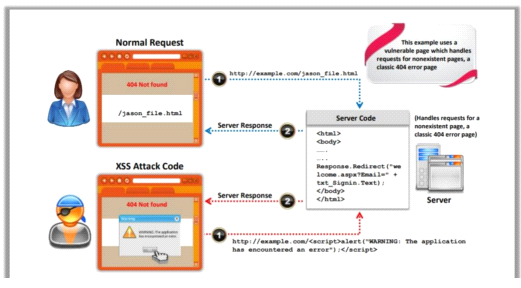
An attacker, in an attempt to exploit the vulnerability in the dynamically generated welcome page, inserted code at the end of the company's URL as follows:
http://technosoft.com.com/. Identify the attack demonstrated in the above scenario.
Suggested Answer: A
Get Premium 312-39 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
12 comments · newest first
KA
Kathryn
11 months ago
Seems too simple for a real attack, right?
TA
Tammy
11 months ago
No doubt, it's XSS for sure!
LA
Lavera
12 months ago
Wait, are we sure it's not SQL Injection?
MA
Mariann
12 months ago
I agree, that script tag is a giveaway.
CA
Caitlin
1 year ago
Definitely a Cross-site Scripting Attack!
OR
Oretha
1 year ago
I thought Denial-of-Service Attack was more about overwhelming a server? This seems more like XSS, but I’m still a bit confused.
CH
Chana
1 year ago
Definitely feels like a Cross-site Scripting Attack to me. The alert message in the script tag is a classic example.
JO
Joaquin
1 year ago
I'm not entirely sure, but it seems like it could also be an SQL Injection Attack? I remember something about code being inserted, but this looks different.
KA
Kanisha
1 year ago
I think this is a Cross-site Scripting Attack since the attacker is injecting a script into the URL. It reminds me of a practice question we did on XSS.
EV
Eveline
1 year ago
Wait, I'm a little confused. I thought the traffic-table was more for monitoring and analyzing traffic, not for actually setting the parameters. I'll need to double-check my notes to make sure I'm remembering this correctly.
ME
Melynda
1 year ago
This question seems straightforward, I think I know the answer.
DA
Daniela
1 year ago
Hmm, I'm not entirely sure about the answer here. I'll need to think through the different options and try to eliminate the ones that don't seem right.