
Free Preparation Discussions
 MENU

CompTIA CAS-005 Exam Questions
Free CompTIA CAS-005 Exam Actual Questions
Note: Premium Questions for CAS-005 were last updated On Oct. 29, 2026 (see below)
A vulnerability can on a web server identified the following:
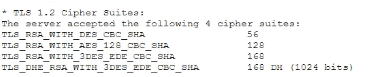
Which of the following actions would most likely eliminate on path decryption attacks? (Select two).
On-path decryption attacks, such as BEAST (Browser Exploit Against SSL/TLS) and other related vulnerabilities, often exploit weaknesses in the implementation of CBC (Cipher Block Chaining) mode. To mitigate these attacks, the following actions are recommended:
B . Removing support for CBC-based key exchange and signing algorithms: CBC mode is vulnerable to certain attacks like BEAST. By removing support for CBC-based ciphers, you can eliminate one of the primary vectors for these attacks. Instead, use modern cipher modes like GCM (Galois/Counter Mode) which offer better security properties.
C . Adding TLS_ECDHE_ECDSA_WITH_AES_256_GCM_SHA256: This cipher suite uses Elliptic Curve Diffie-Hellman Ephemeral (ECDHE) for key exchange, which provides perfect forward secrecy. It also uses AES in GCM mode, which is not susceptible to the same attacks as CBC. SHA-256 is a strong hash function that ensures data integrity.
CompTIA Security+ Study Guide
NIST SP 800-52 Rev. 2, 'Guidelines for the Selection, Configuration, and Use of Transport Layer Security (TLS) Implementations'
OWASP (Open Web Application Security Project) guidelines on cryptography and secure communication
A company developed a new solution that needs to track any changes to the data, and the changes need to be quickly identified. If any changes are attempted without prior approval, multiple events must be triggered, such as:
Raising alerts
Blocking the unapproved changes
Quickly removing access to the data
Which of the following solutions best meets these requirements?
A company is having issues with its vulnerability management program New devices/lPs are added and dropped regularly, making the vulnerability report inconsistent Which of the following actions should the company lake to most likely improve the vulnerability management process'
To improve the vulnerability management process in an environment where new devices/IPs are added and dropped regularly, the company should perform regular discovery scanning throughout the IT landscape using the vulnerability management tool. Here's why:
Accurate Asset Inventory: Regular discovery scans help maintain an up-to-date inventory of all assets, ensuring that the vulnerability management process includes all relevant devices and IPs.
Consistency in Reporting: By continuously discovering and scanning new and existing assets, the company can generate consistent and comprehensive vulnerability reports that reflect the current state of the network.
Proactive Management: Regular scans enable the organization to proactively identify and address vulnerabilities on new and existing assets, reducing the window of exposure to potential threats.
CompTIA Security+ SY0-601 Study Guide by Mike Chapple and David Seidl
NIST Special Publication 800-40: Guide to Enterprise Patch Management Technologies
CIS Controls: Control 1 - Inventory and Control ofHardware Assets
A global organization is reviewing potential vendors to outsource a critical payroll function. Each vendor's plan includes using local resources in multiple regions to ensure compliance with all regulations. The organization's Chief Information Security Officer is conducting a risk assessment on the potential outsourcing vendors' subprocessors. Which of the following best explains the need for this risk assessment?
Per SecurityX CAS-005 GRC principles, outsourcing a function does not transfer accountability for protecting personally identifiable information (PII). While subprocessors handle data, the originating organization remains responsible under most data protection laws and frameworks (e.g., GDPR, CCPA).
Due care in procurement (option B) is important, but it is a supporting concept, not the primary driver in this context.
Jurisdictional compliance (option D) is a requirement, but the underlying reason for risk assessment is that accountability for PII protection remains with the organization.
In order to follow new regulations, the Chief Information Security Officer plans to use a defense-in-depth approach for a perimeter network. Which of the following protections would best achieve this goal?
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Christopher Wright
1 month agoAngela Rodriguez
2 months agoSarah Flores
2 months agoEmma Perez
2 months agoAngela Martinez
3 months agoEdward Murphy
3 months agoBrian White
3 months agoLisa Murphy
4 months agoKimberly Garcia
4 months agoJessica Nguyen
4 months agoJustin Morgan
5 months agoAnthony Phillips
5 months agoGary King
5 months agoJason Roberts
6 months agoMichael Martinez
6 months agoThomas Morgan
7 months agoAngela Turner
6 months agoJustin Flores
6 months agoPaul Evans
6 months agoRachel Nguyen
6 months agoDorothy Turner
6 months agoPauline
7 months agoMarsha
7 months agoBelen
8 months agoLashaunda
8 months agoOlga
8 months agoMichal
9 months agoPok
9 months agoVanda
9 months agoShawnta
9 months agoLeatha
10 months agoAn
10 months agoDesirae
10 months agoGayla
10 months agoCecil
11 months agoLino
11 months agoHildred
11 months agoArthur
11 months agoJose
12 months agoIzetta
12 months agoCassie
1 year agoSol
1 year agoBeatriz
1 year agoLeigha
1 year agoLarae
1 year agoJesus
1 year agoTu
1 year agoGilma
1 year agoPhillip
1 year agoRolf
1 year agoMargart
1 year agoStanford
1 year agoRessie
2 years agoMillie
2 years agoLouis
2 years agoJacqueline
2 years agoMaryann
2 years agoNobuko
2 years agoOzell
2 years agoSanda
2 years agoViola
2 years agoPortia
2 years agoKristel
2 years agoBrandon
2 years agoLouvenia
2 years ago