
Free Preparation Discussions
 MENU

CompTIA CS0-004 Exam - Topic 4 Question 7 Discussion
Topic #: 4
The Chief Information Security Officer (CISO) reviews the following security operations metrics from the last month:
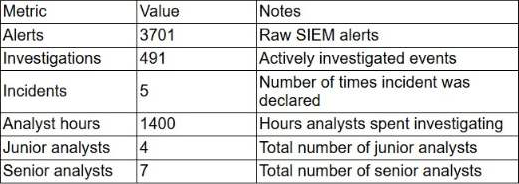
Which of the following is the best action to improve overall security operations efficiency?
The most direct method for improving SOC efficiency when excessive alerts are non-actionable is to identify the detections generating that noise and perform rule and alert tuning. Non-actionable detections consume analyst time, increase queue depth, contribute to alert fatigue, and can obscure genuinely malicious activity. Tuning may include adjusting thresholds, refining correlation logic, adding exclusions for legitimate behavior, improving indicator context, modifying detection conditions, or disabling rules that consistently generate false positives without meaningful security value.
A cloud security posture management platform may improve context for cloud-related findings, but it does not directly correct poorly performing detection logic across the broader SOC. Playbooks improve consistency and reduce investigation variability, particularly for junior analysts, but they still force personnel to process alerts that should not have been generated. Training can improve analyst performance, yet it also fails to address the source of excessive non-actionable notifications.
The CS0-004 Security Operations objectives explicitly identify efficiency and process improvement, including standardized processes, automation and orchestration, data enrichment, rule/alert tuning, dashboard creation, and technology integration.
Therefore, the optimal operational improvement is to reduce unnecessary workload at the detection layer itself.
Study Guide Reference: Security Operations Efficiency and Process Improvement Data Enrichment Rule/Alert Tuning SOC Optimization.
Currently there are no comments in this discussion, be the first to comment!