
Free Preparation Discussions
 MENU

Cisco 300-220 Exam Questions
- Cisco Certified Network Professional CCNP Certifications
- Cisco Certified Network Professional Cybersecurity Certifications
- Topic 1: Threat Hunting Fundamentals: Covers core threat hunting concepts using maturity models, the Pyramid of Pain, and standards like MITRE ATT&CK and CAPEC. Includes interpreting threat intelligence reports to understand adversary tactics, techniques, and procedures.
- Topic 2: Threat Modeling Techniques: Focuses on selecting and applying threat modeling approaches using MITRE ATT&CK, CAPEC, and the Cyber Kill Chain to prioritize attacks. Also covers threat intelligence lifecycle management and structured versus unstructured hunting.
- Topic 3: Threat Actor Attribution Techniques: Covers identifying and attributing threat actors through log analysis, TTP interpretation, and distinguishing real attacks from authorized assessments. Includes using Pyramid of Pain artifacts to detect advanced persistent threats.
- Topic 4: Threat Hunting Techniques: Covers hands-on hunting skills including scripting, cloud-native hunting, C2 analysis, traffic inspection, code-level analysis, IoT device assessment, and memory forensics using tools like Volatility.
- Topic 5: Threat Hunting Processes: Addresses procedural aspects such as identifying memory-resident attacks, reverse engineering, closing detection gaps, and building runbooks. Includes recommending tooling, deception techniques, and security countermeasures.
- Topic 6: Threat Hunting Outcomes: Focuses on post-hunt actions including diagnosing analytical gaps, recommending C2 mitigations, advancing hunt maturity, improving detection methodologies, and communicating findings to drive organizational change.
Free Cisco 300-220 Exam Actual Questions
Note: Premium Questions for 300-220 were last updated On Oct. 17, 2026 (see below)
The SOC team receives an alert about a user sign-in from an unusual country. After investigating the SIEM logs, the team confirms the user never signed in from that country. The incident is reported to the IT administrator who resets the user's password. Which threat hunting phase was initially used?
The correct answer is Collect and process intelligence and data. In this scenario, the initial threat hunting phase occurred when the SOC team received the alert and began analyzing SIEM logs to validate whether the activity was legitimate or malicious. This aligns directly with the first phase of the threat hunting lifecycle, which focuses on gathering, normalizing, and analyzing security-relevant data.
Threat hunting is a structured, hypothesis-driven process, but it always begins with data collection and intelligence processing. This includes ingesting logs from identity providers, authentication systems, cloud platforms, VPNs, and endpoint telemetry into a SIEM. In this case, the alert regarding a sign-in from an unusual country triggered analysts to examine historical login patterns and geolocation data. By confirming that the user had never authenticated from that country, the team established that the event was anomalous and likely malicious.
Option B (Response and resolution) occurred after the initial phase, when the IT administrator reset the user's password to contain the threat. Option C (Hypothesis) would involve formulating a theory such as ''the account may be compromised due to credential theft,'' but this step requires validated data first. Option D (Post-incident review) only happens after the incident has been fully resolved and lessons learned are documented.
From a professional cybersecurity operations perspective, this phase is critical because high-quality data determines hunt effectiveness. Poor log coverage or incomplete identity telemetry would prevent analysts from confidently confirming the anomaly. This example also highlights why identity-related telemetry is foundational to modern threat hunting---compromised credentials remain one of the most common initial access vectors.
In short, before a SOC can hypothesize, respond, or improve controls, it must first collect and process accurate intelligence and data, making option A the correct answer.
What is the classification of the pass-the-hash technique according to the MITRE ATT&CK framework?
The pass-the-hash (PtH) technique is classified under Credential Access in the MITRE ATT&CK framework. Specifically, it aligns with the Credential Access tactic (TA0006) and the technique Use Alternate Authentication Material (T1550), sub-technique Pass the Hash (T1550.002). This classification is based on the attacker's primary objective: abusing stolen credential material---in this case, NTLM password hashes---to authenticate to systems without knowing the actual plaintext password.
From a professional cybersecurity and threat hunting perspective, PtH exploits weaknesses in how Windows authentication mechanisms handle credential storage and reuse. When users authenticate to a system, password hashes may be cached in memory or stored in places such as LSASS (Local Security Authority Subsystem Service). If an attacker gains administrative or SYSTEM-level access to a host, they can extract these hashes and reuse them to authenticate to other systems across the environment.
Although pass-the-hash is often observed during lateral movement, MITRE intentionally classifies it under Credential Access because the defining action is the theft and misuse of credential material, not the movement itself. Lateral movement is a downstream outcome enabled by the stolen credentials, but the core technique is about accessing and abusing authentication secrets.
This distinction is important for threat hunters and detection engineers. When hunting for PtH activity, defenders focus on indicators such as abnormal NTLM authentication events, logons using NTLM where Kerberos is expected, reuse of the same hash across multiple systems, and suspicious access to LSASS memory. Endpoint telemetry, Windows Security Event Logs (e.g., Event IDs 4624 and 4672), and EDR memory access alerts are commonly used data sources.
Understanding PtH as a credential access technique helps security teams prioritize protections such as credential guard, LSASS hardening, disabling NTLM where possible, enforcing least privilege, and monitoring authentication anomalies. This classification also reinforces a core professional principle: identity is the new perimeter, and protecting credential material is foundational to modern threat hunting and defense.
According to the MITRE ATT&CK framework, how is the password spraying technique classified?
The correct answer is Credential Access. In the MITRE ATT&CK framework, password spraying is classified under the Credential Access tactic (TA0006), specifically technique T1110.003 -- Password Spraying. This classification is based on the attacker's primary objective: gaining valid credentials by systematically attempting a small number of common or weak passwords across many user accounts.
Password spraying differs from brute-force attacks in that it intentionally avoids rapid or repeated attempts against a single account, thereby evading account lockout controls and basic detection mechanisms. Instead, attackers ''spray'' one password (for example, Winter2025! or Password123) across a large number of users, exploiting the likelihood that at least one account will use that password.
Although successful password spraying often leads to initial access, MITRE classifies it under Credential Access because the technique's defining action is the acquisition of credentials, not the system entry itself. Initial access is the outcome, while credential theft is the method. This distinction is critical for threat hunters, as it guides where detections and controls should be focused.
From a professional threat hunting perspective, defenders monitor authentication telemetry such as failed and successful logins across identity providers, VPNs, cloud services, and email platforms. Indicators include multiple authentication failures across many accounts from a single source IP, followed by one or more successful logins. Identity-centric logging and anomaly detection are foundational here, reinforcing the principle that identity is the primary attack surface in modern environments.
Understanding password spraying as a credential access technique helps organizations prioritize protections such as strong password policies, MFA enforcement, adaptive authentication, and detection logic tuned for low-and-slow authentication abuse.
During an investigation, analysts observe that attackers consistently avoid PowerShell logging, disable AMSI, and prefer WMI for execution. Why is this information critical for attribution?
The correct answer is it reflects the attacker's operational preferences. Attribution relies on understanding how attackers operate, not just what tools they use.
Operational preferences---such as avoiding PowerShell logging, disabling AMSI, and favoring WMI---are behavioral signatures. These patterns often persist across campaigns and are documented in threat intelligence reports associated with specific adversaries.
Option A is incorrect because malware families change frequently. Option B is unreliable due to infrastructure rotation. Option D is unrelated to post-access tradecraft.
Professional attribution focuses on:
Execution methods
Defensive evasion choices
Tooling preferences
Workflow consistency
Mapping these behaviors to MITRE ATT&CK techniques enables analysts to compare findings against known threat actor profiles. This provides higher confidence attribution than artifact-based indicators.
Thus, option C is the correct answer.
Refer to the exhibit.
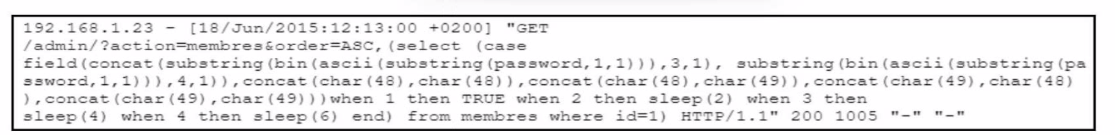
The cybersecurity team at a company detects an ongoing attack directed at the web server that hosts the company website. The team analyzes the logs of the web application firewall and discovers several HTTP requests encoded in Base64. The team decodes the payloads and retrieves the HTTP requests. What did the attackers use to exploit the server?
The correct answer is SQL injection. The decoded HTTP request shown in the exhibit contains multiple unmistakable indicators of a SQL injection attack, including the use of SQL keywords and functions such as SELECT, CASE, SUBSTRING, ASCII, BIN, and conditional SLEEP() statements. These elements are characteristic of time-based blind SQL injection, a technique attackers use to extract database information when direct query results are not visible.
From a professional cybersecurity perspective, the presence of expressions like:
SELECT (CASE WHEN ... THEN SLEEP(x))
SUBSTRING(password,1,1)
ASCII() and binary conversions
indicates that the attacker is probing the backend database character by character and using response timing to infer whether conditions are true or false. This is a well-known exploitation method used when error messages or query output are suppressed by the application.
The use of Base64 encoding does not represent the attack itself but rather an obfuscation technique to evade basic web application firewall (WAF) signatures and logging visibility. Encoding payloads allows attackers to bypass simple pattern-matching defenses, but once decoded, the underlying SQL injection becomes evident.
Option A (Unicode encoding) is incorrect because Unicode is commonly used for evasion, not exploitation. Option C (directory traversal) typically involves sequences like ../ to access filesystem paths, which are not present. Option D (XSS) targets client-side script execution and would include JavaScript payloads rather than database-focused logic.
According to the MITRE ATT&CK framework, this activity maps to Initial Access -- Exploit Public-Facing Application (T1190). SQL injection remains one of the most exploited vulnerabilities in public-facing applications due to poor input validation and insecure coding practices.
For threat hunters and defenders, this scenario reinforces the importance of deep payload inspection, decoding obfuscated requests, monitoring for anomalous database query behavior, and enforcing secure development practices such as parameterized queries and input sanitization. SQL injection continues to be a high-impact, real-world attack vector despite being well understood, making it a critical focus area in web application threat hunting.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Lisa Thomas
27 days agoPaul Brown
2 months agoDennis Campbell
2 months agoGerald Flores
3 months agoTimothy Nguyen
3 months agoAshley Campbell
4 months agoTimothy Jackson
4 months agoAmy Lopez
5 months agoDonna Robinson
5 months agoEmily Torres
5 months agoDennis Turner
6 months agoKenneth Bell
6 months agoRyan Garcia
5 months agoAdam Hill
6 months agoEric Roberts
6 months agoStephanie Rivera
5 months agoIsabelle
6 months agoBuddy
7 months agoSoledad
7 months agoGlynda
7 months agoAlfreda
7 months ago