Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Welcome to Pass4Success

- Free Preparation Discussions

Cisco 350-901 Exam - Topic 12 Question 49 Discussion

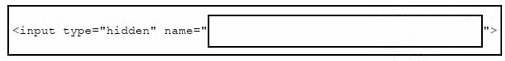
Refer to the exhibit.A network engineer created a simple Python Flask application but must incorporate a CSRF token. Which code snippet must be added in the blank in the script to manually incorporate the token?
A) _access_tokenM value=M{{ csrf_token}}
B) _csrMoken' value='{{ csrf_grant()}}
C) _csrMoken' value='{{ csrf_token()}}
D) _xssjoken' value='{{ csrMoken}}

Cisco 350-901 Exam - Topic 12 Question 49 Discussion

Actual exam question for Cisco's 350-901 exam
Question #: 49
Topic #: 12
[All 350-901 Questions]

Refer to the exhibit.

A network engineer created a simple Python Flask application but must incorporate a CSRF token. Which code snippet must be added in the blank in the script to manually incorporate the token?

Show Suggested Answer Hide Answer
Suggested Answer: A

Contribute your Thoughts:

0/2000 characters
Delisa
10 months ago
Not sure about B, that doesn't look right to me.
upvoted 0 times
...
Marget
10 months ago
I agree with C, it's the standard for Flask apps.
upvoted 0 times
...
Geoffrey
10 months ago
Wait, is D even a real option? Sounds sketchy.
upvoted 0 times
...
Tawna
11 months ago
I thought it was A at first, but C makes more sense.
upvoted 0 times
...
Jutta
11 months ago
Definitely C, that's the correct way to include a CSRF token!
upvoted 0 times
...
Walton
11 months ago
I remember studying CSRF tokens, and I think the correct function is `csrf_token()`. Option C seems to match what I learned, but I hope I’m not confusing it with another framework.
upvoted 0 times
...
Rene
11 months ago
I might be mixing things up, but I feel like the CSRF token should be included in the form as a hidden input. I think option C looks familiar, but I'm not completely confident.
upvoted 0 times
...
Chantell
11 months ago
This question reminds me of a practice quiz where we had to identify the correct syntax for Flask. I feel like `csrf_token()` is the right one, but I can't recall the exact format.
upvoted 0 times
...
Pa
11 months ago
I think I remember that the CSRF token is usually generated with a specific function, but I'm not sure if it's `csrf_token()` or something else.
upvoted 0 times
...
Latia
11 months ago
I'm pretty confident that option B is the correct answer here. IGMP snooping is designed to optimize multicast traffic, so the OLT should only send one join message in this case.
upvoted 0 times
...
Providencia
11 months ago
The heuristics could be a good option too, as they would guide the exploratory testing and could benefit from informal reviews.
upvoted 0 times
...
Tanesha
11 months ago
I remember we discussed screens and screen schemes in class, but I'm a bit confused about how many we actually need here.
upvoted 0 times
...
Trinidad
11 months ago
Okay, let's break this down. The key is understanding what qualifies as "personal information" and the appropriate controls required. I'll evaluate each option against that criteria.
upvoted 0 times
...
Ashton
11 months ago
This is a tricky one. I'll need to think through the different options carefully to determine the most effective approach.
upvoted 0 times
...
Lisha
11 months ago
Hmm, this seems straightforward. I'll need to double-check the GVP 8.x configuration details, but I'm pretty confident I can handle this.
upvoted 0 times
...
Una
1 year ago
Option D? Really? That looks like something a junior dev would come up with. Let's keep it professional, folks.
upvoted 0 times
Layla
1 year ago
A: Definitely, we need to maintain a high standard in our code. Option D does seem like a junior dev mistake.
upvoted 0 times
...
Sanjuana
1 year ago
B: I agree, option C is the most professional choice for incorporating the CSRF token.
upvoted 0 times
...
Claudia
1 year ago
A: I think option C is the correct one. It includes the csrf_token function.
upvoted 0 times
...
...
Clay
1 year ago
Ah, the good ol' CSRF token. Gotta keep those pesky hackers at bay, am I right?
upvoted 0 times
...
Alpha
1 year ago
Hold up, what's a CSRF token? Is this some kind of secret handshake I need to know about?
upvoted 0 times
Tandra
1 year ago
Deonna: Exactly! It helps verify the authenticity of the request.
upvoted 0 times
...
Deonna
1 year ago
User 2: So it's like a secret code to make sure the request is coming from the right place?
upvoted 0 times
...
Dorcas
1 year ago
User 1: A CSRF token is a security measure to prevent cross-site request forgery attacks.
upvoted 0 times
...
...
Luke
1 year ago
Wow, a CSRF token? I thought that was only for enterprise-level apps. This engineer is really on the ball!
upvoted 0 times
Bobbye
1 year ago
Nobuko: Thanks for clarifying, that will help secure the Flask application.
upvoted 0 times
...
Beth
1 year ago
User 3: The correct code snippet to add is C) _csrMoken\' value=\'{{ csrf_token()}}\'.
upvoted 0 times
...
Nobuko
1 year ago
User 2: I agree, it helps prevent cross-site request forgery attacks.
upvoted 0 times
...
Earleen
1 year ago
User 1: Yeah, incorporating a CSRF token is crucial for security.
upvoted 0 times
...
Long
1 year ago
Alyce: Thanks for clarifying, that will help secure the Flask application.
upvoted 0 times
...
Audria
1 year ago
User 3: The correct code snippet to add is C) _csrMoken\' value=\'{{ csrf_token()}}\'.
upvoted 0 times
...
Alyce
1 year ago
User 2: I agree, it helps prevent cross-site request forgery attacks.
upvoted 0 times
...
Essie
1 year ago
User 1: Yeah, incorporating a CSRF token is crucial for security.
upvoted 0 times
...
...
Lavelle
1 year ago
But C makes more sense because it calls the csrf_token function.
upvoted 0 times
...
Burma
1 year ago
Option C is the correct answer. That's the standard syntax for retrieving the CSRF token in a Flask application.
upvoted 0 times
Arlene
1 year ago
Dannette: Exactly, it's important for security purposes.
upvoted 0 times
...
Joye
1 year ago
User 3: Good choice, that's the standard way to incorporate the CSRF token in Flask.
upvoted 0 times
...
Dannette
1 year ago
User 2: Thanks for confirming, I'll go with that option.
upvoted 0 times
...
Breana
1 year ago
User 1: I think the answer is C) _csrMoken\' value=\'{{ csrf_token()}}
upvoted 0 times
...
...
Ronnie
1 year ago
I disagree, I believe the correct answer is A.
upvoted 0 times
...
Lavelle
1 year ago
I think the answer is C.
upvoted 0 times
...

Save Cancel