Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Welcome to Pass4Success

- Free Preparation Discussions

Cisco 350-601 Exam - Topic 2 Question 34 Discussion

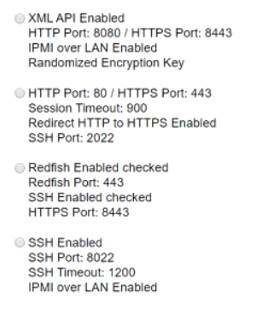
An engineer implements a Cisco UCS C-Series Server that must adhere to these security requirements:Unencrypted communication must be disabled.The session timeout must not exceed 15 minutes.Unencrypted traffic must be automatically diverted.CLI-based management must use nondefault ports.Which configuration set meets these requirements?
B) Option B
A) Option A
C) Option C
D) Option D

Cisco 350-601 Exam - Topic 2 Question 34 Discussion

Actual exam question for Cisco's 350-601 exam
Question #: 34
Topic #: 2
[All 350-601 Questions]

An engineer implements a Cisco UCS C-Series Server that must adhere to these security requirements:

Unencrypted communication must be disabled.

The session timeout must not exceed 15 minutes.

Unencrypted traffic must be automatically diverted.

CLI-based management must use nondefault ports.

Which configuration set meets these requirements?
Show Suggested Answer Hide Answer
Suggested Answer: B

Contribute your Thoughts:

0/2000 characters
Caprice
10 months ago
I disagree, I don't think nondefault ports are necessary for CLI management.
upvoted 0 times
...
Louis
10 months ago
Wait, unencrypted traffic is automatically diverted? That seems a bit extreme.
upvoted 0 times
...
Margurite
10 months ago
Definitely going with Option C!
upvoted 0 times
...
Adolph
11 months ago
I think Option A is the right choice.
upvoted 0 times
...
Daren
11 months ago
Option B meets all the security requirements.
upvoted 0 times
...
Jennifer
11 months ago
I’m a bit confused about how unencrypted traffic is diverted automatically. I think it was mentioned in our study materials, but I can't pinpoint the exact configuration.
upvoted 0 times
...
Ricarda
11 months ago
I definitely remember something about using nondefault ports for CLI management. I hope one of these options covers that requirement clearly.
upvoted 0 times
...
Antonio
11 months ago
I remember we discussed the importance of disabling unencrypted communication, but I'm not sure which option specifically addresses that.
upvoted 0 times
...
Kimbery
11 months ago
I think we practiced a similar question where session timeouts were a focus. I feel like it was 15 minutes, but I can't recall the exact configuration steps.
upvoted 0 times
...
Micaela
11 months ago
I feel pretty confident about this one. The hex string format and the answer choices make me think this is likely a question about Base64 encoding. I'll go with that.
upvoted 0 times
...
Jolanda
11 months ago
I feel pretty confident that the egress LER is the right answer here. The MPLS label is added at the ingress, so it makes sense that it would be removed at the egress before the packet reaches the customer network. I'll mark that one down.
upvoted 0 times
...
Page
11 months ago
Easy peasy! The most important thing is to show the potential impact of current threats. That's going to be the biggest driver for getting stakeholder buy-in. The other options are interesting, but they don't pack the same punch in terms of urgency and necessity. I'd focus my response on that threat impact angle.
upvoted 0 times
...
Bok
11 months ago
Okay, let me think this through. TLS provides encryption and authentication, so the client can be assured the server is who it claims to be. I'd go with B as the best answer.
upvoted 0 times
...
Stephane
11 months ago
I remember learning about this in my networking class. I believe the correct answer is C. 183 Session in Progress, which indicates that the REFER request is being processed.
upvoted 0 times
...
Herman
11 months ago
I vaguely recall that intermediaries can sometimes add delay, so option C might lead to better performance, but I could be mistaken.
upvoted 0 times
...

Save Cancel