
 MENU

Refer to the exhibit.
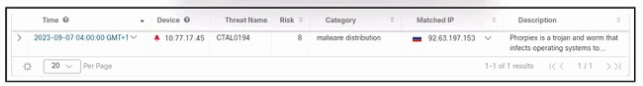
Refer to the exhibit. A security engineer deployed Cisco Secure XDR, and during testing, the log entry shows a security incident. Which action must the engineer take first?
Suggested Answer: C
Get Premium 300-740 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
18 comments · newest first
FE
Felicidad
10 months ago
Surprised that rebuilding the endpoint is even an option here!
FR
Francene
10 months ago
I think blocking the IP might be more effective first.
MA
Marquetta
11 months ago
Totally agree, isolating is crucial!
PE
Pete
11 months ago
Wait, why not just uninstall the malware right away?
BE
Bettina
11 months ago
The first step should be to isolate the endpoint.
KA
Kathryn
11 months ago
I practiced a question like this, and I think rebuilding the endpoint is too drastic to start with. Isolating seems safer.
RE
Reuben
11 months ago
I’m leaning towards option C, but I keep second-guessing myself about whether I should consider the malware first.
JE
Jesusa
12 months ago
I remember a similar question where blocking an IP was the first step, but in this case, it feels like isolating the endpoint might be more appropriate.
VI
Vivan
12 months ago
I think isolating the endpoint is crucial first, but I'm not entirely sure if that’s the best immediate action.
IN
Ines
12 months ago
Blocking the IP address could be a good start, but I want to make sure that's the most effective action to take first before jumping to that conclusion.
LA
Laurel
1 year ago
Isolating the endpoint seems like the safest first move to contain the incident and prevent further damage. That's my initial thought, but I'll double-check the other options.
DI
Dierdre
1 year ago
Hmm, I'm a bit unsure about this one. I'll need to make sure I understand the context and the implications of each action before selecting the right response.
JE
Jennifer
1 year ago
This looks like a classic security incident response question. I'll need to carefully review the options and think through the appropriate first step.
AN
Angelo
1 year ago
Hmm, the obvious choice here is C. Isolating the endpoint to contain the security incident. That's the first and most crucial step to take.
LE
Lezlie
1 year ago
Uninstalling the malware is important, but isolating the endpoint can contain the threat immediately.
LO
Lorean
1 year ago
But what about uninstalling the malware? Wouldn't that be more effective?
LU
Luis
1 year ago
I agree with Lezlie, isolating the endpoint can prevent further damage.
LE
Lezlie
1 year ago
I think the first action should be isolating the endpoint.