
 MENU

Refer to the exhibit.
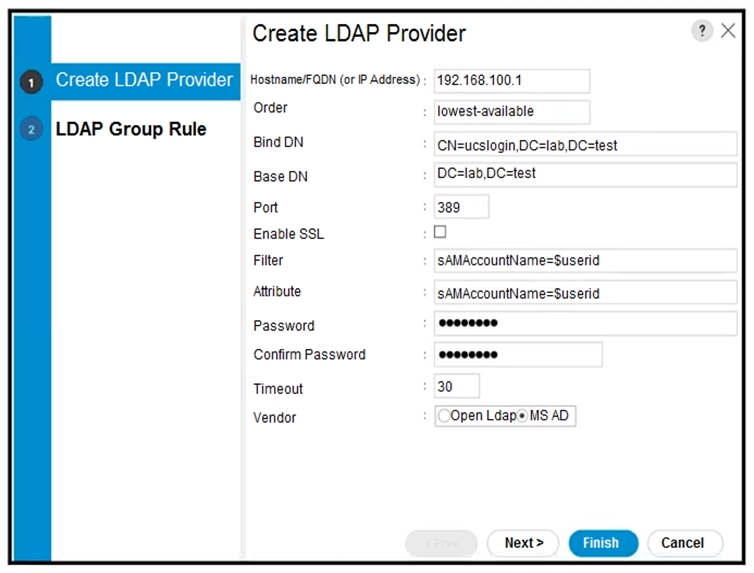
Refer to the exhibit. A network engineer configures an authentication domain through an LDAP provider on the Cisco UCS Manager for users from different companies to log into their respective organizations created in the UCS Manager. The engineer tests the configuration and notices that any user has login access to any organization in the UCS Manager. Which action should be taken to resolve the issue?
Configure the Filter field with sAMAccountName=$company is the appropriate UCS remediation because the symptom maps to a specific managed object rather than a generic server failure. Cisco UCS abstracts hardware through service profiles and policies; therefore, issues involving UCS, UCS Manager, LDAP must be corrected where UCS Manager programs the adapter, boot target, firmware, management certificate, pool qualification, or fabric interconnect state. The selected answer restores that programming path. The other options may appear plausible, but they do not correct the object that UCS uses to derive operational state. For example, boot failures require the correct vHBA/iSCSI target and LUN policy, discovery issues require the proper physical and management path, and firmware failures require the documented recovery action for the failed FSM stage. The correct validation is to inspect the associated fault, confirm inventory acknowledgment, verify the policy under the service profile or equipment tree, and then recheck boot or connectivity behavior after the FSM completes.