Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

Cisco 300-440 Exam - Topic 3 Question 6 Discussion

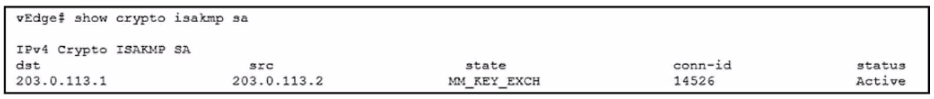
Refer to the exhibit.While troubleshooting an IPsec connection between a Cisco WAN edge router and an Amazon Web Services (AWS) endpoint, a network engineer observes that the security association status is active, but no traffic flows between the devices What is the problem?
B) identity mismatch
A) wrong ISAKMP policy
C) wrong encryption
D) IKE version mismatch

Cisco 300-440 Exam - Topic 3 Question 6 Discussion

Actual exam question for Cisco's 300-440 exam
Question #: 6
Topic #: 3
[All 300-440 Questions]

Refer to the exhibit.

While troubleshooting an IPsec connection between a Cisco WAN edge router and an Amazon Web Services (AWS) endpoint, a network engineer observes that the security association status is active, but no traffic flows between the devices What is the problem?

Show Suggested Answer Hide Answer
Suggested Answer: B

An identity mismatch occurs when the local and remote identities configured on the IPsec peers do not match. This can prevent the establishment of an IPsec tunnel or cause traffic to be dropped by the IPsec policy. In this case, the network engineer should verify that the local and remote identities configured on the Cisco WAN edge router and the AWS endpoint match the values expected by each peer. The identities can be an IP address, a fully qualified domain name (FQDN), or a distinguished name (DN). The identities are exchanged during the IKE phase 1 negotiation and are used to authenticate the peers. If the identities do not match, the peers will reject the IKE proposal and the IPsec tunnel will not be established or will be torn down.Reference:=

Configure IOS-XE Site-to-Site VPN Connection to Amazon Web Services, Topic: Troubleshooting

Designing and Implementing Cloud Connectivity (ENCC) v1.0, Module 3: Implementing Cloud Connectivity, Lesson 2: Implementing Cisco SD-WAN Cloud OnRamp for IaaS, Topic: Troubleshooting Cisco SD-WAN Cloud OnRamp for IaaS

Cisco IOS Security Configuration Guide, Release 15M&T, Chapter: Configuring IPsec Network Security, Topic: Configuring IPsec Identity and Peer Addressing


Contribute your Thoughts:

0/2000 characters
Cristina
9 months ago
Definitely agree with the identity mismatch theory!
upvoted 0 times
...
Alexis
9 months ago
Wrong encryption could also be the culprit here.
upvoted 0 times
...
Lezlie
10 months ago
Surprised that no one mentioned IKE version mismatch!
upvoted 0 times
...
Aretha
10 months ago
I think it's more likely a wrong ISAKMP policy.
upvoted 0 times
...
Mari
10 months ago
Identity mismatch is a common issue in these setups.
upvoted 0 times
...
Jaime
10 months ago
I feel like I read something about IKE version mismatches causing issues, but I’m not entirely confident if that applies here since the SA is active.
upvoted 0 times
...
Vilma
11 months ago
I practiced a similar question about encryption mismatches, but I can't recall if that would keep the SA active without traffic.
upvoted 0 times
...
Santos
11 months ago
I think an identity mismatch could definitely be a reason for the traffic not flowing, especially since both ends need to agree on the identity.
upvoted 0 times
...
Aleta
11 months ago
I remember studying ISAKMP policies, but I'm not sure if a wrong policy would cause the connection to be active but not passing traffic.
upvoted 0 times
...
Ettie
11 months ago
This seems straightforward. Based on the information provided, I'd say the problem is likely an identity mismatch between the Cisco router and the AWS endpoint. That's my best guess for the correct answer.
upvoted 0 times
...
Darrel
11 months ago
I'm a bit confused here. The options seem to cover a range of potential problems, but I'm not sure which one is the most likely culprit. I'll need to think this through step-by-step.
upvoted 0 times
...
Carlota
11 months ago
Okay, let's see. The security association is active, so the connection is established. But no traffic is flowing, so it's likely an issue with the configuration or settings.
upvoted 0 times
...
Flo
11 months ago
Hmm, this looks like a tricky one. I'll need to carefully review the options and think through the possible issues with the IPsec connection.
upvoted 0 times
...
Lili
11 months ago
Alright, I've got a strategy. I'll start by checking the ISAKMP policy to make sure it's configured correctly. If that's not the issue, I'll look into the identity and encryption settings next.
upvoted 0 times
...
Anastacia
11 months ago
This looks like a straightforward question about the required inputs for the Cortex Data Lake sizing calculator. I'm pretty confident I can figure this out.
upvoted 0 times
...
Cathrine
11 months ago
I'm a bit confused on this question. Is the MD5 checksum used to obtain the search warrant, or is it part of the evidence collection process? I'll have to review my notes to make sure I understand this properly.
upvoted 0 times
...
Clement
11 months ago
Ah, I've seen this type of question before. I'm pretty confident I know the right approach, but I'll double-check the options just to be sure.
upvoted 0 times
...
Johanna
11 months ago
I'm feeling confident about this one. The JSON query is checking for the existence of a resource, so the correct tab would be the "Build Your Rule" tab where you can define the rule logic.
upvoted 0 times
...
Marcos
11 months ago
The Scenario feature sounds like the right tool for this. I just need to make sure I set it up properly to switch between the best and worst case budgets.
upvoted 0 times
...
Lenna
2 years ago
Hmm, that's a valid point. But I still think wrong ISAKMP policy is more likely.
upvoted 0 times
...
Allene
2 years ago
I believe it could be an identity mismatch causing the traffic flow issue.
upvoted 0 times
...
Rebecka
2 years ago
I agree with Lenna, a wrong ISAKMP policy could be causing the issue.
upvoted 0 times
...
Lenna
2 years ago
I think the problem might be a wrong ISAKMP policy.
upvoted 0 times
...
Reynalda
2 years ago
Hmm, that's a valid point. But I still think wrong ISAKMP policy is more likely.
upvoted 0 times
...
Alline
2 years ago
I believe it could be an identity mismatch causing the traffic flow issue.
upvoted 0 times
...
Talia
2 years ago
I agree with Reynalda, a wrong ISAKMP policy could be causing the issue.
upvoted 0 times
...
Reynalda
2 years ago
I think the problem might be a wrong ISAKMP policy.
upvoted 0 times
...
Georgeanna
2 years ago
Hmm, the identity mismatch idea sounds plausible too. Maybe the devices are not properly identifying each other, even though the security association is up. I guess we'll have to carefully consider all the options here.
upvoted 0 times
Claribel
2 years ago
I think we should check the IKE version as well. Could be a compatibility issue.
upvoted 0 times
...
Dawne
2 years ago
Yeah, that's a good point. Encryption is crucial for IPsec connections to work properly.
upvoted 0 times
...
Eric
2 years ago
Maybe it's the encryption that's causing the issue. The wrong algorithm or key possibly.
upvoted 0 times
...
Myra
2 years ago
D) IKE version mismatch
upvoted 0 times
...
Anabel
2 years ago
C) wrong encryption
upvoted 0 times
...
Deonna
2 years ago
B) identity mismatch
upvoted 0 times
...
Casie
2 years ago
A) wrong ISAKMP policy
upvoted 0 times
...
...
Jesusita
2 years ago
Personally, I'm leaning towards the wrong encryption option. If the encryption settings are not properly configured, that could definitely cause the connection to be active but not passing any traffic.
upvoted 0 times
...
Lasandra
2 years ago
I agree, Shawnta. It's a bit puzzling. My initial thought is that it could be an identity mismatch, but I'm not entirely certain. What do you guys think?
upvoted 0 times
...
Shawnta
2 years ago
Hmm, this question seems tricky. I'm not sure if I fully understand the issue here. The fact that the security association is active but no traffic is flowing seems like a bit of a paradox.
upvoted 0 times
...

Save Cancel