
 MENU

Refer to the exhibit.
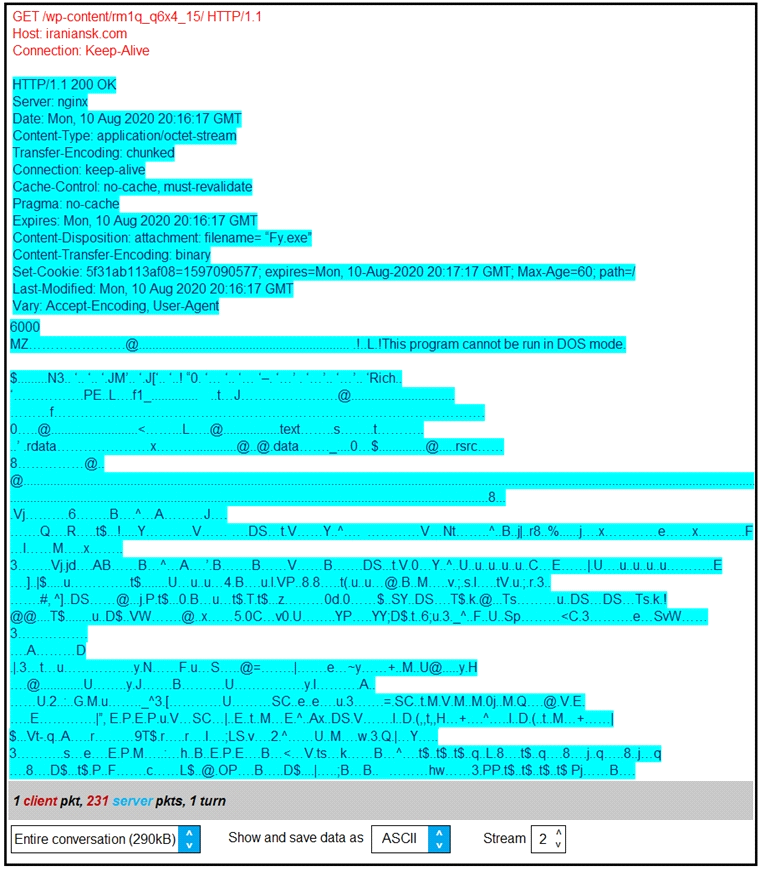
According to the Wireshark output, what are two indicators of compromise for detecting an Emotet malware download? (Choose two.)
Suggested Answer: C, E
Get Premium 300-215 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
10 comments · newest first
QU
Quentin
11 months ago
Wait, people still download stuff from unknown domains? Really?
DE
Delisa
12 months ago
Not sure about the nginx server being a problem.
LO
Loreta
12 months ago
Hash value 5f31ab113af08? Sounds like a red flag.
LO
Lorrie
1 year ago
I think Fy.exe is a clear indicator too.
KA
Kattie
1 year ago
Domain name iraniansk.com is definitely suspicious.
JO
Joanne
1 year ago
I think "E" is a strong candidate too, as application/octet-stream is a common content type for malicious files.
AS
Ashlyn
1 year ago
I'm not entirely sure, but I feel like "D" could be relevant since executable files are often associated with malware downloads.
GL
Glenn
1 year ago
I remember discussing how domain names can be a key indicator of malware, so I think "A" might be one of the answers.
PA
Patria
1 year ago
I practiced a similar question, and I feel like "C" could be a trick option since hash values are often used to identify malware, but I'm not completely confident.
CA
Casandra
1 year ago
Hmm, I'm not entirely sure about this one. I'll need to review my notes on Citrix SBC/HVD tuning to make sure I understand the best approach.