
 MENU

Refer to the exhibit.
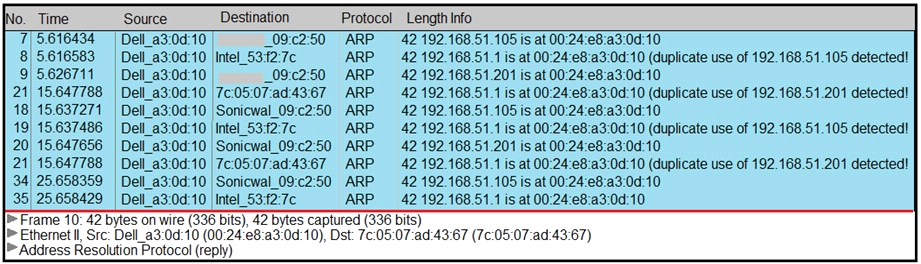
A security analyst notices unusual connections while monitoring traffic. What is the attack vector, and which action should be taken to prevent this type of event?
Suggested Answer: C
Get Premium 300-215 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
10 comments · newest first
RO
Rory
12 months ago
I agree with ARP spoofing, but I'm surprised it's not more widely recognized!
OS
Osvaldo
12 months ago
Wait, MAC flooding? That seems a bit off for unusual connections.
AN
Antonio
1 year ago
Definitely SYN flooding. Blocking those packets is a must!
AS
Ashlyn
1 year ago
I think it's more about DNS spoofing. Encrypting protocols helps too.
JE
Jerry
1 year ago
Looks like a classic case of ARP spoofing. Port security is key!
MI
Micheal
1 year ago
I think the Process Builder could be a good option for this scenario. It would allow me to create a single process with multiple decisions and actions.
HE
Hermila
1 year ago
Considering the phrases used in the options, I feel like A and B might be confused. They both mention interest cost increases but in different contexts. I should probably double-check what refunding means again.
BR
Brande
1 year ago
Hmm, I'm not sure. The question mentions improving KPIs, so the Top Articles sorted descending might be more relevant.
IS
Isabella
1 year ago
I'm a little confused by this question. Does the SAP HANA Cockpit or SAP Solution Manager have any relevance here? I'll need to review my notes to make sure I understand the differences between these tools and how they relate to the migration scenario.
BR
Brandee
1 year ago
This looks like a tricky one. I'll need to think carefully about the test basis and how it relates to the different metrics.