Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

Cisco 300-215 Exam - Topic 6 Question 119 Discussion

Posted by Rodrigo on Sep 27, 2026 at 01:15 AM

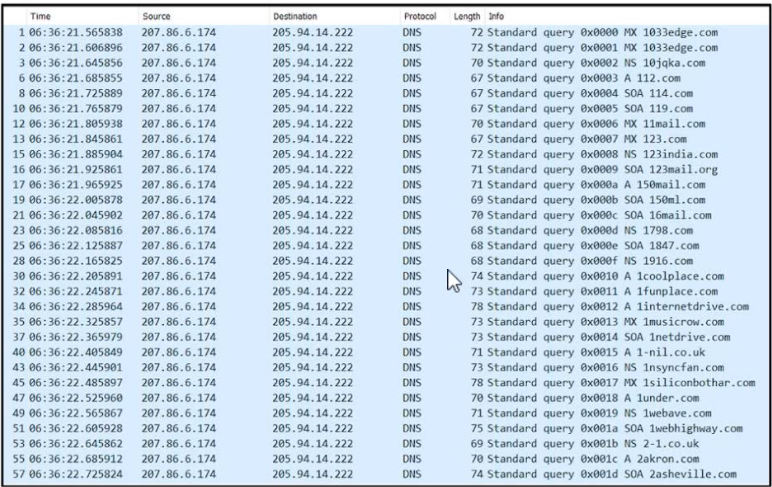
Refer to the exhibit.

According to the Wireshark output, what is the Indicator of Attack?

Suggested Answer: D

The capture shows one source, 207.86.6.174, sending a rapid sequence of DNS queries to 205.94.14.222. The timestamps progress by roughly 0.04 seconds, producing dozens of requests in little more than one second. That unusually high request rate is the observable Indicator of Attack; the exhibit does not establish that the queried domains are malicious. Requesting several DNS record types can occur legitimately, so option B is descriptive but not the strongest attack indicator. Option A ignores the abnormal frequency. CBRFIR Forensics Processes objective 4.3 requires analysts to examine traffic associated with malicious activity using network-monitoring tools and Wireshark display analysis. The defensible conclusion must therefore remain tied to what the packet evidence directly proves: a DNS-query burst from a single host, which warrants correlation with baseline, endpoint, and threat-intelligence data. Cisco CBRFIR v1.2 exam topics

================


Get Premium 300-215 Questions as Interactive Web-Based Practice Test or PDF Real Exam Format Detailed Explanations Instant Access Get Your Practice Test
5 comments · newest first
JE
Jerilyn 5 days ago
Looks like option D is the real red flag here.
KR
Kris 10 days ago
I lean towards option D since it seems to fit the pattern of DNS amplification attacks we studied, but I’m still a bit uncertain about the specifics.
CE
Celeste 15 days ago
I feel like option B could also be suspicious, but I can't recall if just requesting different records is enough to classify it as an attack.
PE
Pearly 20 days ago
I think we had a practice question similar to this, and it pointed out that requesting records for known malicious domains is a clear sign of an attack.
GL
Glennis 26 days ago
I remember we discussed how multiple DNS requests in a short time can indicate a potential attack, but I'm not sure if that's the only factor here.
0/2000 characters

Save Cancel