
Free Preparation Discussions
 MENU

Cisco 300-215 Exam - Topic 6 Question 102 Discussion
Topic #: 6
Refer to the exhibit.
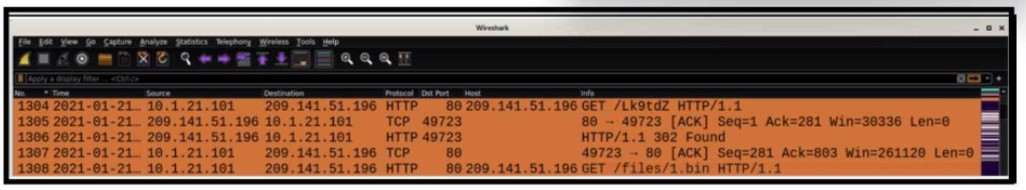
What is occurring within the exhibit?
The Wireshark capture shows a series of HTTP requests and responses:
The client (10.1.21.101) sends a GET request for /Lk9tdZ.
The server (209.141.51.196) responds with HTTP/1.1 302 Found, which is a standard HTTP status code indicating a redirection.
The subsequent GET request from the client is for /files/1.bin, which indicates it followed the redirect.
This behavior confirms that the server is issuing an HTTP 302 redirect from the initial request path /Lk9tdZ to /files/1.bin. This is often observed in malware command-and-control behavior or file download staging.
Option A is incorrect: 302 is a status code, not a data size.
Option C is incorrect: port 49723 is a source/destination ephemeral port, not a redirect target.
Option D is incorrect: communication is over HTTP, not HTTPS (which would indicate encryption).
Herman
9 months agoEdelmira
9 months agoYasuko
9 months agoMary
9 months agoKip
9 months agoRosita
10 months agoKeena
10 months agoMel
10 months agoMary
10 months agoAllene
11 months agoLillian
11 months agoElli
11 months agoTrinidad
11 months agoRickie
11 months agoHayley
11 months agoAlesia
1 year agoWinfred
1 year agoArlyne
1 year ago