
 MENU

Refer to the exhibit.
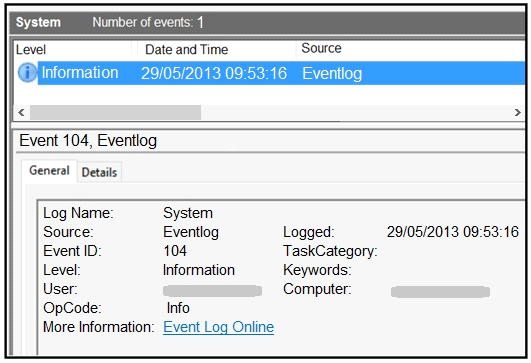
An employee notices unexpected changes and setting modifications on their workstation and creates an incident ticket. A support specialist checks processes and services but does not identify anything suspicious. The ticket was escalated to an analyst who reviewed this event log and also discovered that the workstation had multiple large data dumps on network shares. What should be determined from this information?
Suggested Answer: B
Get Premium 300-215 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
9 comments · newest first
RO
Roxane
12 months ago
I agree, the data dumps are a red flag for sure!
CA
Cassie
12 months ago
Wait, are we sure it’s not just a misconfiguration?
GR
Gretchen
1 year ago
I think it's more likely log tampering.
MA
Major
1 year ago
Definitely suspicious with those large data dumps!
CH
Christoper
1 year ago
Sounds like a reconnaissance attack to me.
KR
Kristal
1 year ago
I'm feeling pretty confident about this one. Encryption and digital signatures are the clear data-oriented options here. The other two are more about managing user access, not directly protecting the data.
SA
Samira
1 year ago
I feel pretty confident about this one. The answer is clearly C - adding disclaimers to advertising materials is the best way to avoid liability under ostensible agency.
AD
Adelina
1 year ago
This seems similar to a practice question we did in class. I think it might not compile due to a missing underscore in _v.
HA
Halina
1 year ago
HTTP is the clear winner here. As the primary protocol for the web, it's the go-to choice for the vast majority of web servers. I'd be surprised if any other protocol even comes close in terms of usage.