Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Welcome to Pass4Success

- Free Preparation Discussions

Cisco 200-201 Exam - Topic 6 Question 80 Discussion

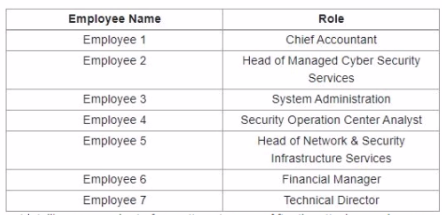
Refer to the exhibit.A suspicious IP address is tagged by Threat Intelligence as a brute-force attempt source After the attacker produces many of failed login entries, it successfully compromises the account. Which stakeholder is responsible for the incident response detection step?
C) employee 4
A) employee 5
B) employee 3
D) employee 2

Cisco 200-201 Exam - Topic 6 Question 80 Discussion

Actual exam question for Cisco's 200-201 exam
Question #: 80
Topic #: 6
[All 200-201 Questions]

Refer to the exhibit.

A suspicious IP address is tagged by Threat Intelligence as a brute-force attempt source After the attacker produces many of failed login entries, it successfully compromises the account. Which stakeholder is responsible for the incident response detection step?

Show Suggested Answer Hide Answer
Suggested Answer: C

Contribute your Thoughts:

0/2000 characters
Lonna
9 months ago
I agree, employee 4 seems like the right choice for this situation.
upvoted 0 times
...
Nettie
9 months ago
Wait, how did the attacker get in after so many failed attempts? Sounds fishy.
upvoted 0 times
...
Terry
10 months ago
Employee 3 is usually the one monitoring those logs, right?
upvoted 0 times
...
Emelda
10 months ago
Not so sure about that, I feel like employee 2 would be more involved.
upvoted 0 times
...
Benedict
10 months ago
I think it's definitely employee 4 who handles incident response.
upvoted 0 times
...
Gail
10 months ago
I’m a bit confused about the responsibilities. I thought all employees had some role, but I guess it depends on their specific duties.
upvoted 0 times
...
Stefanie
11 months ago
I feel like employee 2 had a key role in our last case study about account compromises. Could that be the right choice here?
upvoted 0 times
...
Shelia
11 months ago
This reminds me of a practice question where we had to identify roles in incident response. I think it might be employee 4, but I’m not completely confident.
upvoted 0 times
...
Evangelina
11 months ago
I remember we discussed how the incident response team is usually the one responsible for detection, but I’m not sure which employee that would be.
upvoted 0 times
...
Haydee
11 months ago
I'm a little confused by the wording of the question. Let me re-read it a few times and see if I can break down the key details to figure out the answer.
upvoted 0 times
...
Rozella
11 months ago
This looks like a classic security incident scenario. I'm confident I can apply my knowledge of incident response procedures to identify the correct stakeholder for the detection step.
upvoted 0 times
...
Hollis
11 months ago
Okay, I think I've got a handle on this. The question is asking about the incident response detection step, so I'll focus on that and try to determine which stakeholder is responsible.
upvoted 0 times
...
Carmela
11 months ago
Hmm, I'm a bit unsure about this one. I'll need to carefully review the information provided and think through the different stakeholder responsibilities.
upvoted 0 times
...
Pearly
11 months ago
This question seems straightforward, but I want to make sure I understand the details before answering. The key seems to be identifying the stakeholder responsible for the incident response detection step.
upvoted 0 times
...
Cheryl
11 months ago
I'm a bit confused on this one. I know CBA is related to the UI, but I'm not sure how it specifically applies to SAP Master Data Governance. Gotta read the question more carefully.
upvoted 0 times
...
Remona
11 months ago
Hmm, this seems straightforward. I'll carefully read through the options and think about where installation logs are typically stored.
upvoted 0 times
...
Dianne
11 months ago
Hmm, I'm a bit confused by this one. I know the prof_attr file is used to define profiles, but I'm not sure how the other files mentioned are related. I'll need to review my notes on user and profile management to figure this out.
upvoted 0 times
...
Delmy
2 years ago
Employee 4 could have a role too, but based on the exhibit, I still think employee 3 is more likely.
upvoted 0 times
...
Nana
2 years ago
But what about employee 4? Couldn't they also be responsible for detecting the brute-force attempt?
upvoted 0 times
...
Belen
2 years ago
I agree with Delmy, employee 3 seems like the one who should have detected the suspicious activity.
upvoted 0 times
...
Delmy
2 years ago
I think employee 3 is responsible for the incident response detection step.
upvoted 0 times
...
Carey
2 years ago
Ooh, security team, huh? I bet they're just sitting back and eating donuts while the rest of us sweat over these questions. Lucky them!
upvoted 0 times
Vilma
2 years ago
Ooh, security team, huh? I bet they're just sitting back and eating donuts while the rest of us sweat over these questions. Lucky them!
upvoted 0 times
...
Rhea
2 years ago
Correct! Employee 3 is responsible for the incident response detection step.
upvoted 0 times
...
Melvin
2 years ago
B) employee 3
upvoted 0 times
...
...
Velda
2 years ago
Hmm, let me take a look at the exhibit again. Okay, so we have a suspicious IP address and a successful compromise of an account. I'm thinking it's gotta be the security team, so maybe employee 4?
upvoted 0 times
...
Colette
2 years ago
Yeah, I agree. This whole scenario with the brute-force attack and compromised account is giving me a headache. I'm going to have to really think this one through.
upvoted 0 times
...
Mozell
2 years ago
Amen to that! I just hope I can keep my wits about me and pick the right answer. Fingers crossed!
upvoted 0 times
...

Save Cancel