
 MENU

Refer to the exhibit.
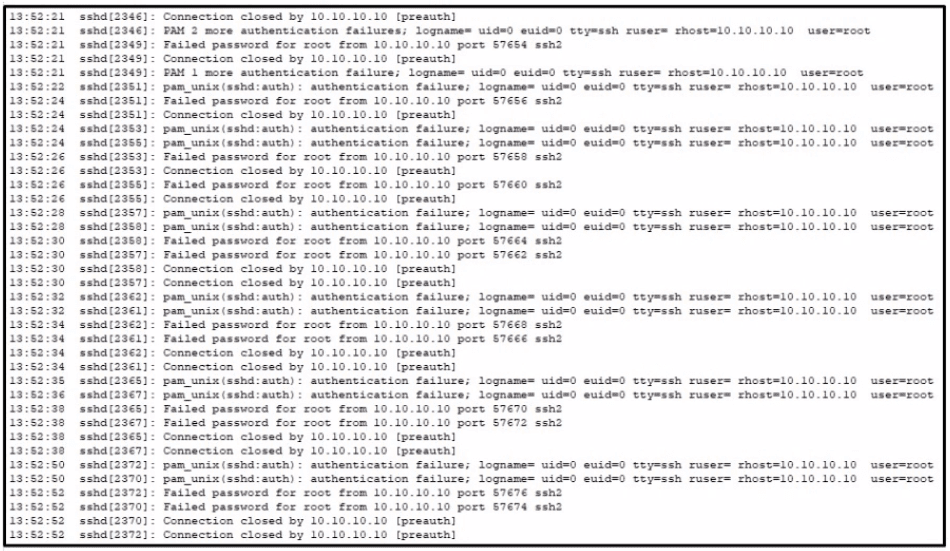
Refer to the exhibit A SOC analyst is examining the Auth.log file logs of one the breached systems What is the possible reason for this event log?
Suggested Answer: B
Get Premium 200-201 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
23 comments · newest first
LA
Lavera
2 days ago
A DoS attack seems less likely here.
BU
Bulah
7 days ago
I lean towards B, a brute force on Windows.
SI
Sina
12 days ago
I doubt it, looks suspicious to me.
NI
Nickie
17 days ago
But what if 10.10.10.10 is a legit host?
LE
Lewis
22 days ago
Yeah, option D makes sense.
AU
Audry
27 days ago
I think it's a brute force attack.
YO
Yoko
1 month ago
Exactly, that's classic brute force behavior.
LE
Levi
1 month ago
True, the logs suggest repeated failed attempts.
SH
Shawnna
1 month ago
A DoS attack seems less likely here.
LY
Lynette
2 months ago
I lean towards B, a brute force on Windows.
DI
Dion
2 months ago
I doubt it, looks suspicious to me.
TI
Tiffiny
2 months ago
But what if 10.10.10.10 is a legit host?
YO
Yoko
2 months ago
Yeah, option D makes sense.
LE
Levi
2 months ago
I think it's a brute force attack.
AL
Alaine
2 months ago
Really? I'm not so sure about that.
FL
Florencia
3 months ago
No way, it's clearly a DoS attack!
CI
Ciara
3 months ago
I think it's just a regular log, 10.10.10.10 seems fine.
LE
Leatha
3 months ago
Definitely a password cracking attempt.
LE
Leota
3 months ago
Looks like a brute force attack from 10.10.10.10.
AL
Alpha
3 months ago
I keep mixing up the definitions of DoS and brute force attacks. I think I need to focus more on those details before the exam.
AI
Aide
3 months ago
I feel like I might have seen something about legitimate hosts in the logs, so maybe C is a possibility too?
DE
Devora
4 months ago
This seems similar to a practice question we did on identifying attack types from logs. I think option D makes sense, but I could be wrong.
DI
Dierdre
4 months ago
I remember studying about log analysis, but I'm not sure if the IP indicates a brute force attack or just a regular login attempt.