
Free Preparation Discussions
 MENU

Splunk SPLK-1005 Exam Questions
- Topic 1: Splunk Cloud Overview: In this topic, aspiring Splunk Cloud administrators cover cloud topology. Moreover, the topic focuses on the differences between Splunk Cloud and Splunk Enterprise.
- Topic 2: Index Management: Splunk Cloud administrators get knowledge about Splunk index, indexes in the cloud and data from an index, and monitoring indexing activities.
- Topic 3: User Authentication and Authorization: Splunk Cloud administrators learn how to administer Splunk user roles and integrate Splunk with LDAP.
- Topic 4: Splunk Configuration Files: In this SPLK-1005 exam topic, the Splunk Cloud administrator learns about Splunk configuration files and directories. Moreover, this topic addresses the configuration of file precedence.
- Topic 5: Getting Data in Cloud: Aspiring Splunk Cloud administrators cover Splunk forwarder types, configuration of a forwarder to Splunk Cloud and the role of forwarders.
- Topic 6: Forwarder Management: The SPLK-1005 exam covers Splunk Deployment Server in this topic. Also, the topic teaches Splunk Cloud administrator about forwarder management configuration of forwarders to be deployment clients.
- Topic 7: Monitor Inputs: The topic tests knowledge of Splunk Cloud administrator about Splunk process for creating file and inputting data.
- Topic 8: Network and Other Inputs: The SPLK-1005 exam covers creation of network (TCP and UDP) inputs. Aspiring Splunk Cloud administrators also learn about creating a basic scripted input in this topic.
- Topic 9: Fine-tuning Inputs: The topic assesses the knowledge of Cloud administrators about processing that occurs during the input phase. It also covers the configuration of input phase options, including source type fine-tuning and character set encoding.
- Topic 10: Parsing Phase and Data Preview: The SPLK-1005 exam topic gives Splunk Cloud administrators knowledge about the default processing that occurs during parsing. It also includes sub-topics about optimization and configuration of event line breaking.
- Topic 11: Manipulating Raw Data: The topic gives Cloud administrators knowledge on how data Transformations are defined and invoked. It also covers the usage of transformations with props.conf and transforms.conf for the modification of raw data.
- Topic 12: Installing and Managing Apps: Splunk Cloud administrators get knowledge about reviewing the process for installing apps. Moreover, the topic focuses on private apps and how apps are managed.
- Topic 13: Working with Splunk Cloud Support: Splunk Cloud administrators attempting the SPLK-1005 exam learn about isolating problems before contacting Splunk Cloud Support. Furthermore, the topic defines the process for working with Splunk Cloud Support.
Free Splunk SPLK-1005 Exam Actual Questions
Note: Premium Questions for SPLK-1005 were last updated On Oct. 17, 2026 (see below)
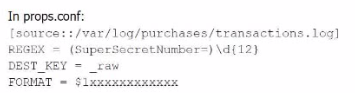
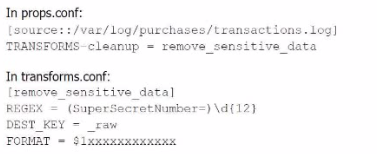
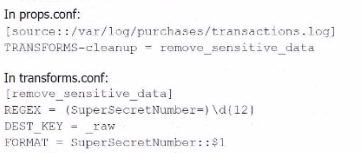
A user has been asked to mask some sensitive data without tampering with the structure of the file /var/log/purchase/transactions. log that has the following format:

A)
B)
C)
D)
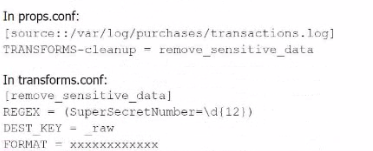
Option B is the correct approach because it properly uses a TRANSFORMS stanza in props.conf to reference the transforms.conf for removing sensitive data. The transforms stanza in transforms.conf uses a regular expression (REGEX) to locate the sensitive data (in this case, the SuperSecretNumber) and replaces it with a masked version using the FORMAT directive.
In detail:
props.conf refers to the transforms.conf stanza remove_sensitive_data by setting TRANSFORMS-cleanup = remove_sensitive_data.
transforms.conf defines the regular expression that matches the sensitive data and specifies how the sensitive data should be replaced in the FORMAT directive.
This approach ensures that sensitive information is masked before indexing without altering the structure of the log files.
Splunk Cloud Reference: For further reference, you can look at Splunk's documentation regarding data masking and transformation through props.conf and transforms.conf.
Source:
Splunk Docs: Anonymize data
Splunk Docs: Props.conf and Transforms.conf
Consider the following configurations:
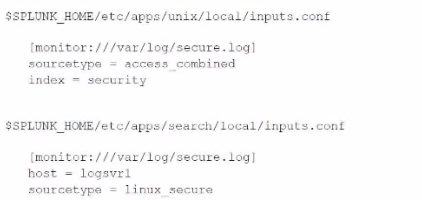
What is the value of the sourcetype property for this stanza based on Splunk's configuration file precedence?
When there are conflicting configurations in Splunk, the platform resolves them based on the configuration file precedence rules. These rules dictate which settings are applied based on the hierarchy of the configuration files.
In the provided configurations:
The first configuration in $SPLUNK_HOME/etc/apps/unix/local/inputs.conf sets the sourcetype to access_combined.
The second configuration in $SPLUNK_HOME/etc/apps/search/local/inputs.conf sets the sourcetype to linux_secure.
Configuration File Precedence:
In Splunk, configurations in local directories take precedence over those in default.
If two configurations are in local directories of different apps, the alphabetical order of the app names determines the precedence.
Since 'search' comes after 'unix' alphabetically, the configuration in $SPLUNK_HOME/etc/apps/search/local/inputs.conf will take precedence.
Therefore, the value of the sourcetype property for this stanza is linux_secure.
Splunk Documentation Reference:
Configuration File Precedence
Resolving Conflicts in Splunk Configurations
This confirms that the correct answer is C. linux_secure.
In case of a Change Request, which of the following should submit a support case for Splunk Support?
In Splunk Cloud, when there is a need for a change request that might involve modifying settings, upgrading, or other actions requiring Splunk Support, the process typically requires submitting a support case.
D . Any person with the appropriate entitlement: This is the correct answer. Any individual who has the necessary permissions or entitlements within the Splunk environment can submit a support case. This includes administrators or users who have been granted the ability to engage with Splunk Support. The request does not necessarily have to come from a Certified Splunk Cloud Administrator or the infrastructure owner; rather, it can be submitted by anyone with the correct level of access.
Splunk Documentation Reference:
Submitting a Splunk Support Case
Managing User Roles and Entitlements
Which of the following lists all parameters supported by the acceptFrom argument?
The acceptFrom parameter is used in Splunk to specify which IP addresses or DNS names are allowed to send data to a Splunk instance. The supported formats include IPv4, IPv6, CIDR notation, and DNS names.
B . IPv4, IPv6, CIDRs, DNS names is the correct answer. These are the valid formats that can be used with the acceptFrom argument. Wildcards are not supported in acceptFrom parameters for security reasons, as they would allow overly broad access.
Splunk Documentation Reference:
acceptFrom Parameter Usage
A customer has worked with their LDAP administrator to configure an LDAP strategy in Splunk. The configuration works, and user Mia can log into Splunk using her LDAP Account. After some time, the Splunk Cloud administrator needs to move Mia from the user role to the power role. How should they accomplish this?
In Splunk Cloud, role-based access controls are managed by mapping LDAP groups to Splunk roles. Therefore, any change in roles should be managed by the LDAP administrator, who can adjust Mia's group to an LDAP group mapped to the power role. [Reference: Splunk Docs on LDAP integration in Splunk Cloud]
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Ashley Mitchell
25 days agoAshley Edwards
2 months agoCharles Carter
2 months agoAdam Rogers
3 months agoAdam Davis
3 months agoRobert Green
4 months agoDorothy Garcia
4 months agoDaniel Nelson
5 months agoEric Torres
5 months agoRichard Thompson
5 months agoMaria Rodriguez
5 months agoTimothy Davis
5 months agoDonald Taylor
5 months agoGeorge Howard
5 months agoWilliam White
6 months agoMichelle Anderson
6 months agoTony
7 months agoMartina
7 months agoPenney
7 months agoBo
8 months agoKristeen
8 months agoProvidencia
8 months agoKip
8 months agoLashawnda
9 months agoDemetra
9 months agoMammie
9 months agoDana
9 months agoArlette
10 months agoNana
10 months agoLinwood
10 months agoValda
10 months agoMari
11 months agoJeanice
11 months agoPete
11 months agoElise
11 months agoDetra
12 months agoReiko
1 year agoBeatriz
1 year agoMaia
1 year agoShawnda
1 year agoColton
1 year agoMaryann
1 year agoNelida
1 year agoPaulina
1 year agoSamira
1 year agoElliott
1 year agoAlbina
1 year agoErnie
2 years agoBrynn
2 years agoJeannine
2 years agoTonette
2 years agoArlene
2 years agoShonda
2 years agoJade
2 years agoTeresita
2 years agoLeandro
2 years agoNaomi
2 years agoLou
2 years agoKayleigh
2 years agoNoah
2 years agoDalene
2 years agoTrina
2 years agoShawn
2 years agoPok
2 years ago