Free Preparation Discussions
 MENU

Free Salesforce Certified Platform Identity and Access Management Architect (Plat-Arch-203) Exam Dumps October 2026
Here you can find all the free questions related with Salesforce Certified Platform Identity and Access Management Architect (Salesforce Certified Platform Identity and Access Management Architect (Plat-Arch-203)) exam. You can also find on this page links to recently updated premium files with which you can practice for actual Salesforce Certified Platform Identity and Access Management Architect Exam. These premium versions are provided as Salesforce Certified Platform Identity and Access Management Architect (Plat-Arch-203) exam practice tests, both as desktop software and browser based application, you can use whatever suits your style. Feel free to try the Salesforce Certified Platform Identity and Access Management Architect Exam premium files for free, Good luck with your Salesforce Certified Platform Identity and Access Management Architect Exam.Universal containers(UC) has decided to build a new, highly sensitive application on Force.com platform. The security team at UC has decided that they want users to provide a fingerprint in addition to username/Password to authenticate to this application. How can an architect support fingerprints as a form of identification for salesforce Authentication?
MultipleChoice
Universal Containers (UC) has a strict requirement to authenticate users to Salesforce using their mainframe credentials. The mainframe user store cannot be accessed from a SAML provider. UC would also like to have users in Salesforce created on the fly if they provide accurate mainframe credentials.
How can the Architect meet these requirements?
OptionsMultipleChoice
Universal containers wants to implement single Sign-on for a salesforce org using an external identity provider and corporate identity store. What type of Authentication flow is required to support deep linking?
OptionsMultipleChoice
Universal Containers (UC) uses a home-grown Employee portal for their employees to collaborate. UC decides to use Salesforce Ideas to allow employees to post Ideas from the Employee portal. When users click on some of the links in the Employee portal, the users should be redirected to Salesforce, authenticated, and presented with the relevant pages. What OAuth flow is best suited for this scenario?
OptionsMultipleChoice
Universal Containers (UC) has an e-commerce website where customers can buy products, make payments and manage their accounts. UC decides to build a Customer Community on Salesforce and wants to allow the customers to access the community from their accounts without logging in again. UC decides to implement an SP-initiated SSO using a SAML-compliant Idp. In this scenario where Salesforce is the Service Provider, which two activities must be performed in Salesforce to make SP-initiated SSO work? Choose 2 answers
OptionsMultipleChoice
An architect has successfully configured SAML-BASED SSO for universal containers. SSO has been working for 3 months when Universal containers manually adds a batch of new users to salesforce. The new users receive an error from salesforce when trying to use SSO. Existing users are still able to successfully use SSO to access salesforce. What is the probable cause of this behaviour?
OptionsMultipleChoice
Northern Trail Outfitters (NTO) wants to give customers the ability to submit and manage issues with their purchases. It is important for to give its customers the ability to login with their Facebook and Twitter credentials.
Which two actions should an identity architect recommend to meet these requirements?
Select 2 answers
OptionsMultipleChoice
Universal containers wants to implement single Sign-on for a salesforce org using an external identity provider and corporate identity store. What type of Authentication flow is required to support deep linking?
OptionsMultipleChoice
Refer to the exhibit.
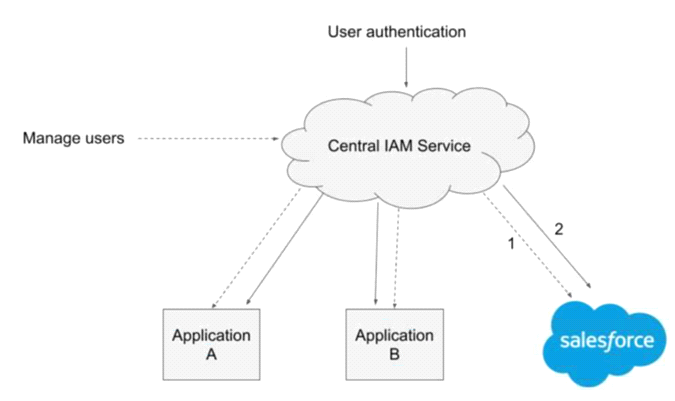
An organization has a central cloud-based Identity and Access Management (IAM) Service for authentication and user management, which must be utilized by all applications as follows:
1 - Change of a user status in the central IAM Service triggers provisioning or deprovisioining in the integrated cloud applications.
2 - Security Assertion Markup Language single sign-on (SSO) is used to facilitate access for users authenticated at identity provider (Central IAM Service).
Which approach should an IAM architect implement on Salesforce Sales Cloud to meet the requirements?
OptionsMultipleChoice
Refer to the exhibit.
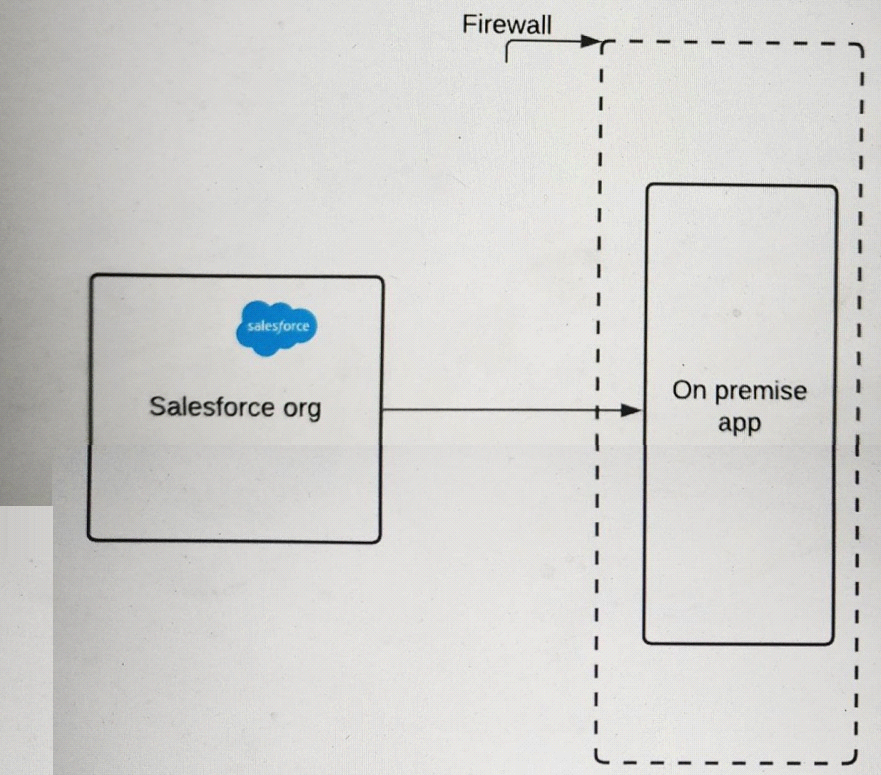
A pharmaceutical company has an on-premise application (see illustration) that it wants to integrate with Salesforce.
The IT director wants to ensure that requests must include a certificate with a trusted certificate chain to access the company's on-premise application endpoint.
What should an Identity architect do to meet this requirement?
Options