
 MENU

There are three logging categories: category1, category1.eu, and category1.us.
In Business Manager, category1 is enabled for WARN level and no other categories are configured. All custom log targets are enabled.
The code segment below executes.
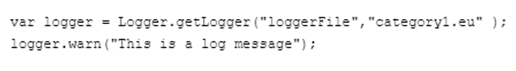
What is the result'
Suggested Answer: C
Get Premium Salesforce Certified B2C Commerce Architect (Arch-303) Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
11 comments · newest first
HA
Harley
12 months ago
Wait, are you all sure about that? Sounds off to me.
KR
Krissy
12 months ago
Definitely going with custom-loggerFile for this one!
ET
Ettie
12 months ago
Not sure about that, seems like it should just be loggerFile.
IS
Isabelle
1 year ago
I think logs will be written with the custom prefix.
KA
Kate
1 year ago
Category1 is set to WARN level only.
RI
Ricki
1 year ago
I'm a bit confused about the custom log targets. Does enabling them mean logs will definitely be written?
AN
Antione
1 year ago
I think I practiced a similar question where the log prefix was important. I feel like it might be "loggerFile" in this case.
JO
Joni
1 year ago
I remember that category1 is set to WARN level, but I'm not sure if that affects the other categories.
ST
Stephaine
1 year ago
I recall that if the log level is WARN, then only WARN messages should be logged. So, maybe "customwarn" is the right prefix?
MA
Marg
1 year ago
Okay, I think I've got this. Based on the question, the answer has to be the state where reviewers can take those two actions - send it back to draft or forward it for approval. That sounds like the "Review" state to me, so I'm going with option D.
LE
Leah
1 year ago
This looks like a straightforward question about the key elements of SecOps. I'll start by identifying the ones I'm sure about, like people, processes, and technology, and then try to reason through the other two.