
 MENU

Click the exhibit button below.
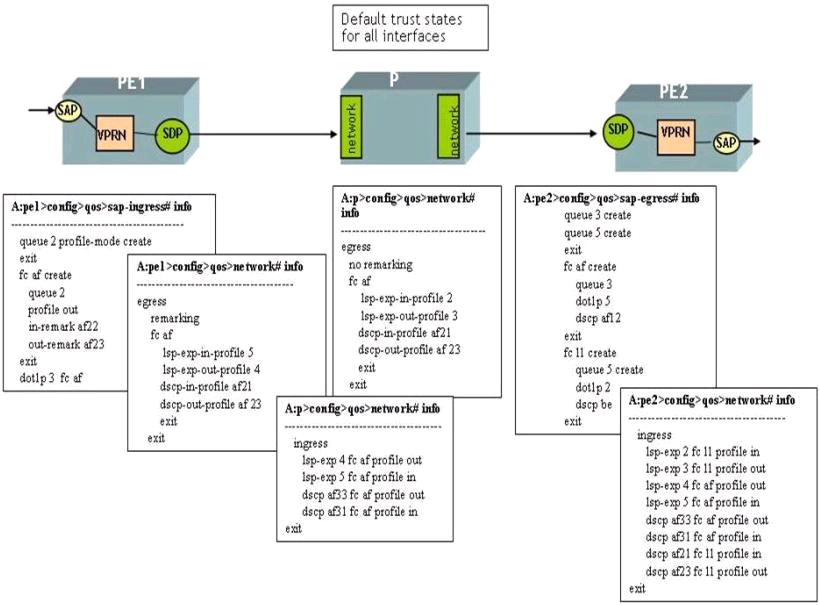
All interfaces are using their default trust states and MPLS is used as the transport tunnel. The SAP-ingress, SAP-egress, and network QoS policies have been configured as shown below. Assume that the default network-queue policy is used on each router.
At router PE 1, customer traffic is arriving marked with DSCP BE and tagged with a dot1p value of 3.
Based on the configuration shown below for the VPRN service, what will be the DSCP and dot1p marking for the packet egressing at router PE 2? (Choose two)
Suggested Answer: D, E
Get Premium 4A0-C02 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
12 comments · newest first
MO
Mona
11 months ago
The dot1p value should stay at 3, right?
KI
Kimberely
12 months ago
I'm pretty sure the dot1p value will be set to 5.
LY
Lyla
12 months ago
Wait, how can it be af21? I thought it was be.
JA
Jamey
1 year ago
Totally agree with that!
MA
Marjory
1 year ago
The DSCP value will be set to af21.
BO
Bok
1 year ago
Based on what I studied, I feel like the DSCP should be af23, but I’m not confident about the dot1p value.
RA
Raelene
1 year ago
I’m a bit confused about the DSCP marking; I thought it would be set to be, but I need to double-check the mapping rules.
KA
Kanisha
1 year ago
I remember practicing a similar question where the dot1p value was affected by the ingress marking. I think the dot1p value will stay at 3.
RO
Robt
1 year ago
I think the DSCP value might be set to af21, but I'm not entirely sure how the QoS policies interact with the default settings.
RA
Rana
1 year ago
Okay, let me think this through. The question is asking about the types of sensitive personal data under the IT Act, so I'll need to focus on the legal definitions and categories specified in the law.
RO
Rodolfo
1 year ago
This is a tricky one, but I think maintaining customer-managed keys and revoking them is the way to go. That way, the data is truly inaccessible.
AD
Adaline
1 year ago
This seems like a straightforward question about the types of background information auditors should review. I'm pretty confident I can handle this one.