
Free Preparation Discussions
 MENU

NetApp NS0-304 Exam Questions
- Topic 1: Hybrid Cloud Concepts: This section covers fundamental knowledge of hybrid cloud, including networking aspects, various consumption models, and the overall hybrid cloud environment.
- Topic 2: Configuration: This exam designed for IT professionals in this domain focuses on practical skills in provisioning and placing resources, as well as data migration techniques in a hybrid cloud setup.
- Topic 3: Automate: The automation section tests the knowledge of hybrid cloud professionals to address common workflows and the use of system templates to streamline operations in hybrid cloud environments.
- Topic 4: Secure and Protect: This critical domain covers various security aspects, including Identity and Access Management (IAM) policies, access permissions, compliance requirements, security policies, and data protection solutions specific to hybrid cloud environments.
- Topic 5: Monitor and Troubleshoot: The final domain deals with essential operational skills, including setting up monitoring, alerting, and reporting systems for hybrid cloud infrastructures, as well as troubleshooting techniques.
Free NetApp NS0-304 Exam Actual Questions
Note: Premium Questions for NS0-304 were last updated On Oct. 15, 2026 (see below)
Refer to the exhibit.
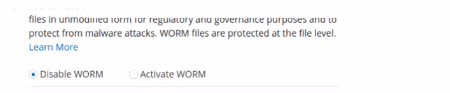
An administrator is deploying the latest version of CVO via BlueXP. What will be the result of leaving the option disabled?
In the context of deploying Cloud Volumes ONTAP (CVO) via BlueXP, if the administrator chooses to leave the WORM (Write Once Read Many) option disabled, the default behavior for newly created volumes will be as non-SnapLock volumes. Here's what this implies:
Non-SnapLock Volumes: Leaving the WORM feature disabled means that new volumes will not be created with the SnapLock compliance feature activated. SnapLock is used to ensure data immutability for compliance and regulatory purposes, protecting files from being altered or deleted before a predetermined retention period expires.
Volume Configuration Flexibility: Administrators will have the option to activate SnapLock or other data protection features on a per-volume basis in the future if needed, but this would need to be explicitly configured.
Impact on Data Management: This choice affects how data is managed in terms of compliance and security. Without SnapLock enabled by default, the volumes will operate under standard data management policies, which do not include immutability protections.
For more information on the implications of enabling or disabling SnapLock and how it affects volume creation in Cloud Volumes ONTAP, please refer to the NetApp BlueXP and SnapLock documentation: NetApp SnapLock Documentation.
An administrator configures the trident ontap-san driver and specifies useCHAP=true.
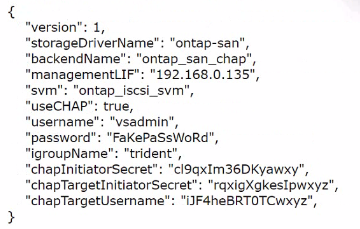
Which parameter is missing from the configuration?
When configuring the Trident ONTAP-SAN driver with CHAP (Challenge Handshake Authentication Protocol) enabled (useCHAP: true), it is essential to specify both the initiator and target CHAP secrets and their corresponding usernames. In the configuration provided, while the CHAP secrets for both initiator and target are specified (chapInitiatorSecret and chapTargetInitiatorSecret), only the CHAP target username (chapTargetUsername) is listed. The missing parameter necessary for the complete CHAP configuration is the CHAP initiator username (chapUsername). This username is used along with the chapInitiatorSecret to authenticate the initiator to the storage system.
To correct this, add the chapUsername field to the configuration file, ensuring that the initiator's username matches the configured environment and that it is correctly paired with the chapInitiatorSecret. This inclusion ensures that both sides of the CHAP authentication process are properly identified, thereby providing the necessary security for SAN communication.
For further guidance on configuring CHAP with the Trident ONTAP-SAN driver, refer to the NetApp Trident documentation: NetApp Trident Documentation.
An administrator is setting up NetApp Cloud Tiering. They are creating a new S3 object storage bucket that needs to be compliant with the default IAM policy for the cloud connector.
How must the bucket be configured to meet the policy?
When setting up NetApp Cloud Tiering with an S3 object storage bucket, it is crucial that the bucket configuration adheres to the default IAM policy for the cloud connector. Here's the configuration requirement:
Bucket Configuration with Specific Prefix: The IAM policy often specifies access permissions based on resource names or prefixes. For Cloud Tiering, particularly when integrating with FabricPool technology, the bucket should have a prefix set to fabric-pool. This allows the Cloud Tiering service to correctly identify and interact with the bucket, ensuring compliance with security policies and access controls.
Verify IAM Policy Configuration: Ensure that the IAM policy for the cloud connector includes permissions for operations on the S3 bucket with the fabric-pool prefix. This typically includes permissions to put, get, list, and delete objects within the bucket.
For further information on configuring S3 buckets for NetApp Cloud Tiering and detailed IAM policy settings, please consult the NetApp Cloud Tiering documentation available on the NetApp website: NetApp Cloud Tiering Documentation.
An administrator wants to add more disks to an aggregate to their existing Azure CVO instance. What is the supported method?
To add more disks to an aggregate in an existing Azure CVO instance, the supported method is to use ONTAP System Manager. This tool provides a user-friendly graphical interface for managing ONTAP features, including disk and aggregate management. Here's how:
Access ONTAP System Manager: Log into ONTAP System Manager on your Azure CVO instance.
Manage Disks and Aggregates: Navigate to the Storage or Aggregates section, where you can view existing aggregates and the disks assigned to them.
Add Disks to Aggregate: Select the aggregate you wish to expand and follow the prompts to add additional disks. This process may involve selecting disks from a pool of unassigned disks or reconfiguring existing disk resources.
For more detailed guidance on managing aggregates and disks in Azure CVO, refer to the specific section in the ONTAP System Manager documentation on disk and aggregate management: NetApp ONTAP System Manager.
An administrator has two Kubernetes clusters: one uses GKE, and the other uses AKS. The administrator wants to migrate from Google to Azure. The migration must be application aware and move all components and data for the application.
Which product should the administrator use?
For migrating applications between Kubernetes clusters---specifically from Google Kubernetes Engine (GKE) to Azure Kubernetes Service (AKS)---and ensuring that all components and data are moved in an application-aware manner, the best product to use is Astra Control Service. Here's why:
Application-Aware Migration: Astra Control Service is designed to manage, protect, and move applications in Kubernetes environments. It understands the structure of Kubernetes applications and can manage the entire lifecycle, including migration of application data along with its configuration and state.
Cross-Platform Capability: Astra Control Service supports multiple Kubernetes platforms, making it suitable for migrations from GKE to AKS. It ensures that all parts of the Kubernetes application, including persistent volumes and configurations, are consistently replicated to the new environment.
Seamless Migration Process: The service automates much of the migration process, reducing the complexity and potential for error when moving applications between different cloud providers or Kubernetes services.
For more detailed guidance on using Astra Control Service for Kubernetes migrations, refer to the NetApp documentation: NetApp Astra Control Service Documentation.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Laura Smith
27 days agoGerald Cooper
2 months agoBrenda Clark
2 months agoGerald Flores
3 months agoHeather Robinson
3 months agoSteven Collins
23 days agoLisa Phillips
4 months agoBetty Lewis
4 months agoMatthew Perez
5 months agoJennifer Davis
5 months agoStephanie Lopez
6 months agoDavid Ramirez
6 months agoTimothy Allen
6 months agoDonald Mitchell
6 months agoStephanie Sanchez
6 months agoLisa Thomas
5 months agoMonica White
5 months agoAzzie
7 months agoVerlene
7 months agoHaydee
7 months agoReuben
7 months agoSunshine
8 months agoIzetta
8 months agoJoni
8 months agoMicah
8 months agoLizette
9 months agoTina
9 months agoVelda
9 months agoLaurel
9 months agoStanton
10 months agoBrock
10 months agoDorthy
10 months agoGearldine
10 months agoGianna
11 months agoElke
11 months agoFiliberto
11 months agoTorie
11 months agoIrma
12 months agoSuzi
12 months agoMarquetta
1 year agoElke
1 year agoFallon
1 year agoSue
1 year agoGraham
1 year agoMable
1 year agoMing
1 year agoRolande
1 year agoMerilyn
1 year agoCaitlin
2 years agoRasheeda
2 years agoCarmen
2 years agoMeaghan
2 years agoGlenna
2 years agoLeontine
2 years agoIvory
2 years agoJuan
2 years agoDelmy
2 years agoAja
2 years agoElenor
2 years agoJenifer
2 years agoYolando
2 years agoBeckie
2 years agoJennifer
2 years agoDarrin
2 years agoPok
2 years agoSalena
2 years agoZona
2 years agoReed
2 years ago