
Halloween Special 2026! Get Up to 25% OFF Practice Questions! Limited Time - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

Microsoft SC-200 Exam Questions

Exam Name: Microsoft Security Operations Analyst Exam
Exam Code: SC-200
Related Certification(s): Microsoft Azure Certification
Certification Provider: Microsoft
Actual Exam Duration: 100 Minutes
Number of SC-200 practice questions in our database: 408 (updated: Oct. 29, 2026)
Disscuss Microsoft SC-200 Topics, Questions or Ask Anything Related
0/2000 characters

Daniel Young

29 days ago
I passed the Microsoft Security Operations Analyst certification by drilling threat hunting patterns instead of chasing every product setting. The hardest questions were the ones that required interpreting queries and deciding what to pivot to next, so practice investigations with real sample data.
upvoted 0 times
...

Rachel Martinez

2 months ago
Automated investigation and response and Sentinel playbooks were tested as multi-step incident scenarios asking which automation sequence should run and how to limit scope or escalate. Build and test Logic App runbooks, learn available automated actions and connectors, and map common playbooks to incident workflows, I passed after practicing those end-to-end.
upvoted 0 times
...

Robert Hall

2 months ago
I managed to pass SC-200 after I stopped skimming the data connector and ingestion details and actually configured a few end to end pipelines. Understanding how logs land, normalize, and drive detections made the protection and detection questions much easier.
upvoted 0 times
...

David Robinson

3 months ago
Cloud App Security and app discovery questions often present OAuth app risk or session control scenarios and ask how to manage risky apps or enforce conditional access. Understand app discovery, risk scoring, conditional access integration, and how to create session policies, that familiarity helped a teammate pass the exam.
upvoted 0 times
...

Ashley Lewis

3 months ago
What caught me off guard on SC-200 was how much it ties Defender and Sentinel together in realistic scenarios, but I still managed to pass. Mapping alerts to the right portal and knowing where to investigate saved me time during the exam.
upvoted 0 times

Dina Ansari

29 days ago
Selected Answer: **A** Defender for Endpoint and Sentinel are deeply integrated in SC-200, and the exam leans heavily on knowing which portal handles which workflow. Mapping alerts correctly between the two is not just a concept but a tested skill that shows up in scenario-based questions.
upvoted 0 times
...
...

Andrew Miller

4 months ago
Configuring anti-phishing and safe attachments in Defender for Office 365 appeared as policy configuration questions where you must pick policy priority, match conditions, and the right action for spoofing or malware. Study policy evaluation order, spoof intelligence, and test mail flow safeguards, and someone I know passed the exam and credited Pass4Success for concise practice questions that sped their prep.
upvoted 0 times
...

Jennifer Taylor

4 months ago
I passed the Microsoft Security Operations Analyst exam by spending more time on incident workflow than memorizing features. The questions leaned into triage decisions and remediation order, so rehearsing playbooks and case notes helped a lot.
upvoted 0 times
...

Emily Harris

5 months ago
Defender for Endpoint onboarding and EDR alert investigation showed up as scenario items that mixed onboarding methods with triage steps and required you to pick the correct containment or remediation action. Practice hands-on triage, learn the alert fields and evidence types, and review onboarding options across OS versions, I passed after drilling incident investigations.
upvoted 0 times
...

Richard Wright

5 months ago
SC-200 felt very hands on, so building a small Sentinel lab and practicing KQL daily made the difference for me, and I managed to pass on the first try. The trickiest part was tuning analytic rules without breaking signal quality, so focus on the why behind each alert.
upvoted 0 times

Kenji Do

1 month ago
Selected Answer: **A** Building a Sentinel lab really does reinforce this stuff. The hands-on practice with KQL and analytic rules is what separates candidates who just memorize from those who actually understand signal tuning. Passing first try confirms the approach works.
upvoted 0 times
...
...

Carol Evans

6 months ago
Tuning Microsoft Sentinel analytics rules and KQL was the trickiest part for me because the exam gave scenario questions asking which query detects lateral movement or whether to use scheduled versus fusion rules. Focus on writing and testing KQL, study built-in rule templates and false-positive tuning, and a colleague passed the exam and thanked Pass4Success for a solid question set that saved them time.
upvoted 0 times
...

Melissa Torres

6 months ago
Noticed the tricky part was those scenario questions about tuning detections versus suppressing alerts, deciding which action matched the business requirement was surprisingly subtle, thinking in terms of incident impact and the response workflow helped a lot.
upvoted 0 times

Daniel Taylor

6 months ago
Another tricky area was retention and connector details, since an answer that looks right from a detection angle can be wrong if the data isn't ingested or retained long enough.
upvoted 0 times
...

Amanda Nelson

6 months ago
Helpful tip during my SC-200 prep I practiced identifying qualifiers like "minimize analyst overhead" or "comply with policy" because Microsoft often uses those to steer the best response.
upvoted 0 times
...

Kenneth Martinez

6 months ago
Definitely the wording about "reduce noise" versus "prevent future incidents" changed my answers, so focus on the desired outcome in the prompt.
upvoted 0 times

Karen Green

6 months ago
Meanwhile I stumbled on playbook questions where choosing automation over manual steps depended on whether the task required human validation.
upvoted 0 times

Stephen Hill

5 months ago
Personally the KQL and threat hunting scenarios were confusing because they expected you to infer what logs were authoritative, not just craft a query.
upvoted 0 times
...
...
...
...

Kattie

7 months ago
I passed the Microsoft Security Operations Analyst exam, thanks to the practice questions from Pass4Success. There was a challenging question on setting up custom alerts in Azure Sentinel. I wasn't entirely sure about the alert logic, but I made it through.
upvoted 0 times
...

Pansy

7 months ago
Just became a Microsoft Certified Security Operations Analyst. Pass4Success was key to my success.
upvoted 0 times
...

Eun

7 months ago
Pass4Success helped me ace the Microsoft Security exam in record time. Highly recommended!
upvoted 0 times
...

Kayleigh

8 months ago
MS-SC200 exam conquered! Pass4Success questions were incredibly similar to the real thing.
upvoted 0 times
...

Ahmed

8 months ago
Initial nerves had me doubting myself, yet Pass4Success’ focused labs and clear explanations turned anxiety into readiness, so keep practicing and believe in your preparation—you’ve got this.
upvoted 0 times
...

Ernest

8 months ago
For me, endpoint detection logic and alert prioritization were tough; Pass4Success simulations trained me to triage under pressure.
upvoted 0 times
...

Kristofer

8 months ago
Conquering the Microsoft Security Operations Analyst exam was a real challenge, but the Pass4Success practice exams were a godsend. My top tip? Familiarize yourself with the exam format and structure.
upvoted 0 times
...

Oretha

9 months ago
Happy to report that I passed the Microsoft Security Operations Analyst exam. The Pass4Success practice questions were very helpful. One question that had me stumped was about configuring threat analytics in Microsoft 365 Defender. I wasn't sure about the exact configuration, but I passed.
upvoted 0 times
...

Arleen

9 months ago
Passing the Microsoft Security Operations Analyst exam was a huge relief, and the Pass4Success practice tests played a big part in my success. My tip? Stay focused and don't let the pressure get to you.
upvoted 0 times
...

Vincenza

9 months ago
Thanks to Pass4Success, I'm now a certified Microsoft Security Operations Analyst. Great resource!
upvoted 0 times
...

Wade

9 months ago
Passed the Microsoft Security Operations Analyst exam with flying colors. Kudos to Pass4Success!
upvoted 0 times
...

Blondell

10 months ago
If you're prepping for the Microsoft Security Operations Analyst exam, the pass4success practice exams are a must. My advice? Revise thoroughly and don't be afraid to ask for help when you need it.
upvoted 0 times
...

Paola

10 months ago
Acing the Microsoft Security Operations Analyst exam was no easy feat, but the Pass4Success practice tests were a game-changer. My top tip? Manage your time wisely and don't get bogged down in any one section.
upvoted 0 times
...

Alba

10 months ago
I was jittery before the exam, but pass4success gave me structured practice and real-world scenarios that built my confidence, and now I know future test-takers can do this too—stay persistent and trust the prep process.
upvoted 0 times
...

Leota

10 months ago
MS-SC200 success! Pass4Success provided exactly what I needed for efficient preparation.
upvoted 0 times
...

Lorrie

11 months ago
Grateful for Pass4Success - their questions helped me pass the Microsoft Security exam in no time.
upvoted 0 times
...

Bok

11 months ago
Memory-heavy topics like log correlation and SOAR workflow were brutal; pass4success practice exams gave me the repeat exposure I needed.
upvoted 0 times
...

Jeannetta

11 months ago
The tricky questions on incident response playbooks were brutal, but the practice exams from pass4success finally made the steps click.
upvoted 0 times
...

Luis

11 months ago
Security Operations Analyst certified! Pass4Success made it possible with their relevant exam questions.
upvoted 0 times
...

Andra

12 months ago
I passed the Microsoft Security Operations Analyst exam, and the Pass4Success practice questions were a great resource. There was a tricky question on enabling threat intelligence in Azure Defender. I wasn't confident about the exact steps, but I still succeeded.
upvoted 0 times
...

Ling

12 months ago
Thrilled to have passed the Microsoft Security Operations Analyst exam. The practice questions from Pass4Success were extremely useful. One question that confused me was about configuring data retention policies in Azure Sentinel. I wasn't sure about the correct settings, but I managed to pass.
upvoted 0 times
...

Penney

1 year ago
Aced the MS-SC200 exam today. Pass4Success materials were a lifesaver for quick prep!
upvoted 0 times
...

Herminia

1 year ago
I successfully passed the Microsoft Security Operations Analyst exam, and the Pass4Success practice questions were a big help. There was a tough question on setting up automated investigation and response in Microsoft 365 Defender. I wasn't entirely sure about the configuration, but I still passed.
upvoted 0 times
...

Joye

1 year ago
The hardest part for me was threat hunting patterns and MITRE ATT&CK mappings—Pass4Success drills helped me connect the dots faster with real-world scenarios.
upvoted 0 times
...

Nadine

1 year ago
Excited to share that I passed the Microsoft Security Operations Analyst exam. The Pass4Success practice questions were spot on. One question that puzzled me was about configuring endpoint detection and response in Azure Defender. I wasn't clear on the exact settings, but I passed nonetheless.
upvoted 0 times
...

Freeman

1 year ago
Passing the Microsoft Security Operations Analyst exam was a game-changer for me. The Pass4Success practice exams were a lifesaver - they really helped me identify my weak areas and focus my study.
upvoted 0 times
...

Glennis

1 year ago
Just passed the Microsoft Security Operations Analyst exam! Thanks to Pass4Success for the spot-on practice questions.
upvoted 0 times
...

Ahmed

1 year ago
I passed the Microsoft Security Operations Analyst exam, thanks to the practice questions from Pass4Success. There was a challenging question on setting up workbooks in Azure Sentinel for threat monitoring. I wasn't entirely sure about the configuration, but I made it through.
upvoted 0 times
...

Ruthann

1 year ago
Happy to report that I passed the Microsoft Security Operations Analyst exam. The Pass4Success practice questions were very helpful. One question that had me stumped was about configuring advanced hunting queries in Microsoft 365 Defender. I wasn't sure about the query syntax, but I passed.
upvoted 0 times
...

Rhea

1 year ago
Thrilled to have passed the Microsoft Security Operations Analyst exam. Big thanks to Pass4Success!
upvoted 0 times
...

Lynda

1 year ago
Pass4Success's relevant questions made all the difference. Just got my MS-SOA certification!
upvoted 0 times
...

Nina

1 year ago
So happy I chose Pass4Success for my Microsoft Security Ops Analyst exam prep. Passed easily!
upvoted 0 times
...

Gayla

2 years ago
Passed the MS-SOA exam today! Pass4Success's materials were invaluable for quick preparation.
upvoted 0 times
...

Annabelle

2 years ago
Pass4Success's exam prep was spot on. Just became a certified Microsoft Security Operations Analyst!
upvoted 0 times
...

Roxane

2 years ago
Thanks to Pass4Success, I nailed the Microsoft Security Ops Analyst exam in record time!
upvoted 0 times
...

Patrick

2 years ago
Pass4Success's practice questions were key to my success on the MS-SOA exam. Highly recommend!
upvoted 0 times
...

Lettie

2 years ago
I passed the Microsoft Security Operations Analyst exam, and the Pass4Success practice questions were a great resource. There was a tricky question on enabling threat protection for Azure resources using Azure Defender. I wasn't confident about the exact steps, but I still succeeded.
upvoted 0 times
...

Horace

2 years ago
Couldn't have passed the Microsoft Security Operations Analyst exam without Pass4Success. Thank you!
upvoted 0 times
...

Macy

2 years ago
Thrilled to have passed the Microsoft Security Operations Analyst exam. The practice questions from Pass4Success were extremely useful. One question that confused me was about setting up data connectors in Azure Sentinel. I wasn't sure about the correct connector to use, but I managed to pass.
upvoted 0 times
...

Alishia

2 years ago
Pass4Success made studying for the MS-SOA exam a breeze. Passed with flying colors!
upvoted 0 times
...

Adell

2 years ago
I successfully passed the Microsoft Security Operations Analyst exam, and the Pass4Success practice questions were a big help. There was a tough question on configuring incident response policies in Microsoft 365 Defender. I wasn't entirely sure about the policy settings, but I still passed.
upvoted 0 times
...

Jennifer

2 years ago
Excited to announce that I passed the Microsoft Security Operations Analyst exam. The Pass4Success practice questions were invaluable. One question that had me second-guessing was about setting up vulnerability assessments in Azure Defender. I wasn't clear on the exact configuration, but I passed nonetheless.
upvoted 0 times
...

Lucina

2 years ago
Grateful for Pass4Success - their materials were crucial for my Microsoft Security Ops Analyst certification.
upvoted 0 times
...

Asha

2 years ago
I passed the Microsoft Security Operations Analyst exam, thanks to the practice questions from Pass4Success. There was a challenging question on creating custom analytics rules in Azure Sentinel. I wasn't sure about the KQL query syntax, but I made it through.
upvoted 0 times
...

Ryan

2 years ago
Happy to share that I passed the Microsoft Security Operations Analyst exam. The Pass4Success practice questions were spot on. One question that puzzled me was about configuring attack surface reduction rules in Microsoft 365 Defender. I wasn't confident about the settings, but I still succeeded.
upvoted 0 times
...

Michal

2 years ago
Wow, aced the MS-SOA exam! Pass4Success really helped me prepare quickly.
upvoted 0 times
...

Leigha

2 years ago
Excellent. Any final thoughts on the exam?
upvoted 0 times
...

Linsey

2 years ago
Just cleared the Microsoft Security Operations Analyst exam! The practice questions from Pass4Success were a great help. There was a tricky question on how to enable Just-In-Time VM access in Azure Defender. I was unsure about the exact steps, but I still managed to get through.
upvoted 0 times
...

Dell

2 years ago
Overall, the exam was challenging but fair. It really tests your practical knowledge of Microsoft security tools and practices. Again, I can't stress enough how helpful Pass4Success was in my preparation. Their materials were crucial in helping me pass the exam.
upvoted 0 times
...

Santos

2 years ago
I recently passed the Microsoft Security Operations Analyst exam, and the Pass4Success practice questions were incredibly helpful. One question that stumped me was about configuring playbooks in Azure Sentinel to automate threat responses. I wasn't entirely sure about the correct sequence of actions, but I managed to pass the exam.
upvoted 0 times
...

Sabra

2 years ago
Just passed the Microsoft Security Operations Analyst exam! Thanks Pass4Success for the spot-on practice questions.
upvoted 0 times
...

Claudio

2 years ago
With the help of Pass4Success practice questions, I passed the Microsoft Security Operations Analyst exam. The exam included topics like configuring detections in Microsoft Defender XDR and managing a security operations environment. One question that stood out to me was about designing and configuring a Microsoft Sentinel workspace, which required a good understanding of the concepts to answer correctly.
upvoted 0 times
...

Mila

2 years ago
The exam covers threat hunting scenarios using Microsoft 365 Defender and Azure Sentinel. Practice creating custom detection rules and understand how to use threat intelligence in your investigations.
upvoted 0 times
...

Joni

2 years ago
My exam experience for the Microsoft Security Operations Analyst exam was successful, thanks to Pass4Success practice questions. I had to configure detections in Microsoft Defender XDR and ingest data sources in Microsoft Sentinel. There was a question related to managing assets and environments in a security operations environment, which I had to think through carefully before selecting the answer.
upvoted 0 times
...

Della

2 years ago
Don't overlook Azure AD Identity Protection. The exam includes questions on risk policies and multi-factor authentication configuration. Know how to interpret risk detection reports.
upvoted 0 times
...

Maryann

2 years ago
The exam tests your knowledge of configuring Microsoft 365 Defender. Be prepared to answer questions about setting up data connectors and configuring automated response actions.
upvoted 0 times
...

Gerald

2 years ago
Just passed the Microsoft Security Operations Analyst exam! Watch out for questions on Azure Sentinel KQL queries - they're tricky. Focus on understanding how to write effective queries for threat hunting. Big thanks to Pass4Success for their spot-on practice questions that helped me prep quickly!
upvoted 0 times
...

Tenesha

2 years ago
I passed the Microsoft Security Operations Analyst exam with the help of Pass4Success practice questions. The exam covered topics like configuring settings in Microsoft Defender XDR and designing a Microsoft Sentinel workspace. One question that I remember was about configuring protections in Microsoft Defender security technologies, which I found a bit tricky but managed to answer correctly.
upvoted 0 times
...

darrena

2 years ago
I highly recommend Pass4Success to anyone preparing for the Microsoft SC-200 exam. The study materials are top-notch, and the PDF exam questions is well-designed to help you pass the exam with confidence.
upvoted 1 times
...

kalasan

2 years ago
Pass4Success is amazing! I passed my SC-200 exam on the first try thanks to their detailed PDF questions and web-based practice tests. The material was up-to-date and very relevant.
upvoted 1 times
...

Free Microsoft SC-200 Exam Actual Questions

Note: Premium Questions for SC-200 were last updated On Oct. 29, 2026 (see below)

Question #1

You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 Windows 11 devices that are onboarded to Microsoft Defender for Endpoint You discover unauthorized changes to the membership of the Administrators group on the devices. You need to configure a solution that meets the following requirements:

* Every hour, check the Administrators group membership of each endpoint.

* When a change to the Administrators group membership is detected, create an incident in Microsoft Defender XDR.

What should you create first?

Reveal Solution Hide Solution
Correct Answer: D

Question #2

You have a Microsoft 365 subscription that uses Microsoft Defender XDR.

You are investigating an incident.

You need to review the incident tasks that were performed. The solution must include a query that will display the incidents in a workbook, and then display the tasks of each incident in another grid.

Which table should you target in the query?

Reveal Solution Hide Solution
Correct Answer: A

In Microsoft Defender XDR (and Microsoft Sentinel), the table that stores information about incidents---including their status, severity, classification, associated alerts, and related tasks---is the SecurityIncident table. This table is part of the advanced hunting schema and Microsoft Sentinel workspace schema when Microsoft Defender XDR incidents are synchronized to Log Analytics.

Microsoft's documentation for the SecurityIncident table describes it as:

''Contains information about incidents generated in Microsoft Sentinel or Microsoft 365 Defender, including incident title, ID, description, severity, provider, owner, and related entities. It can be used to track and analyze incidents and their associated alerts or tasks.''

When you need to display incidents in a workbook and also visualize incident tasks or actions performed under each one, you must query the SecurityIncident table. From there, you can join or expand incident details such as tasks or alert relationships for deeper investigation.

Other options are not suitable for this requirement:

SecurityEvent -- contains raw Windows event log data (e.g., logon events, process creation) and is unrelated to incident-level information.

SentinelAudit -- contains audit trail records of changes and administrative actions within Sentinel (e.g., who modified analytics rules), not incidents or tasks.

SecurityAlert -- contains individual alerts that may belong to incidents, but it doesn't include incident tasks or groupings by incident.

Therefore, to query incident information and related tasks in a workbook, the correct target table is SecurityIncident.


Question #3

You have a Microsoft 365 subscription.

You have 1,000 Windows devices that have a third-party antivirus product installed and Microsoft Defender Antivirus in passive mode. You need to ensure that the devices are protected from malicious artifacts that were undetected by the third-party antivirus product Solution: You enable automated investigation and response (AIR).

Does this meet the goal?

Reveal Solution Hide Solution
Correct Answer: B

Automated Investigation and Response (AIR) automates investigation and remediation actions for alerts that Defender already detects: it triages alerts, runs investigation playbooks, and can execute remediation (quarantine files, terminate processes, remove persistence) based on the investigation outcome. AIR is powerful for reducing analyst load and quickly remediating detected threats. However, AIR only runs in response to detections/alerts it receives---if the third-party AV completely misses an artifact and no EDR/behavioral detection generates an alert, AIR will not be triggered. In contrast, EDR in block mode is specifically built to catch post-breach detections that the primary AV missed and to remediate them. Therefore, enabling AIR alone does not guarantee protection from artifacts missed by the third-party antivirus; AIR helps remediate once a detection exists but does not itself create the missed detection coverage that EDR in block mode provides.


Question #4

You have a Microsoft 365 E5 subscription that contains 500 Windows 11 devices.

You have a Microsoft Defender for Endpoint deployment that has the following settings:

Discovery mode: Basic

Live Response: Disabled

Enable EDR in block mode: Off

Tamper Protection: Off

You need to implement automatic attack disruption in Microsoft Defender XDR.

What should you do?

Reveal Solution Hide Solution
Correct Answer: A

Microsoft Defender XDR's Automatic attack disruption requires EDR in block mode to be enabled. This feature allows Defender for Endpoint to block or contain malicious activities, even when the primary antivirus engine fails to detect or block them initially.

According to Microsoft Defender documentation, attack disruption relies on real-time EDR response capabilities and EDR in block mode to isolate compromised users or devices automatically. Without EDR in block mode, Defender can only alert --- not stop --- ongoing attacks.

Enabling EDR in block mode integrates the EDR layer with Microsoft Defender Antivirus to automatically contain lateral movement and credential theft activities. While Tamper Protection, Live Response, and Standard Discovery are valuable, they do not directly enable automatic attack disruption.

Correct Answe r: A. Set Enable EDR in block mode to On


Question #5

You have a Microsoft 365 E5 subscription that uses Microsoft Copilot for Security. You plan to run the following code to create a custom Copilot for Security plugin.
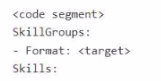
You need to specify a format and complete the code segment. Which format should you use for the variable?

Reveal Solution Hide Solution
Correct Answer: C

When authoring a custom plugin for Copilot for Security that queries security telemetry and returns structured results, the expected query/target format is Kusto Query Language (KQL). Copilot for Security integrates with Microsoft security data platforms (Microsoft Sentinel/Log Analytics and Defender tables) where investigative and hunting queries are expressed in KQL. Official plugin examples and guidance show the plugin invoking a KQL query against a workspace or a Defender table and returning the results in the plugin response payload. KQL is the language used to interrogate event, alert, and entity tables (for example, DeviceProcessEvents, SecurityAlert, MicrosoftGraphActivityLogs) and is the supported format when a plugin's purpose is to retrieve and return telemetry to Copilot for Security. Other formats listed (API, GPT, SQL) are not the standard query language for Defender/Sentinel data: APIs are endpoints for programmatic access, GPT is a model format, and SQL is not used for Azure Monitor / Sentinel tables. Therefore when the plugin's <target> must specify the query format against security telemetry, KQL is the correct choice.


Unlock Premium SC-200 Exam Questions with Advanced Practice Test Features:
  • Select Question Types you want
  • Set your Desired Pass Percentage
  • Allocate Time (Hours : Minutes)
  • Create Multiple Practice tests with Limited Questions
  • Customer Support
Get Full Access Now

Save Cancel