
 MENU

Exhibit:
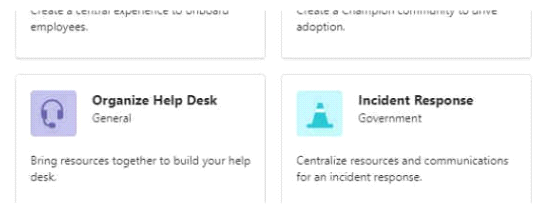
You need to ensure that the user sees only the Manage a Project template.
What should you do?
Suggested Answer: C
Get Premium MS-700 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
13 comments · newest first
YO
Yolando
11 months ago
I disagree, modifying policies seems more complex than necessary.
NE
Nelida
11 months ago
Definitely B! Templates need to be managed from the admin center.
VI
Viki
12 months ago
Wait, can you really do that with PowerShell?
CA
Carolynn
12 months ago
Nah, I’m pretty sure C is correct.
AR
Arlyne
1 year ago
I think option B is the way to go.
FE
Felix
1 year ago
I’m leaning towards option C since it mentions modifying the templates policies, which seems relevant to ensuring the user sees only one template.
KA
Karl
1 year ago
I feel like modifying the team templates directly would be the way to go, but I can't recall if that’s what the question is asking for.
MI
Miles
1 year ago
I remember a practice question about managing templates, and I think it was related to PowerShell. Could it be option A or D?
NO
Nobuko
1 year ago
I think we might need to modify the templates policies from the Teams admin center, but I'm not entirely sure if that's the right approach.
CE
Celeste
1 year ago
Hmm, this seems straightforward. I think I'll go with option B - "property" to read the record's Id column.
MI
Mira
1 year ago
Okay, let me see. As a DSH, Preamble Hospital likely receives financial assistance from the government to help cover the costs of providing care to a disproportionately high number of Medicaid and uninsured patients. That suggests option B is the best answer.
JA
Janey
1 year ago
I'm a bit confused by this question. VPN, S/MIME, and HTTP all seem like they could be used for security, but I'm not sure which one would be the best recommendation for this specific scenario. I'll have to review my notes on web service security.
SH
Shantay
1 year ago
Okay, let's see. Wardriving and sniffing sound like they could be passive attacks, since they involve monitoring the network without actively interfering. I'll go with those.