Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

Juniper JN0-232 Exam Questions

Exam Name: Juniper Security, Associate Exam
Exam Code: JN0-232 JNCIA-SEC
Related Certification(s): Juniper Junos Security Certification
Certification Provider: Juniper
Number of JN0-232 practice questions in our database: 110 (updated: Oct. 31, 2026)
Expected JN0-232 Exam Topics, as suggested by Juniper :
  • Topic 1: SRX Series Service Gateways: Covers the foundational architecture, hardware, interfaces, initial setup, and traffic processing of SRX devices, along with J-Web and vSRX virtual firewall basics.
  • Topic 2: Junos OS Security Objects: Covers the core building blocks of Junos security configuration, including zones, screens, address objects, and application/ALG objects.
  • Topic 3: Security Policies: Covers how zone-based, global, and unified security policies are structured and used to control traffic.
  • Topic 4: Network Address Translation: Covers the concepts and operation of source, destination, and static NAT on Junos devices.
  • Topic 5: Content Security: Covers UTM-style features such as content filtering, web filtering, antivirus, and antispam protections.
  • Topic 6: Monitoring and Troubleshooting: Covers techniques for troubleshooting security policies, validating expected behavior, and monitoring packet flow.
Disscuss Juniper JN0-232 Topics, Questions or Ask Anything Related
0/2000 characters

Ankit Chaudhary

4 days ago
Network Address Translation questions tested layered translations and whether ports or addresses are preserved, asking you to compute the final packet values after policy and interface-based NAT. A study buddy passed by working through many static, source and destination NAT scenarios, so memorize translation order, matching criteria and port preservation rules.
upvoted 0 times
...

Tanvi Sinha

10 days ago
Network Address Translation items commonly ask you to pick the correct rule type or predict the translated address after several NAT rules are applied, and forgetting processing order will cost you points. I passed after mapping source and destination NAT flows on paper and thanks Pass4Success for providing good collection of exam questions for preparation in short time.
upvoted 0 times
...

Vikram Tiwari

10 days ago
Network Address Translation items tend to be situational, asking whether source NAT, destination NAT, or policy NAT applies and how the processing order affects return traffic. Study the NAT processing sequence on SRX, mapping of pools and interfaces, and convert real scenarios into NAT rule logic to avoid common traps.
upvoted 0 times
...

Aarav Kapoor

17 days ago
Network Address Translation questions give a topology and ask for the resulting translated addresses for sessions, mixing source NAT, destination NAT, and interface-based behavior. Drill examples of static 11 and dynamic pool translations, learn rule versus interface NAT precedence, and practice computing resulting IP mappings.
upvoted 0 times
...

Imran Malik

27 days ago
I managed to pass the Juniper Security, Associate exam, and content security caught me off guard because it is easy to memorize terms without understanding where it applies on SRX. I focused on real configuration order and what actually gets evaluated in a policy match.
upvoted 0 times
...

Sara Ali

1 month ago
Security Policies questions frequently present a chain of policies and ask which rule permits or denies traffic, with traps involving implicit deny, policy order, and application inspection. A friend managed to pass after repeatedly using the policy trace and labbing policy ordering, so focus on match conditions, action outcomes, and how application identification affects policy hits.
upvoted 0 times
...

Laura King

1 month ago
Security Policies problems were tricky because many questions require you to evaluate multiple rules and decide which one hits first based on order and specificity. I passed by running through policy hit scenarios, checking logging options and understanding from zone to zone matching.
upvoted 0 times
...

Soo Vo

1 month ago
Security Policies questions commonly present multiple from-to rules and require you to determine which policy matches based on order, application filters, or counters. Make sure you understand policy evaluation order, implicit deny behavior, and how policy options like log and then-actions change traffic handling.
upvoted 0 times
...

Richard Harris

2 months ago
Security Policies often appear as troubleshooting scenarios asking why traffic is blocked despite an apparent permit the trick is implicit deny, policy order, or mismatched application versus service criteria. Review policy evaluation order, the impact of from/to zones, and how to use policy counters and show commands to verify matches.
upvoted 0 times
...

Sanjay Chopra

2 months ago
Passed JN0-232 last week, and the troubleshooting items were trickier than expected since they mix show commands with policy and NAT logic. Reviewing session inspection, logs, and basic flow trace steps helped me answer faster under time pressure.
upvoted 0 times
...

Aiko Hoang

2 months ago
Junos OS Security Objects questions often showed snippets of address-book and application-set configurations and asked which object would match a given flow, and the subtlety around nested groups cost me time. Someone I know passed by spending time on address-book precedence, longest-prefix matching and how address-sets expand, so practice with real config examples.
upvoted 0 times
...

Hanna Michel

2 months ago
Junos OS Security Objects questions often ask you to identify which object type is appropriate or to follow how address-book entries and application-sets are resolved in a policy. Drill the differences between address, address-set, service, and application objects and practice parsing config snippets to see how objects are referenced.
upvoted 0 times
...

Pooja Singh

2 months ago
Junos OS Security Objects appeared as config parsing questions that show address and service objects and ask which policy will match. A colleague who took the test passed by practicing address book precedence, object groups and how objects are referenced at different hierarchy levels, so focus on object resolution and naming.
upvoted 0 times
...

Ivan Durand

3 months ago
Junos OS Security Objects show up as config interpretation questions where they display an address-book entry, application-set, or service-object and ask which policy will match given traffic. Practice referencing objects in policies, understand address-book hierarchy and precedence, and know differences between application definitions and application-sets so you can map packets to objects quickly.
upvoted 0 times
...

Giovanni Popov

3 months ago
I just cleared the Juniper JN0-232, and the biggest win was building a small SRX lab to practice security zones, policies, and NAT until the flow made sense. The exam wording can be subtle, so I slowed down and mapped each question back to how I would configure it in Junos.
upvoted 0 times
...

Diego Fernandez

3 months ago
SRX Series Service Gateways had a lot of scenario questions where you had to follow packet flow through interfaces and zones to see why traffic was dropped, which was tricky because logical interfaces and routing instances change the path. A colleague passed the exam and thanks Pass4Success for providing a good collection of exam questions for preparation in short time, so drill packet flow, zone assignment, and session table behavior until it’s second nature.
upvoted 0 times
...

Yusuf Aziz

3 months ago
SRX Series Service Gateways were a big part of the exam and I saw several packet-flow scenarios where you must trace a packet through zones, NAT, and policy to determine the outcome. Practice lab tracing and get comfortable with zone-based processing and threat profiles that hands-on work helped me pass JN0-232 in a short time, and I appreciated Pass4Success for a focused question collection.
upvoted 0 times
...

Neha Yadav

3 months ago
SRX Series Service Gateways questions often present a packet flow scenario where you must identify which interface family or zone drops traffic due to a misapplied security zone. I passed the exam after drilling interface to zone mappings and security policy behavior on an SRX and thanks Pass4Success for providing good collection of exam questions for preparation in short time.
upvoted 0 times
...

Ling Dang

4 months ago
SRX Series Service Gateways were a major focus with scenario questions about failover, zone assignments, and interface types I passed the JN0-232 and managed to do it quickly thanks to Pass4Success for the concentrated question set. Those exam items often walk through a failing session and ask which chassis-cluster state or security zone change caused the outage, so study SRX packet flow, failover states, and how logical interfaces and aggregated links behave.
upvoted 0 times
...

Free Juniper JN0-232 Exam Actual Questions

Note: Premium Questions for JN0-232 were last updated On Oct. 31, 2026 (see below)

Question #1

Which two statements are correct about security policies in SRX Series Firewalls? (Choose two.)

Reveal Solution Hide Solution
Correct Answer: C, D

In the JNCIA-SEC SRX security policy context, standard security policies control transit traffic passing through the firewall. They are not the normal mechanism for permitting management or protocol traffic destined to the SRX itself; that type of self or exception traffic is controlled with host-inbound-traffic settings. Security policies can be configured between different zones, which is inter-zone policy, or within the same zone, which is intra-zone policy. Therefore, option C is correct because policies can apply to both intra-zone and inter-zone flows. Option D is correct in the standard SRX policy model because security policies are used to control traffic transiting the firewall. Options A and B are not correct for this topic scope.


Question #2

Which statement is correct about security policies?

Reveal Solution Hide Solution
Correct Answer: B

Zone-based security policies are configured in a context that includes both a source zone and a destination zone. Juniper describes this policy context as from-zone to to-zone, and traffic is classified by matching source zone, destination zone, source address, destination address, and application. Option B is therefore correct. Screens are applied earlier in flow processing than policy evaluation, so option A is incorrect. Security policy lookup is part of first path processing when a session is created; once the session exists, fast path traffic normally follows the established session rather than re-evaluating policy for every packet. Option D is also incorrect because zone-based policies can apply to both intra-zone and inter-zone traffic, depending on the configured context.


Question #3

You have created a series of security policies permitting access to a variety of services. You now want to create a policy that blocks access to all other services for all user groups.

What should you create in this scenario?

Reveal Solution Hide Solution
Correct Answer: A

To enforce a catch-all blocking policy after other specific policies, the correct solution is a global security policy (Option A).

Global policies can apply universally across zones, and an administrator can configure a final ''deny all'' rule to block any unmatched traffic.

ATP policy (Option B): Protects against advanced threats, not used for catch-all rule enforcement.

IDP policy (Option C): Focuses on intrusion detection and prevention signatures, not general traffic blocking.

Integrated user firewall policy (Option D): Applies policies based on user identity, but it does not provide a universal block across all services.

Correct Solution: Global security policy


Question #4

In which order does Junos OS process the various forms of NAT?

Reveal Solution Hide Solution
Correct Answer: A

NAT processing in Junos OS follows a strict sequence to ensure correct packet handling:

Static NAT -- applied first because it provides a permanent one-to-one bidirectional mapping.

Destination NAT -- applied second to translate inbound destination addresses, often used for servers in private networks.

Source NAT -- applied last to translate outbound private source addresses to public ones.

This ensures deterministic behavior and avoids conflicts between translation types.

Options B, C, and D list incorrect sequences.

Correct Order: static NAT destination NAT source NAT


Question #5

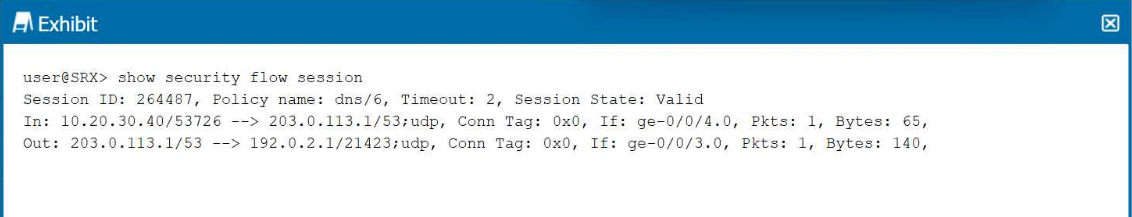
Click the Exhibit button.

Referring to the exhibit, which two statements are correct about the traffic flow shown in the exhibit? (Choose two.)

Reveal Solution Hide Solution
Correct Answer: B, D

Inbound Flow (before NAT):

Source = 10.20.30.40 (internal private IP)

Destination = 203.0.113.1 (public DNS server)

Outbound Flow (after NAT):

Source = 192.0.2.1 (translated IP)

Destination = 203.0.113.1 (unchanged)

Analysis:

The source IP (10.20.30.40) was translated to 192.0.2.1. This indicates Source NAT was applied Option B is correct.

The destination IP changed between the inbound and outbound view. Inbound it was 203.0.113.1, and outbound it is still 203.0.113.1 in appearance, but notice the reversal: the session entry shows it as the outbound 'source' side. This confirms Destination NAT translation has occurred for return flow consistency Option D is correct.

Option A: Incorrect. The original source IP was indeed translated.

Option C: Incorrect. The destination IP did change in the flow processing.

Correct Statements:

The original source IP address was translated to a new source IP address.

The original destination IP address was translated to a new destination IP address.


Unlock Premium JN0-232 Exam Questions with Advanced Practice Test Features:
  • Select Question Types you want
  • Set your Desired Pass Percentage
  • Allocate Time (Hours : Minutes)
  • Create Multiple Practice tests with Limited Questions
  • Customer Support
Get Full Access Now

Save Cancel