
Free Preparation Discussions
 MENU

Google Professional Cloud DevOps Engineer Exam Questions
Free Google Professional Cloud DevOps Engineer Exam Actual Questions
Note: Premium Questions for Professional Cloud DevOps Engineer were last updated On Nov. 02, 2026 (see below)
You are responsible for the reliability of a custom-built, distributed file storage service that your company uses internally. This service handles thousands of file uploads and downloads daily. You need to define a service level indicator (SLI) to measure the reliability of your service usage and configure alerts to be notified of potential issues. Which SLI should you use to measure the reliability of the service?
SLIs are quantitative measures of service behavior. For reliability, success rate (successful vs. total requests) is the most fundamental metric.
''The most common SLIs are request success rate, availability, and latency.''
--- Google SRE Workbook: Implementing SLIs
''Availability SLIs often look like 'the fraction of requests that succeed.'''
--- Google SRE Book
Option C directly maps to this definition and is the most accurate and measurable indicator of overall reliability.
You are currently planning how to display Cloud Monitoring metrics for your organization's Google Cloud projects. Your organization has three folders and six projects:
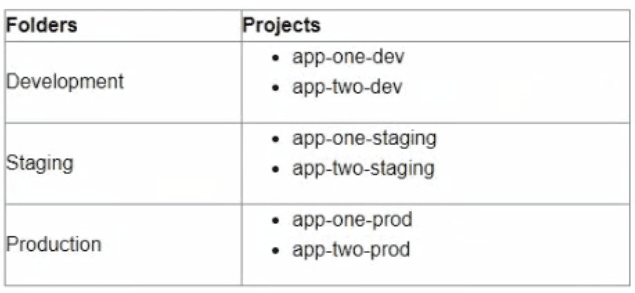
You want to configure Cloud Monitoring dashboards lo only display metrics from the projects within one folder You need to ensure that the dashboards do not display metrics from projects in the other folders You want to follow Google-recommended practices What should you do?
The best option for configuring Cloud Monitoring dashboards to only display metrics from the projects within one folder is to create new scoping projects for each folder. A scoping project is a project that defines which resources are monitored by Cloud Monitoring. You can create new scoping projects for each folder by using the gcloud monitoring register-project command. This way, you can associate each scoping project with a folder and only monitor the resources within that folder. You can then configure Cloud Monitoring dashboards to use the scoping projects as data sources and only display metrics from the projects within one folder.
Your team has an application built by using a Dockerfile. The build is executed from Cloud Build, and the resulting artifacts are stored in Artifact Registry. Your team is reporting that builds are slow. You need to increase build speed, while following Google-recommended practices. What should you do?
To speed up Docker builds, optimize layer caching. Google Cloud recommends using --cache-from with Artifact Registry, and placing frequently changed files late in the Dockerfile so earlier layers can be reused.
''Put instructions that are less likely to change (like installing packages) early in the Dockerfile, and more frequently changing lines (like copying app code) near the end.''
--- Dockerfile Best Practices
''Use the --cache-from argument to pull layers from previously built images in Artifact Registry.''
--- Cloud Build Docker Caching
This dramatically reduces build time by avoiding redundant rebuilds of static layers.
You are configuring a CI pipeline. The build step for your CI pipeline integration testing requires access to APIs inside your private VPC network. Your security team requires that you do not expose API traffic publicly. You need to implement a solution that minimizes management overhead. What should you do?
Cloud Build Private Pools allow your builds to run in a secure, isolated environment with direct access to resources inside your private VPC network, without exposing them to the public internet. This is the Google-recommended approach for minimizing management overhead while maintaining strong security boundaries.
From the official documentation:
'Private pools run your builds in a dedicated and secure environment that can connect to private network resources.'
--- Cloud Build Private Pools Overview
'You can configure private pools to access resources in a VPC network, which enables secure access to services without using public IPs.'
--- Accessing Private Resources
This method eliminates the need to create and manage additional compute instances or complex load balancing setups, providing seamless integration with your private services during CI pipeline execution.
You are developing a Node.js utility on a workstation in Cloud Workstations by using Code OSS. The utility is a simple web page, and you have already confirmed that all necessary firewall rules are in place. You tested the application by starting it on port 3000 on your workstation in Cloud Workstations, but you need to be able to access the web page from your local machine. You need to follow Google-recommended security practices. What should you do?
Cloud Workstations provides a secure way to preview web applications using built-in preview links, which expose internal ports only via authenticated and authorized access --- no public IP exposure required.
''To preview your app, click the preview icon in the Code OSS panel, which securely tunnels the service to your browser.''
--- Cloud Workstations - Previewing your app
This adheres to Google's security best practices by avoiding public IPs or manual tunneling while enabling developer efficiency.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Geeta Chopra
3 days agoHarsh Singh
18 days agoNeha Dubey
1 month agoHamza Qureshi
2 months agoLinda White
2 months agoShruti Rao
3 months ago