
 MENU

Exhibit
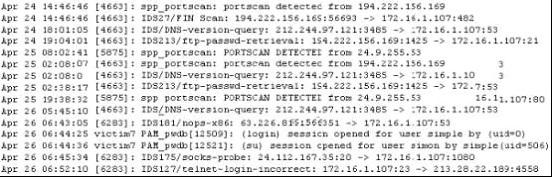
Study the log given in the exhibit,
Precautionary measures to prevent this attack would include writing firewall rules. Of these firewall rules, which among the following would be appropriate?
Suggested Answer: B
Get Premium CPEH-001 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
You only want your or your ISP's outside DNS to be able to contact your inside DNS. All other traffic should be directed against the outside DNS.
12 comments · newest first
AM
Amie
12 months ago
Wait, blocking all UDP? That seems risky, right?
DA
Dana
12 months ago
Totally agree with option C, it's a solid precaution.
ZA
Zana
1 year ago
Allowing UDP 53 from DNS to outside is necessary for queries.
HE
Herminia
1 year ago
I think blocking all UDP traffic is too extreme.
AR
Arlette
1 year ago
Disallowing UDP 53 to the DNS server is a must!
TY
Ty
1 year ago
I’m a bit confused about the difference between TCP and UDP in this context. I think disallowing TCP 53 from secondaries is important, but I’m not entirely sure.
DA
Danica
1 year ago
I think we practiced a similar question where we had to decide on firewall rules for DNS. I feel like disallowing UDP 53 from outside makes sense, but I can't recall the exact reasoning.
WI
Willodean
1 year ago
I remember we discussed how blocking certain UDP traffic can help prevent DNS attacks, but I'm not sure if blocking all UDP is too extreme.
EL
Elenore
1 year ago
I remember that allowing UDP 53 from the DNS server to the outside is usually necessary for responses, but I wonder if that could be risky too.
JE
Jesus
1 year ago
Based on the information provided, I think option C focuses on the right elements - customer and market relevance supported by operational excellence. That seems like the most logical approach.
AN
Annice
1 year ago
I think the key is to take an incremental, collaborative approach to help the organization understand and adopt Scrum effectively.
JO
Joanna
1 year ago
Ah, this is a classic firewall configuration question. I've seen these before, so I'm feeling pretty confident I can figure this out.