
 MENU

Refer to the exhibit, which shows an SD-WAN zone configuration on the FortiGate GUI. What can you conclude about the zone and member configuration on this device?
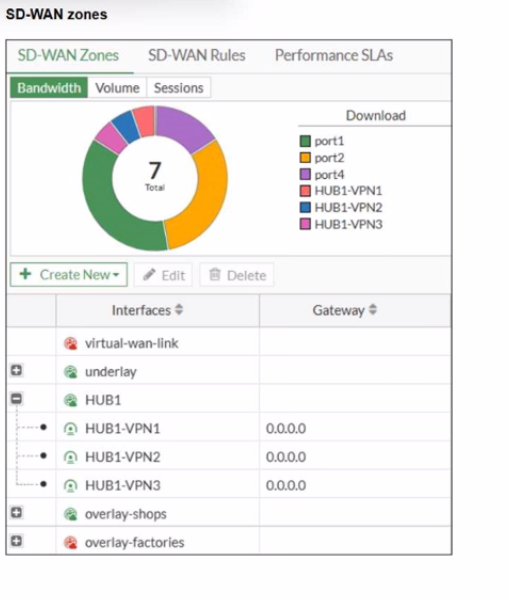
Exhibit 1
The WAN1 custom zone has no expansion indicator or visible subordinate member in the configuration screenshot, so it is the intended empty zone. WAN2 and HUB1 display expansion controls, indicating collapsed membership rather than a verified absence of members. The default virtual-wan-link zone is system-defined and cannot be treated like an ordinary removable custom zone. A zone can be deleted only when member assignments and other referencing configurations permit deletion. The candidate answer C reflects the intended screenshot interpretation, although the other statements must be assessed against the full configuration. Reference: FortiOS 7.6 --- SD-WAN Members and Zones. A deployment should preserve the distinction between the physical or logical WAN underlay, the IPsec overlay and the SD-WAN zone that groups forwarding members. These layers can have different routing and security-policy requirements. The configured architecture must also allow the required traffic paths and failover behavior rather than assuming every available interface is interchangeable.
Verification qualification: The empty-zone interpretation has a second technically possible action, so the item is ambiguous. Reference: https://docs.fortinet.com/document/fortigate/7.6.3/administration-guide/942095/sd-wan-members-and-zones
==========
Currently there are no comments in this discussion, be the first to comment!