
Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25
Welcome to Pass4Success

- Free Preparation Discussions

Fortinet NSE4_FGT_AD-7.6 Exam - Topic 1 Question 9 Discussion

Refer to the exhibit, which shows a partial configuration from the remote authentication server.Why does the FortiGate administrator need this configuration? (Choose one answer)
A) To authenticate only the Training user group.
B) To set up a RADIUS server Secret.
C) To authenticate and match the Training OU on the RADIUS server.
D) To authenticate Any FortiGate user groups.

Fortinet NSE4_FGT_AD-7.6 Exam - Topic 1 Question 9 Discussion

Actual exam question for Fortinet's NSE4_FGT_AD-7.6 exam
Question #: 9
Topic #: 1
[All NSE4_FGT_AD-7.6 Questions]

Refer to the exhibit, which shows a partial configuration from the remote authentication server.
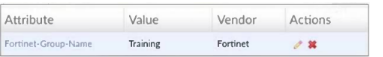
Why does the FortiGate administrator need this configuration? (Choose one answer)

Show Suggested Answer Hide Answer
Suggested Answer: A

''With this method, you must create a user group and add the preconfigured remote server to the group. This setup allows you to select one or more pre-existing groups from the Radius server, enabling any user within those groups to be authenticated.''

''The response from the server reports success, failure, and group membership details.''

''Note that Fortinet has a vendor-specific attributes (VSA) dictionary to identify the Fortinet-proprietary RADIUS attributes. This capability allows you to extend the basic functionality of RADIUS.''

Technical Deep Dive:

The attribute shown in the exhibit is Fortinet-Group-Name = Training. This is a Fortinet RADIUS Vendor-Specific Attribute (VSA) used to return group membership information to FortiGate. FortiGate uses that returned value to match the authenticated user to the corresponding FortiGate user group, in this case Training.

That is why A is correct: the administrator needs this so FortiGate can authenticate users and place or match them into the Training group for identity-based policy control.

Why the others are wrong:

* B is wrong because the RADIUS secret is configured separately as the shared secret between FortiGate and the RADIUS server, not as a Fortinet-Group-Name attribute.

* C is wrong because OU matching is an LDAP concept, not standard RADIUS group matching.

* D is wrong because this attribute is not for ''any'' group; it is explicitly returning the specific group name Training.

In practice, this lets FortiGate apply firewall policies such as:

```bash

config user group

edit 'Training'

set member 'RADIUS_Server'

next

end

```

Then the RADIUS server returns Fortinet-Group-Name=Training, and FortiGate matches the user into that group for policy enforcement.


Contribute your Thoughts:

0/2000 characters
Dominque
11 days ago
I agree with C. It aligns with RADIUS functionality.
upvoted 0 times
...
Mollie
16 days ago
C is the best choice. It ensures proper authentication.
upvoted 0 times
...
Stephanie
21 days ago
D seems too broad. Not specific enough.
upvoted 0 times
...
Michal
27 days ago
B makes sense for security. RADIUS secret is key.
upvoted 0 times
...
Daniela
1 month ago
I feel A is too limiting. Training group only?
upvoted 0 times
...
Gregoria
1 month ago
I think it's C. Matching the OU is crucial.
upvoted 0 times
...
Catarina
1 month ago
No way, it should cover all FortiGate user groups!
upvoted 0 times
...
Johnna
2 months ago
I think it's for setting up the RADIUS secret, right?
upvoted 0 times
...
Ryan
2 months ago
Wait, can it really only authenticate one group?
upvoted 0 times
...
Sanjuana
2 months ago
Definitely need to match the Training OU!
upvoted 0 times
...
Anika
2 months ago
This is all about RADIUS server settings.
upvoted 0 times
...
Vernice
2 months ago
But what if there are multiple groups? Wouldn't that complicate things?
upvoted 0 times
...
Vicky
2 months ago
Agree, it's all about authenticating that specific user group!
upvoted 0 times
...
Hobert
3 months ago
Wait, does it really need to match the OU? Sounds a bit off.
upvoted 0 times
...
Tracie
4 months ago
I think it's just to set up the RADIUS server Secret.
upvoted 0 times
...
Lovetta
4 months ago
It's definitely for the Training OU on the RADIUS server.
upvoted 0 times
...
Jin
5 months ago
I’m a bit confused; could it be option D since it mentions any user groups? That seems too broad though.
upvoted 0 times
...
Yaeko
5 months ago
I’m leaning towards option C because it mentions matching the Training OU, which seems important for authentication.
upvoted 0 times
...
Maryln
5 months ago
I remember a practice question that focused on RADIUS server settings, so I feel like option B might be relevant here.
upvoted 0 times
...
Hector
5 months ago
I think this configuration is about authenticating specific user groups, but I'm not sure if it's just for the Training group or something broader.
upvoted 0 times
...

Save Cancel