
 MENU

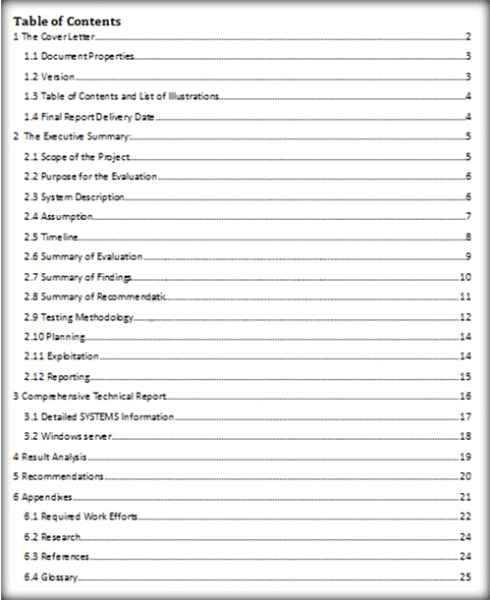
Which of the following pen testing reports provides detailed information about all the tasks performed during penetration testing?
Suggested Answer: A
Get Premium ECSAv10 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
13 comments · newest first
PA
Paulina
12 months ago
Client-Side Test Report is too narrow for this.
NA
Nancey
12 months ago
Wait, are we sure about that? Sounds off.
HE
Herminia
12 months ago
Definitely going with Activity Report for detailed tasks.
VI
Vilma
1 year ago
I think the Vulnerability Report is more comprehensive.
CY
Cyndy
1 year ago
The Activity Report usually has all the details.
TE
Tenesha
1 year ago
The Host Report seems too specific; I think it might not include all tasks. I’m leaning towards the Activity Report, but I’m still a bit confused.
AL
Aleta
1 year ago
I feel like the Client-Side Test Report could also provide detailed info, but I can't recall if it covers everything done during the test.
MY
Myra
1 year ago
I remember practicing a question about different types of reports, and I think the Vulnerability Report focuses more on findings rather than tasks.
MI
Minna
1 year ago
I think the Activity Report might be the one that details all the tasks performed, but I'm not entirely sure.
CE
Cecil
1 year ago
I remember learning about the NIST cloud computing model, but I'm drawing a blank on the specific details right now. I'll have to use my best guess and hope for the best. Maybe option B is the safest bet?
AB
Abel
1 year ago
Okay, I think I've got this. The key is to methodically go through each adjustment and apply it correctly to the starting cash balance. As long as I don't make any silly mistakes, I should be able to arrive at the right answer.
MA
Marion
1 year ago
I remember from our course that fraud reports need to be comprehensive but objective. I'm leaning towards answer A - avoiding technical jargon makes the report clearer.
SH
Shaquana
1 year ago
This seems like a straightforward question, but I want to make sure I understand the requirements correctly. I'll need to think through the different flow options carefully.