
 MENU

Identify the type of attack depicted in the following figure.
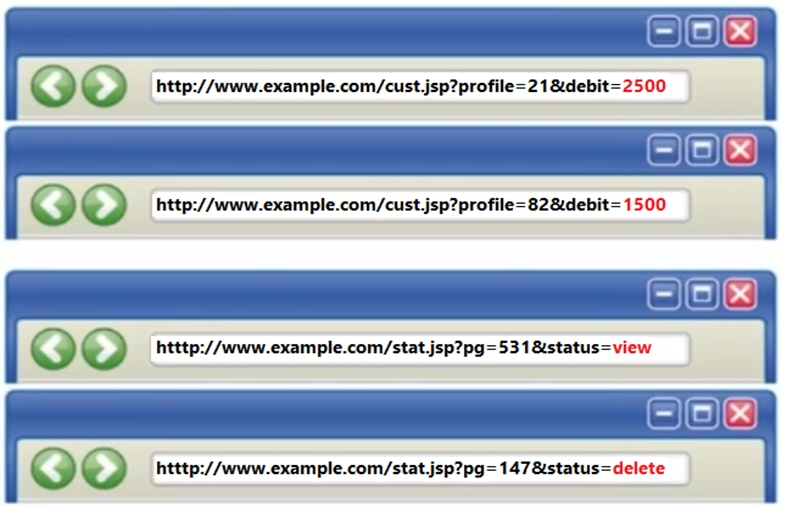
Suggested Answer: D
Get Premium 312-96 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
42 comments · newest first
TY
Ty
11 months ago
Wait, is that really an SQL Injection? I thought it was something else!
AL
Alica
11 months ago
Not so sure about that, could be Session Fixation too.
CH
Charlene
11 months ago
I think it's Parameter Tampering.
RA
Raymon
12 months ago
Definitely a Denial-of-Service Attack!
CA
Carmen
12 months ago
Looks like an SQL Injection to me.
DA
Darrin
1 year ago
I feel like I've seen a similar question before, and I think Session Fixation was the answer, but I could be mixing it up.
AN
Annice
1 year ago
Parameter Tampering sounds like a possibility, but I can't recall the exact characteristics that differentiate it from the others.
AL
Alisha
1 year ago
I remember practicing a question about Denial-of-Service attacks, but this doesn't seem to fit that description.
KR
Kristel
1 year ago
I think this might be an SQL Injection Attack, but I'm not entirely sure. The image looks familiar, though.
JE
Jenelle
1 year ago
I've seen this type of attack before. The URL structure and the options provided make me confident that this is a parameter tampering attack. I'll select that option and move on to the next question.
AN
Annelle
1 year ago
I'm a bit confused here. The image doesn't seem to match the options very well. I'll need to think this through step-by-step to make sure I don't miss anything.
SH
Shawn
1 year ago
Okay, based on the image and the options, I think this is a parameter tampering attack. The URL structure suggests user input is being passed directly to the application without proper validation.
LA
Lanie
1 year ago
Hmm, I'm not sure about this one. The image doesn't seem to depict a typical SQL injection scenario. Let me re-read the question and options more closely.
CH
Charlie
1 year ago
This looks like a classic SQL injection attack. I'll carefully analyze the image and the options to identify the correct answer.
TW
Twana
1 year ago
I dunno, but it kinda looks like they're trying to break the internet. Might as well start building a bunker, just in case!
BR
Brent
1 year ago
D) Denial-of-Service Attack
JU
Judy
1 year ago
C) Parameter Tampering Attack
MA
Malcolm
1 year ago
B) Session Fixation Attack
AL
Alyce
1 year ago
A) SQL Injection Attacks
PA
Pamella
1 year ago
D) Denial-of-Service Attack
CH
Charlie
1 year ago
C) Parameter Tampering Attack
SH
Sherron
1 year ago
B) Session Fixation Attack
MA
Malcolm
1 year ago
A) SQL Injection Attacks
VA
Vanda
1 year ago
Session fixation, for sure. I bet those hackers are trying to hijack someone's session. Gotta watch out for those sneaky attacks!
SU
Sunshine
1 year ago
D) Denial-of-Service Attack
GL
Gladys
1 year ago
C) Parameter Tampering Attack
PA
Paola
1 year ago
B) Session Fixation Attack
AN
Anjelica
1 year ago
A) SQL Injection Attacks
GE
Gene
1 year ago
Denial-of-service, all the way! Just imagine the chaos if that server goes down. Might as well go home early that day!
LA
Lauran
1 year ago
D) Denial-of-Service Attack
CA
Carlene
1 year ago
C) Parameter Tampering Attack
JO
Jonell
1 year ago
B) Session Fixation Attack
CU
Curtis
1 year ago
A) SQL Injection Attacks
KI
Kiley
2 years ago
Hmm, I'm not so sure. That image looks a bit suspicious to me. Could it be a SQL injection attempt in disguise?
LA
Lavonna
2 years ago
Looks like a classic parameter tampering attack to me. Messing with those query parameters can really mess things up!
YU
Yuki
1 year ago
Parameter tampering attacks can lead to serious security vulnerabilities if not addressed properly.
RY
Ryann
1 year ago
We need to make sure our input validation is strong to prevent these types of attacks.
ZA
Zana
1 year ago
I agree, it's definitely a parameter tampering attack. Those attackers are sneaky!
AN
Angella
1 year ago
Looks like a classic parameter tampering attack to me. Messing with those query parameters can really mess things up!
CE
Cecil
2 years ago
I'm not sure, but I think it could also be a Parameter Tampering Attack.
BE
Belen
2 years ago
I agree with Lachelle, the figure looks like a SQL Injection Attack.
LA
Lachelle
2 years ago
I think it's a SQL Injection Attack.