
 MENU

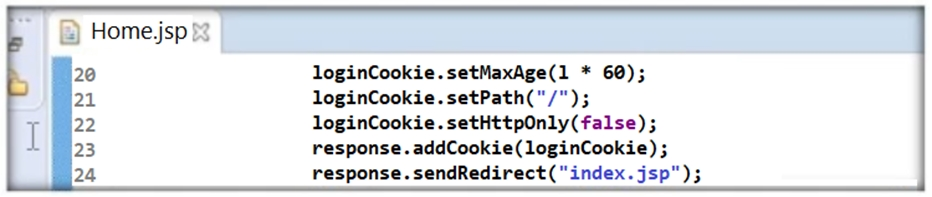
Thomas is not skilled in secure coding. He neither underwent secure coding training nor is aware of the consequences of insecure coding. One day, he wrote code as shown in the following screenshot. He passed 'false' parameter to setHttpOnly() method that may result in the existence of a certain type of vulnerability. Identify the attack that could exploit the vulnerability in the above case.
Suggested Answer: B
Get Premium 312-96 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
33 comments · newest first
AN
Antonio
11 months ago
I didn't know 'false' could cause such issues, wow!
EL
Elbert
11 months ago
Directory Traversal seems unlikely here.
SH
Sherron
11 months ago
Wait, are we sure it's not SQL Injection?
AI
Aileen
12 months ago
Totally agree, that's a classic vulnerability!
AL
Alysa
12 months ago
This could lead to a Client-Side Scripts Attack.
AL
Alberto
1 year ago
I'm a bit confused. I thought SQL Injection was more about database queries, not cookies. But I guess if the cookies are compromised, it could lead to other attacks?
PA
Pamella
1 year ago
I practiced a question similar to this, and I think it was about how not using HttpOnly can expose cookies to XSS attacks. So, I would lean towards option B.
SH
Sherell
1 year ago
I think if the HttpOnly flag is not set, it could allow for client-side scripts to access the cookies, which might lead to a Client-Side Scripts Attack.
AL
Alishia
1 year ago
I remember something about HttpOnly cookies being important for preventing client-side script attacks, but I'm not entirely sure how that connects to the options given.
WH
Whitley
1 year ago
Hmm, this is a tricky one. I'm a bit confused about the vulnerability mentioned, but I'll try to break it down step-by-step. I think the key is understanding how the setHttpOnly() method works and the potential consequences of passing a 'false' parameter.
CA
Cammy
1 year ago
Alright, time to put on my thinking cap. The code snippet doesn't seem to be related to SQL injection or directory traversal, so I'm going to rule those out. I'm leaning towards a client-side script attack, but I'll make sure to review the details carefully.
EM
Emelda
1 year ago
Hmm, this looks like a tricky one. I'll need to carefully analyze the code and the vulnerability mentioned to determine the correct attack type.
LO
Lou
1 year ago
Okay, let's see here. The question says Thomas passed a 'false' parameter to the setHttpOnly() method, which could lead to a vulnerability. I'm thinking this might be related to a client-side script attack, but I'll double-check that.
RO
Rosendo
1 year ago
Okay, let me think this through. Since vRealize Operations Manager is already in use for vSphere monitoring, I'm guessing we need to add some specific components for Horizon monitoring.
CO
Colette
1 year ago
Hmm, I'm a bit unsure about this one. The DITSCAP/NIACAP model has a lot of different phases, and I'm not entirely sure which one is focused on the accreditation process and ATO. I'll need to think this through carefully.
MA
Maile
2 years ago
SQL Injection? Directory Traversal? What is this, a video game boss fight? I think Thomas just unlocked the 'Insecure Coding' achievement. Time to start a new game and level up those secure coding skills!
JU
Justine
2 years ago
C) SQL Injection Attack
JA
Jani
2 years ago
B) Client-Side Scripts Attack
AR
Arlette
2 years ago
Client-side scripts attack is the correct answer here. Passing 'false' to setHttpOnly() means the session cookie won't be marked as HttpOnly, which leaves it vulnerable to client-side scripts. Thomas really needs to brush up on web security basics.
EL
Eladia
2 years ago
It's important to always be aware of potential vulnerabilities in your code.
GL
Glynda
2 years ago
Yes, you're right. Thomas should definitely learn more about secure coding.
CH
Charolette
2 years ago
I think the correct answer is B) Client-Side Scripts Attack.
JE
Jenelle
2 years ago
I believe the correct answer is B) Client-Side Scripts Attack because the code is not properly securing the HTTPOnly flag.
OR
Oren
2 years ago
Hmm, I'm not too sure about this one. Could it also be a denial-of-service attack? Either way, Thomas needs to learn about secure coding practices, and fast! Maybe he can try a 'Secure Coding for Dummies' book - it might be a good starting point.
HE
Helene
2 years ago
The code snippet shows that Thomas passed 'false' to the setHttpOnly() method, which could lead to a client-side scripts attack. That's a dangerous vulnerability that could allow attackers to steal session cookies and gain unauthorized access.
DE
Della
2 years ago
C) SQL Injection Attack
LA
Lavonda
2 years ago
B) Client-Side Scripts Attack
EL
Elke
2 years ago
A) Denial-of-Service attack
AS
Ashley
2 years ago
C) SQL Injection Attack
SH
Shannan
2 years ago
B) Client-Side Scripts Attack
LU
Luis
2 years ago
A) Denial-of-Service attack
VI
Vilma
2 years ago
I agree with Chantay, passing 'false' to setHttpOnly() method can lead to client-side scripts being able to access sensitive information.
CH
Chantay
2 years ago
I think the vulnerability in the code could be exploited by a Client-Side Scripts Attack.